The Key That Minted Billions: Tracing the ASI Alliance Exploit

September 23, 2026
EXECUTIVE SUMMARY
Between 19 and 20 September 2026, a linked attacker cluster abused privileged signing and minting authority across the Artificial Superintelligence Alliance ecosystem. Public incident analysis attributes the initial loss to a compromised SingularityNET bridge-authorizer key and a separately compromised NuNet minting key—not to a flaw in Ethereum consensus or a normal user-wallet compromise.
The most concrete liquid loss was 8,721,530.40162591 FET released from Fetch.ai's Ethereum conversion infrastructure. Unauthorized supplies of AGIX, NTX, WMTx and CGV were also created, but their face value must not be treated as realized proceeds: liquidity was too shallow to sell the entire counterfeit supply at quoted prices.
SentinelTX expanded three seeds into 857 addresses and 1,393 flows. Its case summary connected the two main attacker addresses through a shared gas funder, identified several exchange and bridge exposures, and showed that the primary wallet still held 433.045913 ETH at the initial profiling cutoff. The result establishes a broad operational cluster, but it does not identify the human operator.
HOW THE PRIVILEGED-ACCESS FAILURE WORKED
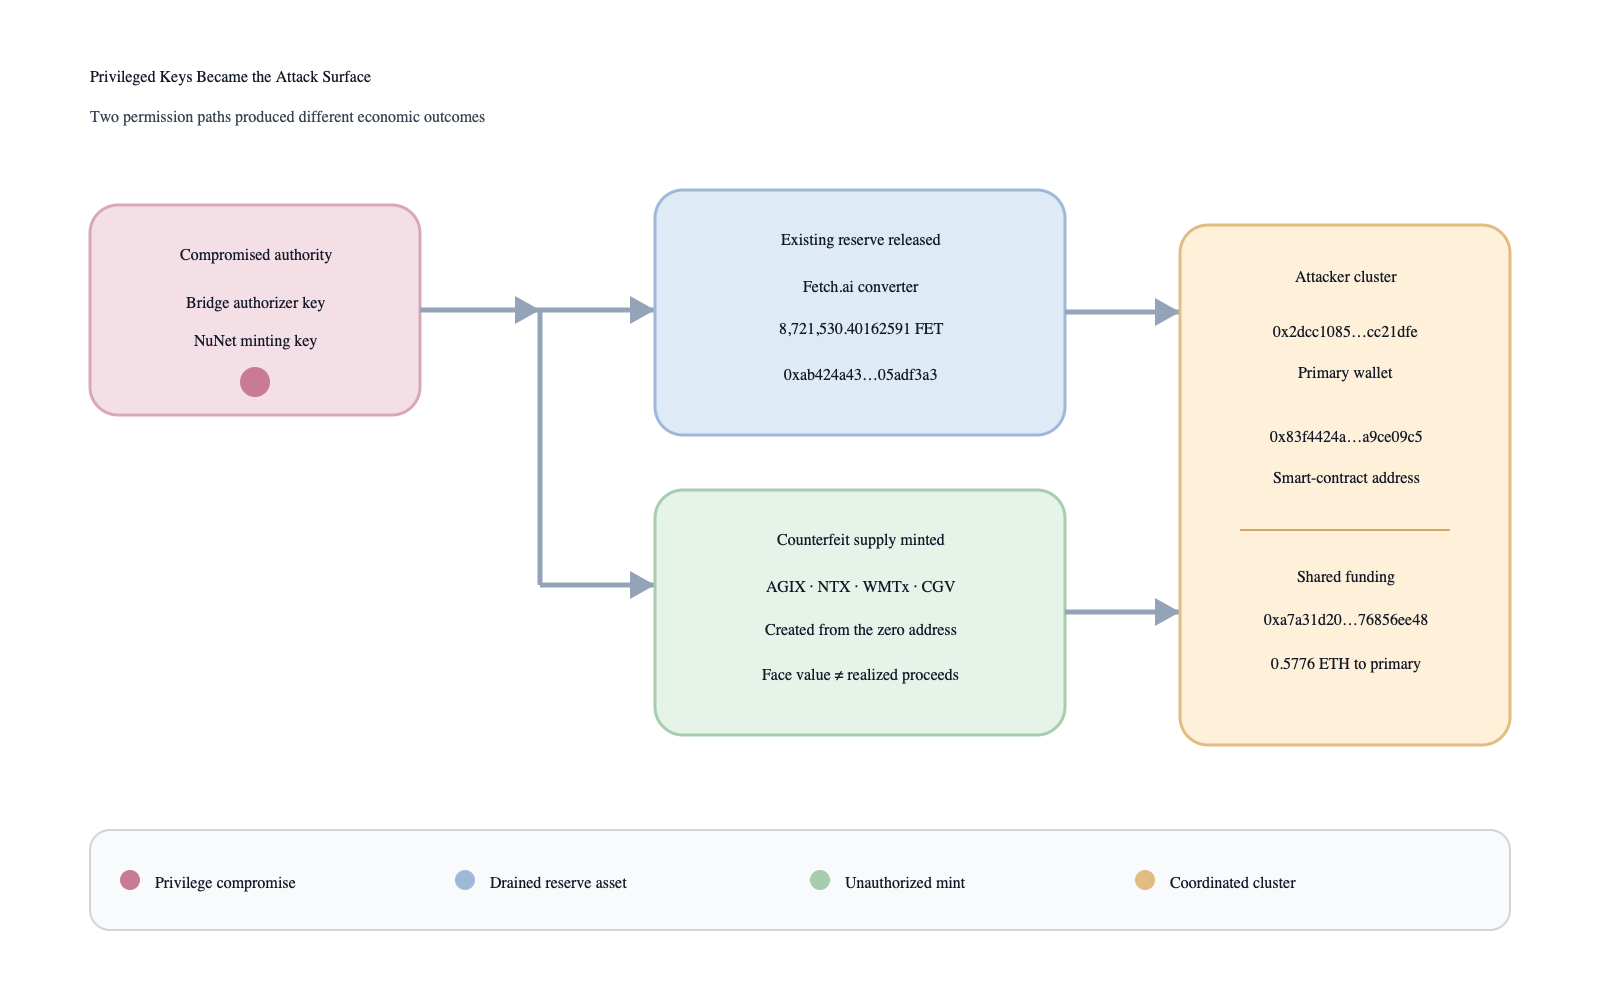
The incident combined two different privileged actions. First, a valid-looking authorization was used against Fetch.ai's TokenConversionManagerV3 to release existing FET. Separately, compromised mint authority created unauthorized token supplies directly from the zero address. The contracts executed the permissions they were given; the security failure was control of the privileged signing and minting keys.
The diagram below separates the liquid FET withdrawal from the later token mints. That distinction matters because drained reserve assets and newly created, illiquid supply have different economic effects.
CONFIRMED SEEDS AND INCIDENT ANCHORS
Item | Address / transaction | Type / value | Time / block | Evidence note |
Primary attacker | 433.045913 ETH; 192 outbound tx | Profiling cutoff | SentinelTX seed wallet | |
Second attacker | Smart contract | First active 20 Sep | Shared-funder cluster link | |
Fetch.ai converter | Verified contract | Public incident anchor | Contract role verified | |
FET withdrawal | 0xfe12c63b322d52727c615f3342222138d1563400a9880cebb516a9a162ac69e2 | 8,721,530.40162591 FET | Incident withdrawal | Public transaction anchor |
Earliest preview tx | 0x17627865473286a01045f485b664274123e59c48bc3e65cbab6347264b49843b | Preview transaction | Block 25,885,213 | Low-confidence “Poloniex Hack” endpoint lead |
Public on-chain research reports 408.53 million NTX, 260 million AGIX and 53.838 million WMTx minted without authorization. Those quantities describe counterfeit supply, not cash successfully realized by the attacker.
ONE OPERATING CLUSTER, NOT ISOLATED ADDRESSES
SentinelTX found a common funding wallet, 0xa7a31d206042b8a3e81aa4cf8c68c1b76856ee48, that supplied ETH to both main attacker addresses. It sent 0.5776 ETH to the primary wallet. Two additional wallets—0x1572f2af7696b39c85e3221cde8efb640f86c362 and 0x3196fd46b8e44a48722d0e8d042dbf28ad2ea1f9—also supplied ETH or NTX to the primary wallet.
This shared infrastructure is consistent with common control, but funding overlap is not proof of a real-world identity. The defensible conclusion is that the addresses operated as one coordinated on-chain cluster during the incident window.
WHERE THE MONEY TOUCHED SERVICES
SentinelTX's conversational case summary identified the following service exposures. They are useful intervention leads, but the free report preview does not disclose every full transaction hash or every hop. Each recipient and label should therefore be revalidated before a legal freeze request is sent.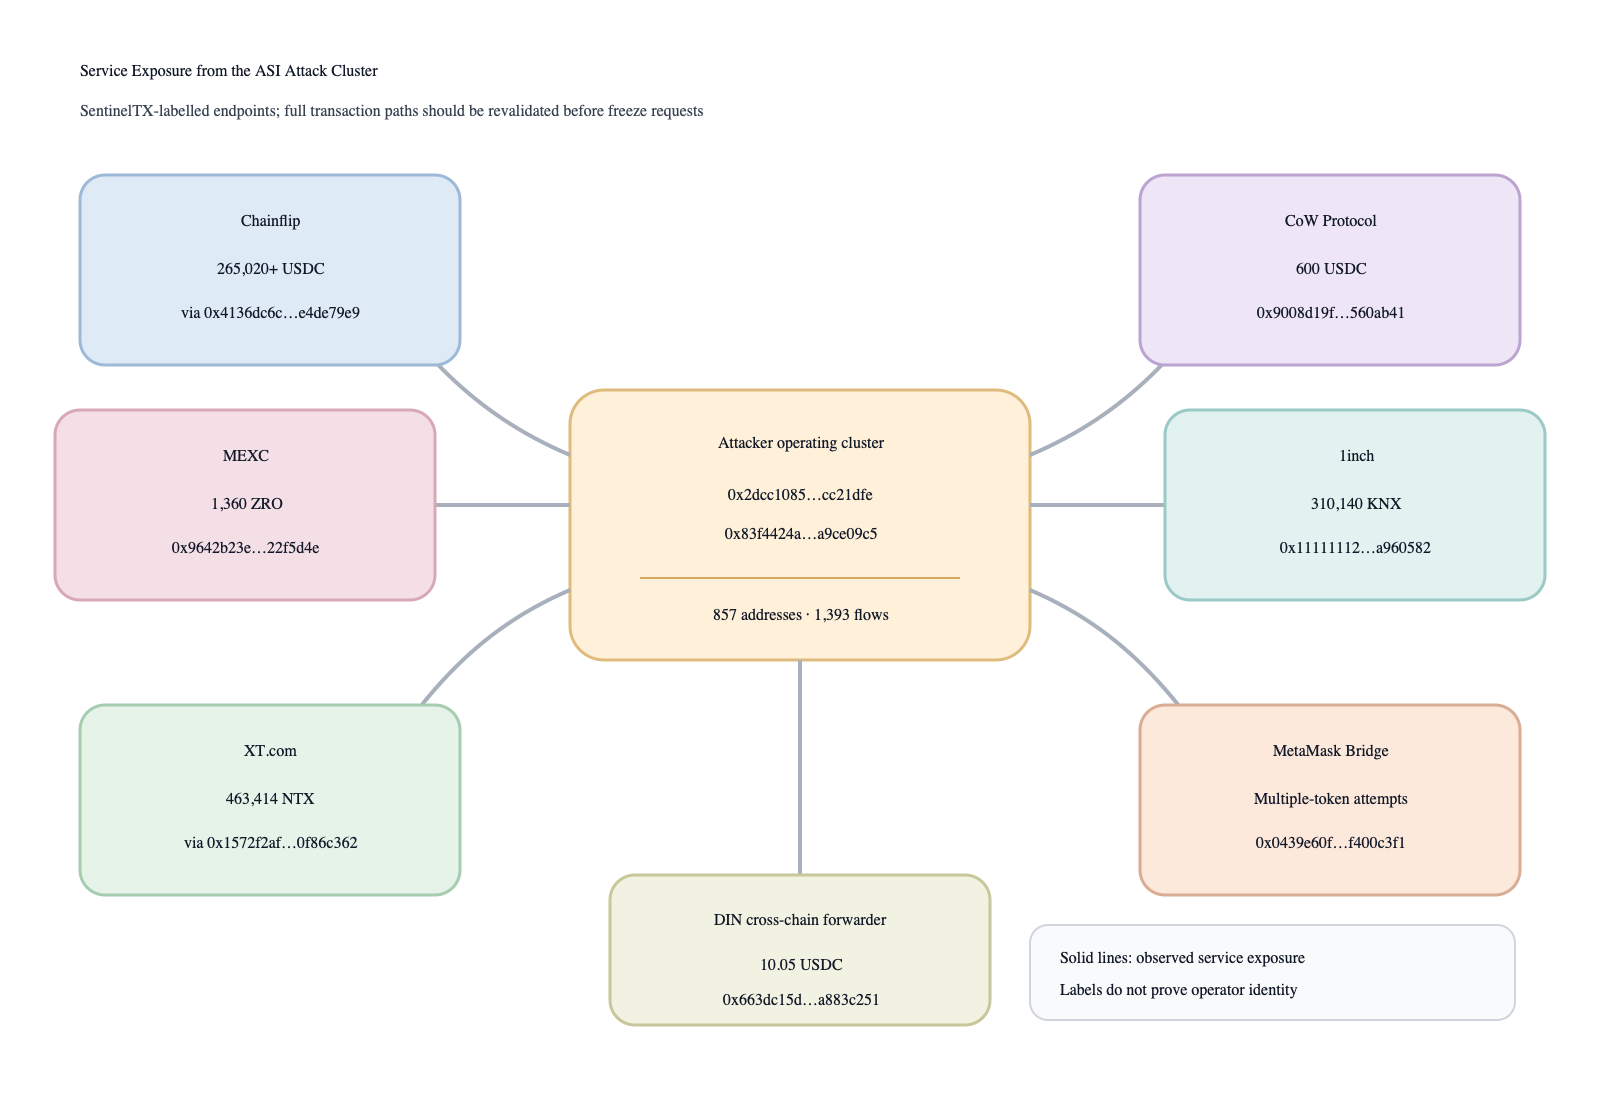
Secondary routing endpoints remain relevant but are not treated as final cash-out:
Service / route | Address | Observed activity | Classification |
CoW Protocol | 600 USDC | Routing endpoint | |
MetaMask Bridge | Multiple-token attempts | Bridge endpoint | |
DIN cross-chain forwarder | 10.05 USDC | Forwarding endpoint |
The report preview also displayed a low-confidence endpoint labelled “Poloniex Hack” receiving 860.69 USDT, 1.20 million FakeAI and another token. Because the attribution confidence is low and the full path is locked behind the detailed report, it should be treated as an investigative lead—not a confirmed exchange cash-out.
WHAT THE CHAIN PROVES—AND WHAT IT DOES NOT
The available evidence supports five conclusions:
1. Existing FET left the converter through a transaction anchored to the primary attacker wallet.
2. Large unauthorized token supplies were minted through privileged contract roles.
3. The two principal attacker addresses shared funding infrastructure.
4. The cluster interacted with labelled exchange, swap and bridge endpoints.
5. The primary wallet retained a substantial ETH balance at the profiling cutoff.
The evidence does not prove who stole the keys, whether every downstream wallet is controlled by the same person, or how much of the counterfeit supply was actually monetized. It also does not justify adding unsold token face values to liquid losses.
One inconsistency remains open. SentinelTX's conversational summary described the Fetch.ai converter as receiving and holding the same 8.721 million FET, while independent call-level reporting describes the contract releasing that amount to the attacker. The transaction trace should control; the “holding wallet” wording should not be repeated without reconciling the contract call and token-transfer direction.
INVESTIGATOR PRIORITIES
The first priority is preservation and freeze outreach to Chainflip, MEXC and XT.com using complete transaction paths—not abbreviated addresses. CoW, 1inch and bridge interactions should be preserved as routing evidence even when they are not final cash-out points.
The second priority is key-control reconstruction: bridge authorizer rotation, NuNet minter-role changes, deployer access logs, CI/CD secrets, cloud audit logs and acknowledgement timestamps. The shared funder should be examined for earlier deposits from labelled exchanges or infrastructure providers.
The third priority is live monitoring. The primary attacker wallet remained active through 21 September, and SentinelTX's report preview is based on Ethereum data through block 26,016,578 with the last transaction on 22 September. Any movement after that cutoff is a new evidentiary event.
CONCLUSION
This incident was not one token contract failing in isolation. A privileged-access compromise crossed multiple connected projects and turned trusted bridge and minting functions into attacker tools. The chain provides a strong operational cluster and several intervention points, while still leaving identity and final realized proceeds unresolved.
The clearest public claim is therefore narrow: compromised privileged keys enabled one material FET withdrawal and several unauthorized token mints; the attacker cluster shared funding infrastructure; and part of the liquid proceeds reached labelled services where preservation and KYC requests may still matter.
SOURCES AND METHODOLOGY
• SentinelTX case CASE-C5F23B38, investigated 23 September 2026. Graph: 857 addresses, 1,393 flows. Preview evidence: 429 of 882 addresses shown; on-chain cutoff block 26,016,578.
• Bitquery Research, “SingularityNET Hack Explained: AGIX, FET and NTX Minted,” 20 September 2026: https://bitquery.io/investigations/asi-bridge-counterfeit-supply
• Smart Contracts Hacking, incident record: https://smartcontractshacking.com/hacks/asi-alliance-singularitynet-hack-2026
• SingularityNET bridge documentation: https://dev.singularitynet.io/docs/products/Bridge/faq/
Service labels come from SentinelTX's threat-reputation and exchange attribution data. Labels indicate an investigative lead; they do not by themselves establish ownership, intent or legal liability.
SERVICE EXPOSURE APPENDIX
The four highest-priority intervention leads are organized below using the community editor’s native table. Labels are investigative leads and must be revalidated against complete transaction paths.
Endpoint | Observed exposure | Route / contract | Confidence | Investigator action |
Chainflip | 265,020+ USDC | High-priority lead | Revalidate tx path; freeze outreach | |
MEXC | 1,360 ZRO | Medium | Preservation and KYC request | |
XT.com | 463,414 NTX | High-priority lead | Revalidate complete route | |
1inch | 310,140 KNX | Routing only | Preserve swap evidence |
INCIDENT ANCHOR TABLE
Core wallets and transaction anchors are separated from service exposure so investigators can copy complete identifiers without mixing them with attribution labels.
Item | Address / transaction | Amount / activity | Evidence status | Investigator note |
Primary attacker | 433.045913 ETH | SentinelTX seed | 192 outbound tx | |
Second attacker | First active 20 Sep | Smart contract | Shared funder link | |
Fetch.ai converter | Verified contract | Public anchor | Reconcile transfer direction | |
FET withdrawal | 0xfe12c63b322d52727c615f3342222138d1563400a9880cebb516a9a162ac69e2 | 8,721,530.40162591 FET | Public tx anchor | Existing FET release |
CLUSTER FUNDING AND ATTRIBUTION TABLE
Funding overlap supports a coordinated on-chain cluster, but it does not identify the real-world operator.
Role | Address / transaction | Asset / amount | Connection | Confidence |
Shared gas funder | 0.5776 ETH to primary | Funded both main attackers | Strong cluster lead | |
Additional funder A | ETH / NTX funding | Primary wallet and XT.com route | Observed link | |
Additional funder B | ETH / NTX funding | Primary wallet | Observed link | |
Earliest preview tx | 0x17627865473286a01045f485b664274123e59c48bc3e65cbab6347264b49843b | 860.69 USDT + 1.20M FakeAI | Low-confidence endpoint label | Investigate only |
 0
 0
67 조회
 조사관 신청하기