FlashLoopAdapter: 114 ETH Extracted Through Module Authority, Then Shielded Across a Fee Boundary

October 05, 2026
Investigation Findings
Executive Summary
On 1 October 2026, a third-party FlashLoopAdapter enabled execution from two Safe accounts. The exploit transaction delivered 114.096151469674448809 ETH to the initiating EOA. The evidence points to delegated module authority, not an exploit of Aave V3 core. SlowMist primary analysis and clarification.
The strongest downstream finding is an exact fee split: 114.030726169100264326 ETH was wrapped, 113.745649353677513666 WETH entered the RAILGUN privacy-system proxy, and 0.285076815422750660 WETH went to the protocol treasury. The visible route ends at that privacy boundary; it does not identify a hidden recipient or prove an exchange cash-out.
Measure / scope | Verified result |
|---|---|
Exploit proceeds received | 114.096151469674448809 ETH; counted once |
Private-pool transfer | 113.745649353677513666 WETH |
Treasury fee | 0.285076815422750660 WETH |
Scope | Ethereum; focused funding and outbound route |
Investigation cutoff | 4 October 2026, 23:32:47 UTC; block 26122303 |
Evidence basis | SentinelTX call traces and receipts, independently checked Etherscan anchors, SlowMist primary analysis |
Core finding | What establishes it |
|---|---|
Delegated authority | Victim-emitted module success logs 1023 and 1030 |
Exact extraction accounting | Receipt logs separate collateral, repaid debt, returned loan and ETH proceeds |
Privacy boundary | Shield receipt separates private-pool transfer and protocol fee |
Finding 1 — How Did the Safe Accounts Execute Without Owner Signatures?
The question is not whether a wallet signed the initiating transaction—it did—but whether the victims’ owners signed the Safe executions that removed assets. The traced exploit used module executions. No owner-signed Safe execution was observed in the inspected call tree.
Observed call relationship | Evidence / interpretation |
|---|---|
Adapter → victim Safe 1 | Module execution targeting weETH transfer |
Adapter → victim Safe 2 | Module execution targeting lending-pool withdrawal |
Adapter → execution helper | Additional module execution frames naming the helper as the Safe |
Coverage boundary | 259 frames reported; 134 returned by the trace tool—not a complete replay |
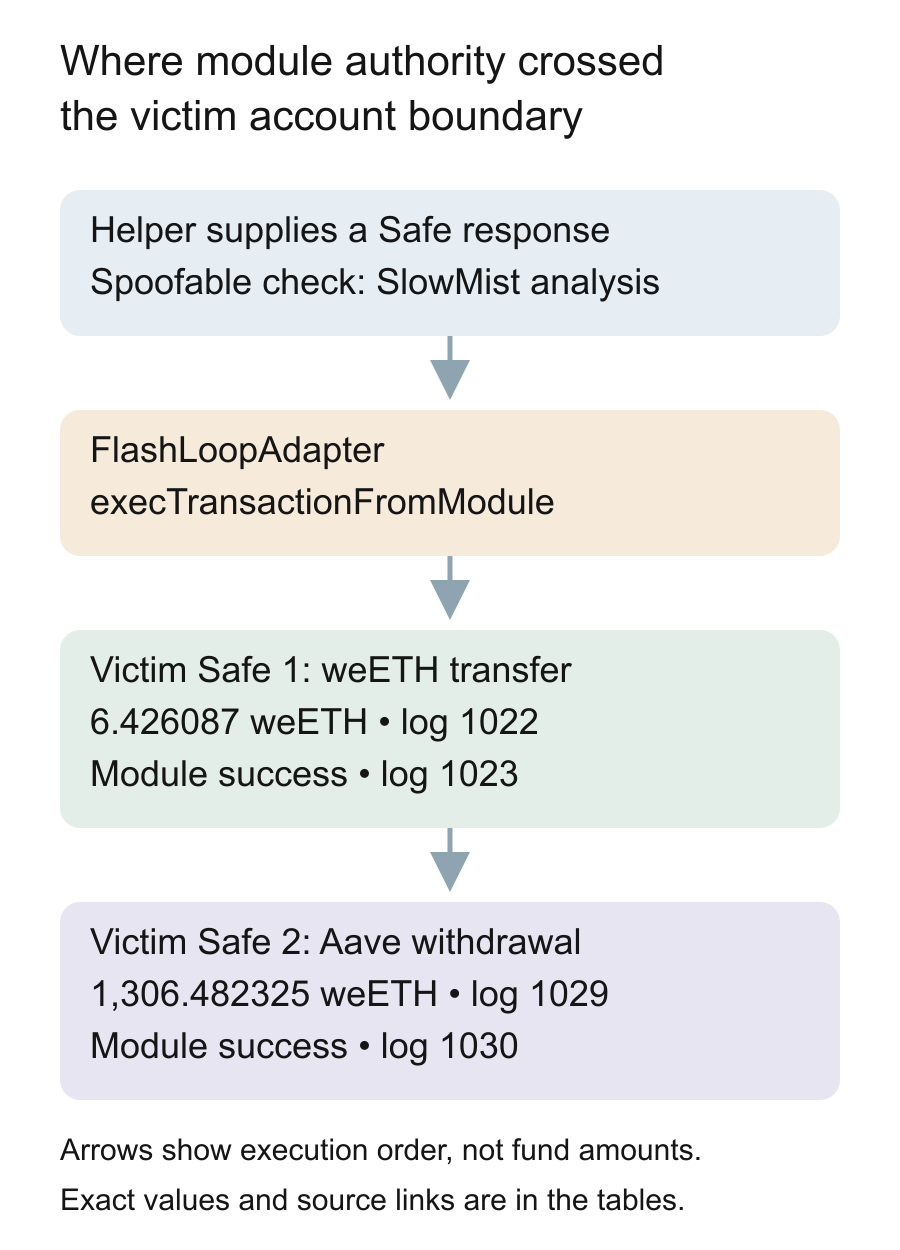
SlowMist reports that open()/close() checked ISafe(msg.sender).isModuleEnabled(address(this)), allowing a fake caller to answer its own authentication check. It then describes attacker-controlled router.call data targeting genuine victim Safes through execTransactionFromModule. This source-level explanation is attributed research; our call-trace evidence supports the module-execution route, but we did not independently compile or replay the adapter. SlowMist primary analysis and clarification. 0x75328f916b1a0878724d364da5eb12b255160b894cb36c63ed5d718efc616fc4.
Receipt corroboration — two victim-emitted success events
Both victim Safe contracts emitted ExecutionFromModuleSuccess naming the same adapter. Log 1023 follows the first victim’s weETH Transfer; log 1030 follows the second victim’s Aave withdrawal. These events independently corroborate the module route beyond the partial call trace. They establish successful execution by the named module, but do not by themselves reconstruct the caller’s authorization check or the owners’ earlier decision to enable it. Exploit receipt: decoded event logs.
The implication is a separate authorization boundary: enabling a module grants executable authority beyond the ordinary owner-signature path. SlowMist explicitly clarified that Aave V3 core was unaffected. The current enabled-module lists and the complete set of exposed Safes were not enumerated; two observed victims are not a total exposure count.
Finding 2 — Which Amount Is the Loss, and Which Is Reused Liquidity?
The exploit receipt and internal movements show WETH unwrapped into the execution helper and then paid to the attack EOA. Those two legs describe the same 114.096151469674448809 ETH and must be counted once. 0x75328f916b1a0878724d364da5eb12b255160b894cb36c63ed5d718efc616fc4.
Quantity | Classification | Evidence boundary |
|---|---|---|
114.096151469674448809 ETH | Exploit proceeds received | Exact internal transfer |
11,537.239738536922710940 WETH | Morpho loan and matching return | Exact logs 1014–1015 and 1059; returned liquidity |
1,335.255802777509633370 WETH | Debt repayment | Exact Repay event for victim Safe 2, log 1021 |
1,449.351954247184082179 WETH | Swap output | Exact WETH transfer to helper, log 1058 |
The large flash loan provides temporary liquidity for repayment and collateral release. It was returned, so counting it as stolen funds would inflate the incident by two orders of magnitude. Proceeds received are also not necessarily each victim’s gross collateral loss: debt repayment changes the net economic calculation. The receipt now establishes each victim’s exact token movements. A single ETH-denominated loss for each victim still requires an explicit weETH valuation basis and account-state reconciliation.
Subtracting only exploit-transaction gas gives 114.092231045147641069 ETH. That is an arithmetic subtotal, not an all-in profit claim: deployment costs, forwarding costs and other activity are not completely reconciled.
Victim Safe 1 — direct token removal
The first victim transferred 6.426087021311600894 weETH directly to the execution helper in log 1022. Its own module-success event follows in log 1023. This is an exact token outflow; it must not be relabeled as 6.426087 ETH or added to a WETH figure without a conversion basis. Exploit receipt: decoded event logs.
Receipt item | Exact result |
|---|---|
Victim | Safe 1; full account address in evidence appendix |
weETH outflow | 6.426087021311600894 weETH |
Transfer evidence | Log 1022; victim → execution helper |
Module execution | Log 1023; adapter named by victim |
Victim Safe 2 — collateral removal after debt repayment
The helper paid 1,335.255802777509633370 WETH against Safe 2’s debt. The Pool Repay event identifies both that victim and the helper as repayer. The Pool then records withdrawal of 1,306.482324969756972729 weETH for Safe 2 to the same helper; the token Transfer corroborates it. Gross collateral removed and debt extinguished are economically different legs. Exploit receipt: decoded event logs.
Receipt item | Exact result |
|---|---|
Debt repaid for Safe 2 | 1,335.255802777509633370 WETH; logs 1020–1021 |
Collateral delivered to helper | 1,306.482324969756972729 weETH; logs 1027 and 1029 |
aToken burn value | 1,306.482262583889567736; log 1026 |
Accrued balance increase | 0.000062385867404993; log 1026 |
Module execution | Log 1030; adapter named by victim |
The aToken burn value plus its logged balanceIncrease equals the underlying weETH withdrawal exactly. Counting the burn, Transfer and Withdraw as three losses would triple-count the same collateral leg. The debt-token Burn likewise separates 1,329.536830578102452349 from 5.718972199407181021 of balance increase; together they equal the 1,335.255802777509633370 WETH repayment. These are receipt reconciliations, not independent cash movements.
Helper accounting — why the flash loan cancels out
Helper WETH leg | Exact amount / receipt |
|---|---|
Morpho loan in | 11,537.239738536922710940 WETH; logs 1014–1015 |
WETH debt repayment out | 1,335.255802777509633370 WETH; logs 1020–1021 |
WETH swap output in | 1,449.351954247184082179 WETH; log 1058 |
Morpho loan returned | 11,537.239738536922710940 WETH; log 1059 |
WETH unwrapped | 114.096151469674448809 WETH; log 1060 |
The matching loan-in and loan-return cancel. Swap output minus debt repayment equals 114.096151469674448809 WETH exactly, matching the withdrawal event and subsequent ETH receipt. This explains the observed extraction without treating temporary liquidity as incident loss. The helper also retained approximately 0.008411991 weETH in the explorer’s rounded token overview; it is excluded from the exact ETH subtotal because that overview is not an exact balance proof. Exploit receipt: decoded event logs.
Combined execution and settlement map
This supplementary overview connects the module-execution boundary with both collateral outflows and helper settlement. The dashed paths represent authority calls; the dotted path is a repayment prerequisite, not a token transfer. Solid paths show selected asset movements. The flash-loan return is shown separately from extracted proceeds.
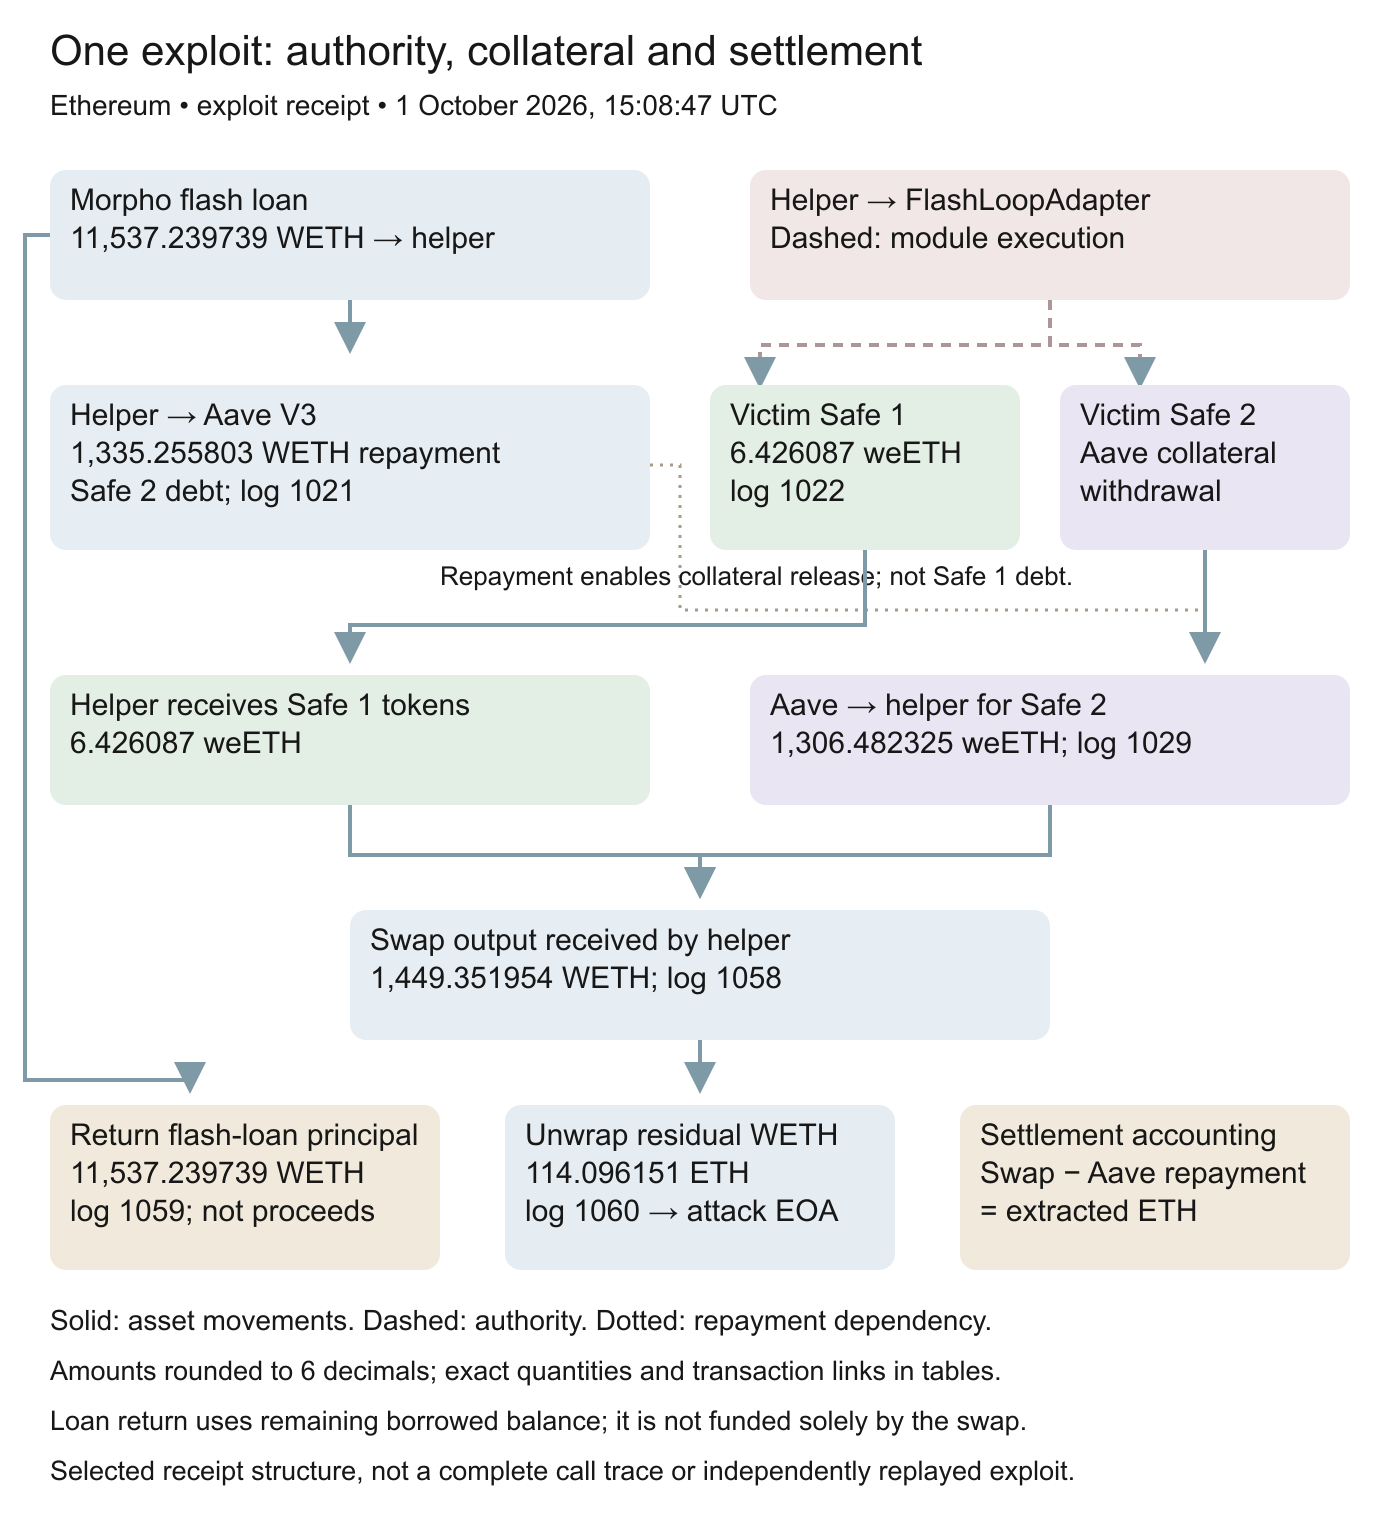
The diagram rounds amounts to six decimals. The native receipt tables preserve exact quantities; it does not convert weETH into ETH one-for-one or claim a complete execution trace.
Finding 3 — What Actually Entered the Private Pool?
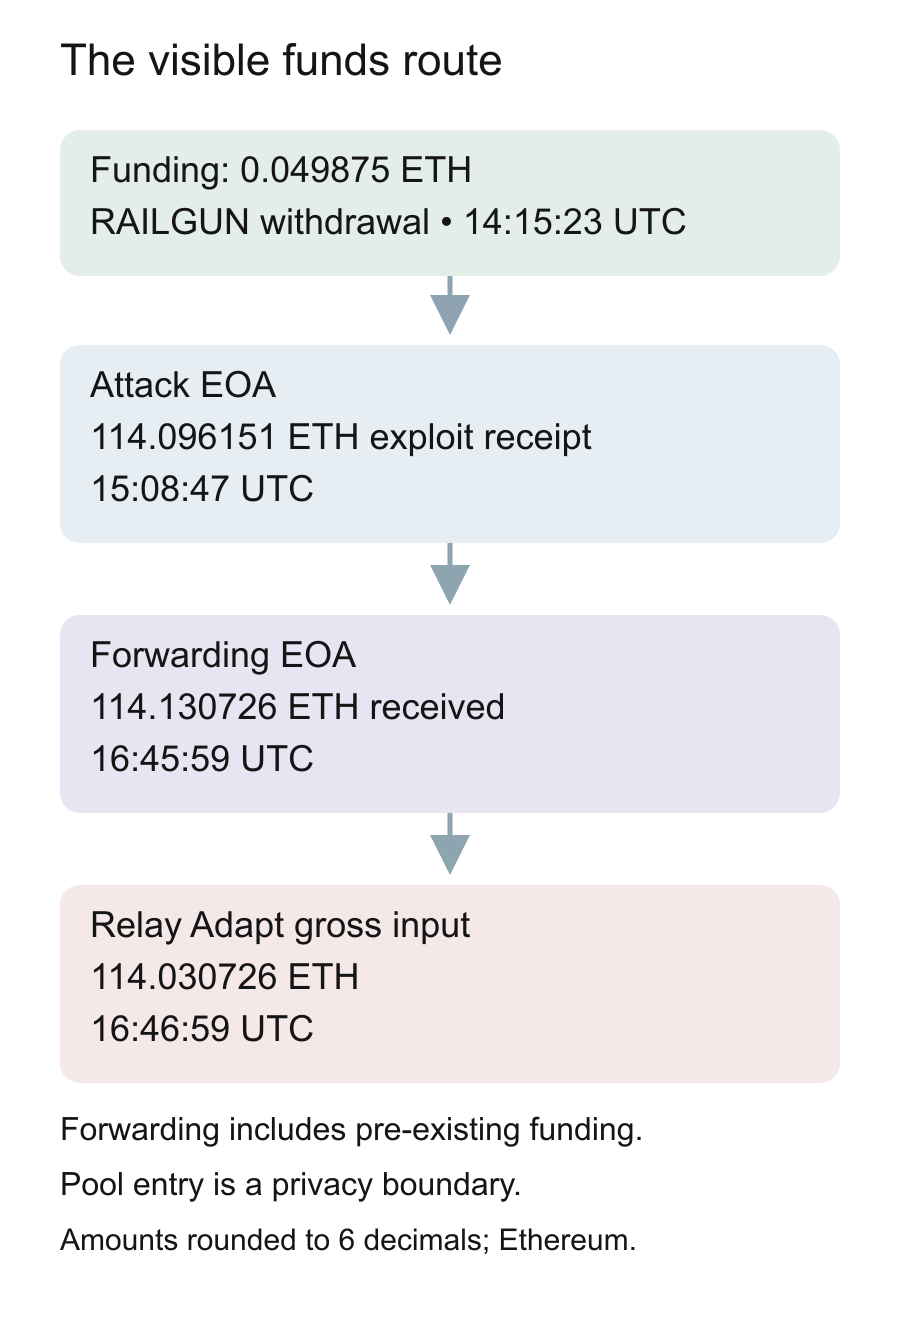
The forwarding transfer is larger than the exploit receipt because the EOA had pre-existing funding. It cannot be treated as an exclusively stolen-funds figure. The next transaction converts the gross ETH input to WETH and divides it between the privacy-system proxy and treasury. 0x3a5663d9a3d32bdea3c3012fd9dbaf490195ed413204c4db8f1097e1e7f753f9. 0xa20636bf3792f705ae51a48afdec336fb0518cd43365a8fc3e596dea23266dc9.
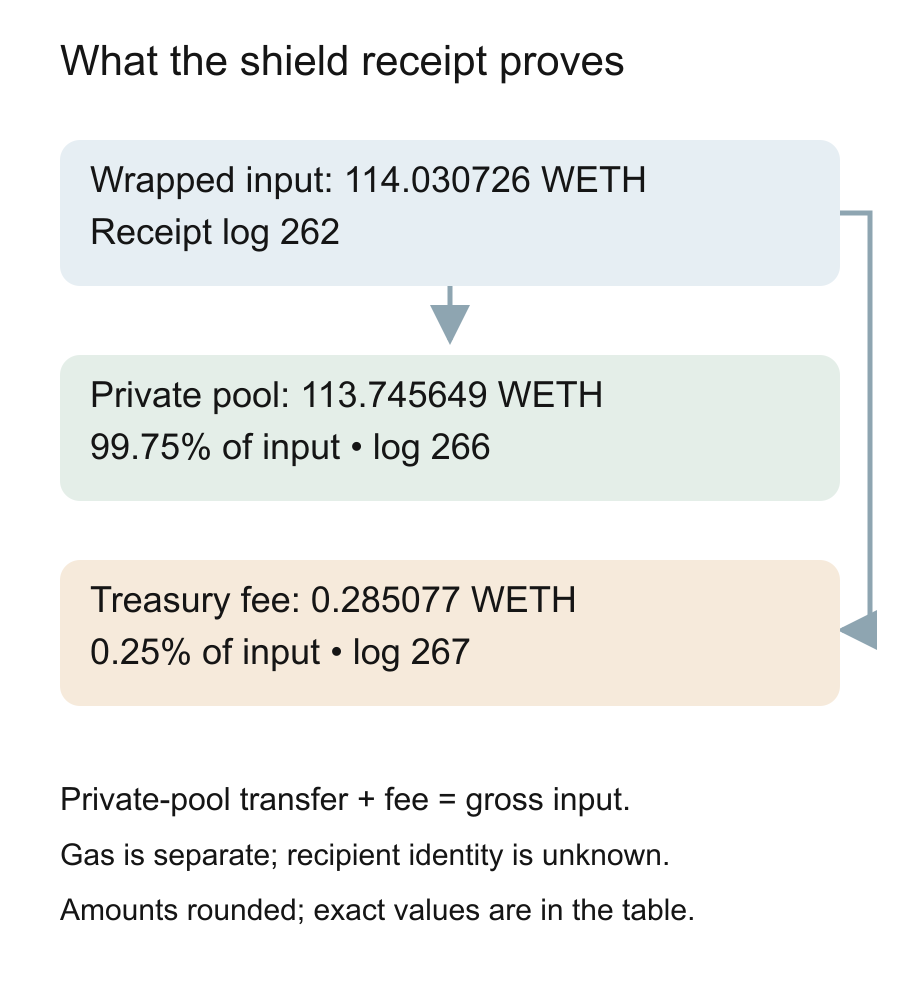
Shield receipt leg | Exact WETH | Log |
|---|---|---|
Wrapped input | 114.030726169100264326 | 262 |
Transfer to privacy-system proxy | 113.745649353677513666 | 266 |
Transfer to treasury | 0.285076815422750660 | 267 |
Shield event | Supports the amount / fee split | 268 |
The allocation chart below uses a shared linear WETH scale. The fee bar is intentionally tiny: enlarging it without a separate scale would misrepresent the 0.25% allocation. Chart labels are rounded to six decimals; the native table above preserves the full values and receipt indices.
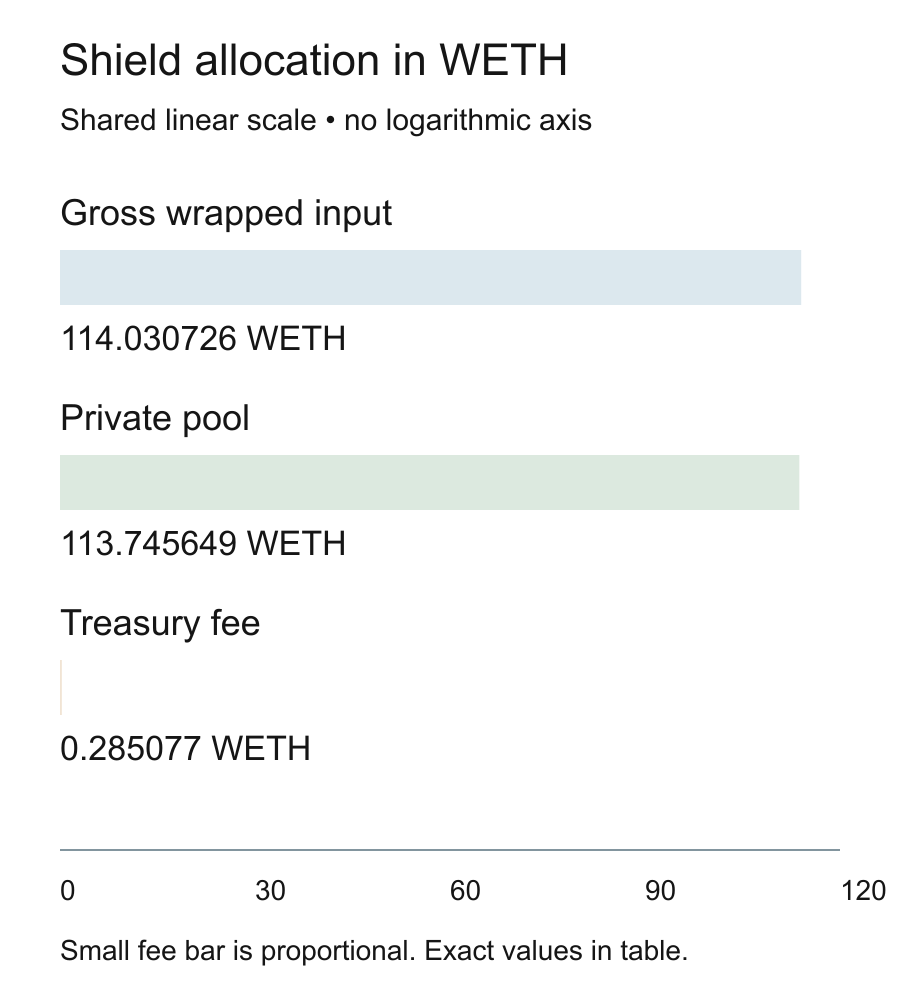
The two transfers sum exactly to the wrapped input. The treasury fee is 0.25% rounded down at token precision; transaction gas of 0.001793902352363730 ETH is separate. The treasury leg is a protocol fee—not evidence of cash-out, common ownership, or a recovery target. We independently checked these visible Etherscan logs against the SentinelTX follow-up result.
Timeline — Funding, Execution and Disposition
All times below are UTC on 1 October 2026. These are selected transaction anchors, not a claim that every intervening transaction has been accounted for.
UTC / block | Event | Amount |
|---|---|---|
14:15:23 / 26098000 | RAILGUN withdrawal funds attack EOA | 0.049875 ETH net received |
15:08:47 / 26098264 | Exploit helper pays attack EOA | 114.096151469674448809 ETH |
16:45:59 / 26098748 | Attack EOA forwards to intermediate EOA | 114.130726169100264326 ETH |
16:46:59 / 26098753 | Intermediate EOA sends Relay Adapt input | 114.030726169100264326 ETH |
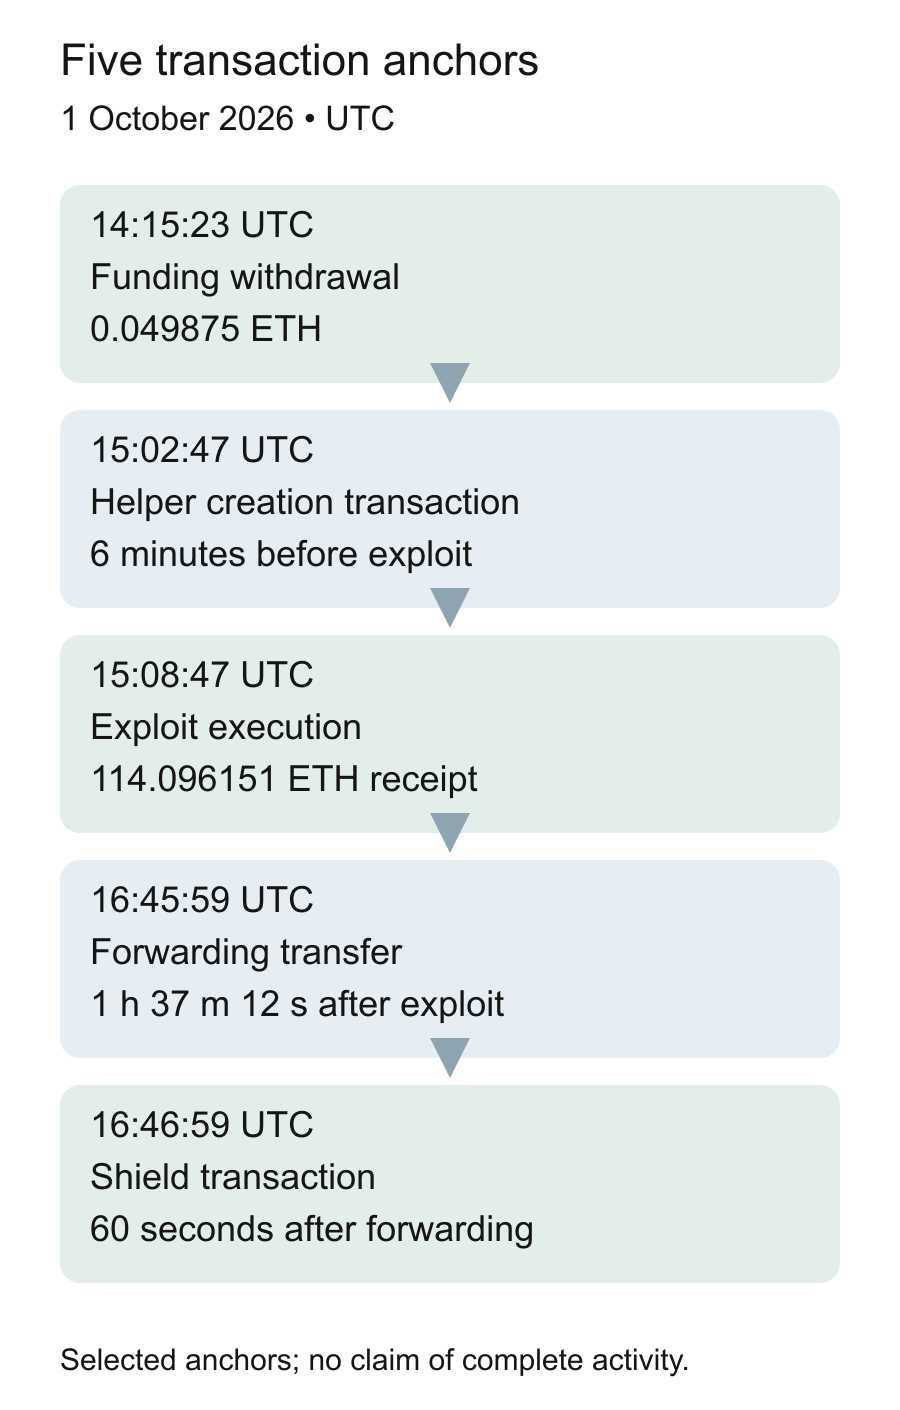
Funding to exploitation took 53 minutes 24 seconds. The creation transaction preceded exploitation by six minutes; forwarding followed exploitation by 1 hour 37 minutes 12 seconds, and shielding followed forwarding by 60 seconds. These measured intervals are consistent with a prepared execution sequence, but do not identify a person or prove coordination with any service operator.
Helper creation — a direct infrastructure anchor
The creation transaction at block 26098235, 1 October 2026 15:02:47 UTC, was signed by the same initiating EOA and sent to a separate contract; the explorer identifies the helper as created within that transaction. This establishes a transaction-level infrastructure link. It does not justify calling the EOA the direct CREATE caller without inspecting the creation call frame. 0x0c2bbaf2b5ebf1102e0df4acb1bcc2c7bc920896c45da6f85b4e9442506a3884.
Creation anchor | Observed result |
|---|---|
Transaction signer | |
Transaction target | |
Created helper | |
UTC / block | 2026-10-01 15:02:47 / 26098235 |
Creation transaction | 0x0c2bbaf2b5ebf1102e0df4acb1bcc2c7bc920896c45da6f85b4e9442506a3884 |
Wallet network — how the public route connects
The account-level overview below joins the victim collateral legs with the directly observed outbound route. V2 collateral is delivered by the Aave token contract, not by a direct Safe token transfer. The funding origin is a separate earlier privacy-service withdrawal; using the same public infrastructure does not prove a shared hidden owner. Exact transaction anchors remain in the evidence appendix.
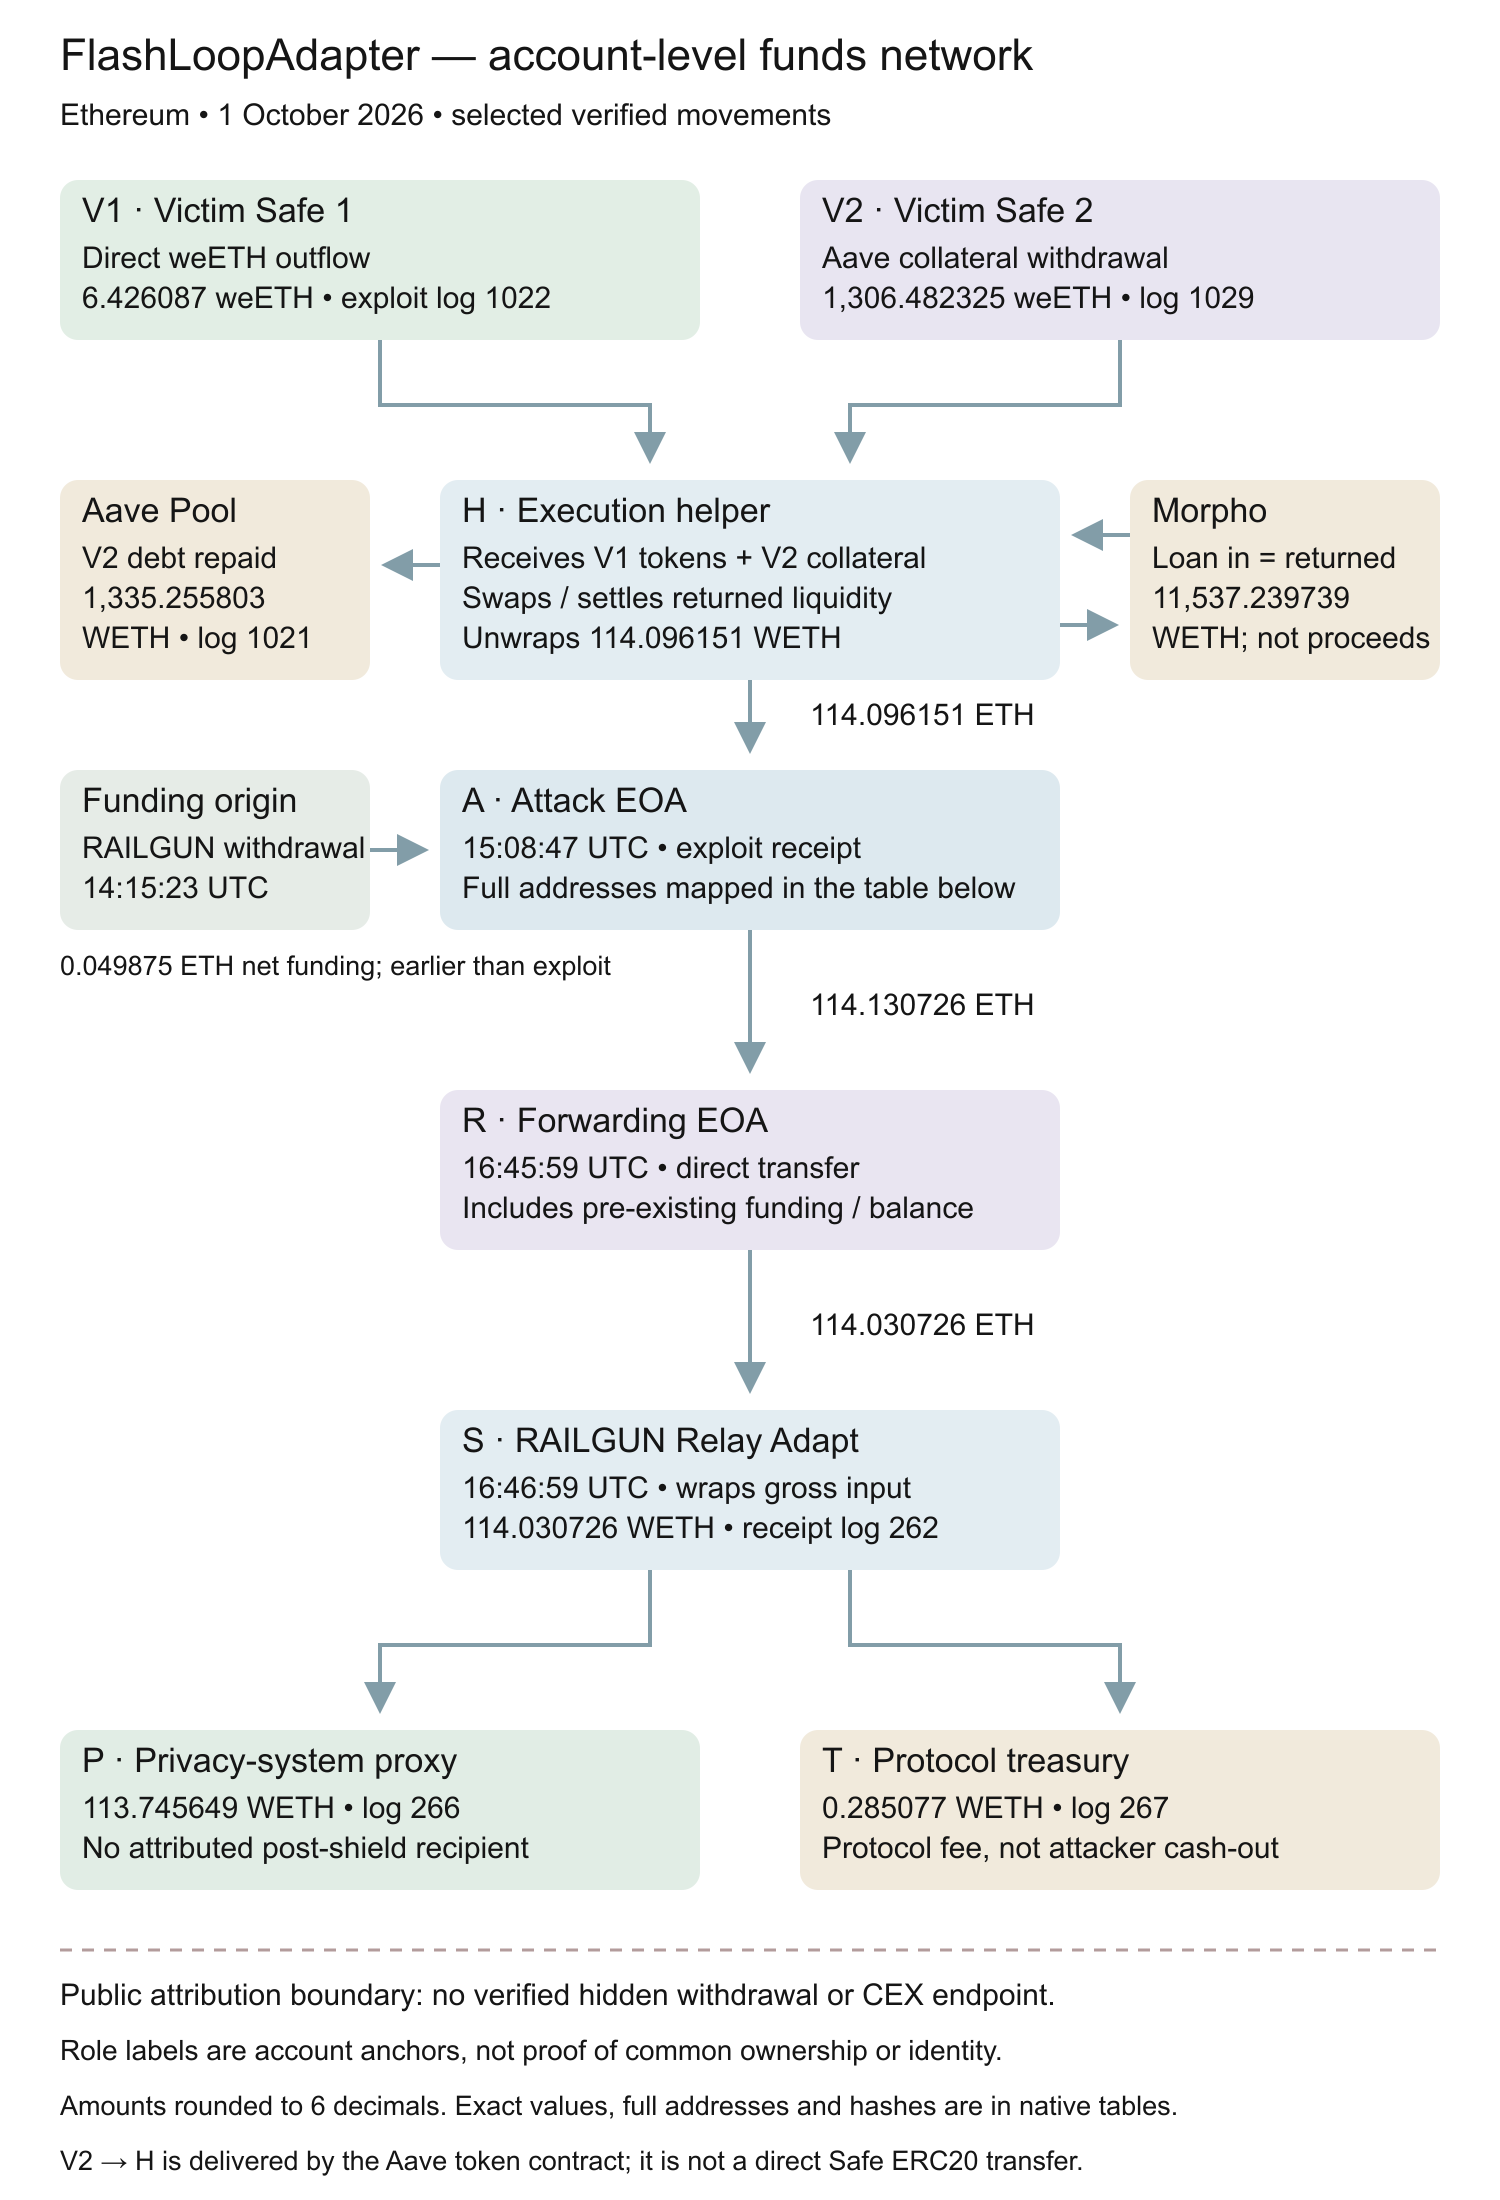
Diagram node | Full Ethereum account / contract |
|---|---|
V1 · Victim Safe 1 | |
V2 · Victim Safe 2 | |
H · Execution helper | |
A · Attack EOA | |
R · Forwarding EOA | |
S · Relay Adapt | |
P · Privacy-system proxy | |
T · Protocol treasury | |
Aave Pool | |
Morpho flash lender |
The role-labelled nodes are verified account or contract anchors, not a common-owner cluster. The 114.130726 ETH forwarding transfer exceeds the exploit receipt because it includes pre-existing balance. Relay Adapt wraps 114.030726 ETH, then the receipt splits WETH between the privacy-system proxy and treasury. The treasury payment is a protocol fee, not attacker cash-out. No verified edge continues from the private pool to a hidden withdrawal or exchange.
Connection Evidence — Direct Transfers Are Not Identity Evidence
A same-transaction call chain directly connects the initiating EOA, helper, adapter and victim executions. Two later transaction hashes directly connect the initiating EOA to the forwarding EOA and Relay Adapt. These are transaction relationships, not human attribution.
Proposed connection | Evidence level | Conclusion |
|---|---|---|
Attack EOA → helper → adapter → victims | Direct inspected call trace | Execution relationship established |
Attack EOA → forwarding EOA → RAILGUN | Direct value transfers | Visible disposition route established |
Funding withdrawal and shield use same public service | Shared service pattern | Does not establish hidden owner continuity |
Similar-looking addresses | Potential poisoning | Do not merge into attacker cluster |
Post-shield withdrawal of similar size | Heuristic only | Amount / timing alone cannot attribute funds |
Limits and Alternative Interpretations
The traced scope is Ethereum. Two reported Optimism activities were not inspected. The exact exploit receipt and helper creation transaction were checked in this revision. Adapter source code, a complete replay, incident-block module lists, the precise CREATE caller and each victim’s pre/post account valuation remain unestablished. Historical owner/setup claims from the first automated result were withdrawn in the follow-up and are not used here.
The RAILGUN funding-transaction signer may be an independent relayer. Shared public infrastructure does not identify an operator. No exchange endpoint was identified in the inspected routes; that is narrower than proving no exchange cash-out occurred. The private-pool transfer cannot be followed to a particular hidden withdrawal using these public records alone.
Visible noncustodial EOA balances are not automatically freezeable. We also do not describe the helper’s deployment as the only remaining lead: unexamined histories, module exposure and alternate infrastructure remain separate questions.
Incident-Specific Response Points
Question | Practical investigation action |
|---|---|
Which Safes retain this authority? | Enumerate adapter-enabled Safes and incident-block module lists; validate current exposure before remediation |
How much did each victim lose net of debt? | Use the exact receipt legs established here; reconcile pre/post positions and a documented weETH valuation basis |
Was infrastructure reused? | Inspect the creation call frame and transaction target history; the signing EOA is now directly linked to helper creation |
Can downstream funds be attributed? | Treat pool exit matches as leads; require independent evidence before attribution or exchange requests |
For affected account operators, the relevant control is the specific module’s execution authority. A verified vulnerable-module exposure warrants targeted module revocation and preservation of account state and receipts. This is distinct from a blanket assertion that Safe or Aave core is compromised.
Evidence Appendix — Ethereum Account Anchors
Role | Full address |
|---|---|
Attack EOA | |
Execution helper | |
Third-party adapter | |
Victim Safe 1 | |
Victim Safe 2 | |
Forwarding EOA | |
RAILGUN Relay Adapt | |
RAILGUN privacy-system proxy | |
RAILGUN Treasury |
Evidence Appendix — Contract and Asset Anchors
Role | Ethereum address |
|---|---|
weETH token | |
WETH token | |
Aave Pool V3 | |
aEthweETH token | |
Variable debt WETH token | |
Morpho flash lender | |
Helper creation transaction target |
Evidence Appendix — Transaction Anchors
Role | Full transaction hash |
|---|---|
Helper creation | 0x0c2bbaf2b5ebf1102e0df4acb1bcc2c7bc920896c45da6f85b4e9442506a3884 |
Funding withdrawal | 0xc5dc2606e42ebfad29fce601056248b9b3f3571318c9a0de2910ac7c0363852b |
Exploit | 0x75328f916b1a0878724d364da5eb12b255160b894cb36c63ed5d718efc616fc4 |
Forwarding | 0x3a5663d9a3d32bdea3c3012fd9dbaf490195ed413204c4db8f1097e1e7f753f9 |
Shield / fee split | 0xa20636bf3792f705ae51a48afdec336fb0518cd43365a8fc3e596dea23266dc9 |
Source and Method Notes
Primary mechanism and scope clarification: SlowMist primary analysis and clarification. Incident index: SlowMist Hacked. Transaction references above are Etherscan records. SentinelTX was used for the original call-trace and downstream receipt analysis. This revision directly checked the exploit receipt’s decoded events and the helper creation transaction in Etherscan; the shield accounting and exploit anchor were cross-checked against visible explorer records. The report separates directly observed transfers, attributed source-code findings and analytical inference.
The central result is a module-authority route yielding a precisely observed ETH receipt, followed by a fee-reconciled privacy-pool entry. A large flash loan is not the loss figure, a protocol fee is not cash-out, and a privacy endpoint is not an identified attacker.
Revision note — 5 October 2026: added exact victim-level receipt accounting, helper creation evidence, a measured UTC timeline, a proportional shield-allocation chart and clearer directional diagrams. The original investigation window ends at block 26122303 (4 October 2026 23:32:47 UTC); this revision does not claim a complete scan of later activity.
 0
 0
55 조회
 조사관 신청하기