Notional V1 Escrow Drain: $1.73M Left a Deprecated Contract in Minutes

September 17, 2026
An unsafe `uint128` cast on Ethereum. Funds in Tornado Cash before most of the market was awake. Recovery is still open.
On 3–4 September 2026, residual balances sitting in Notional Finance’s long-deprecated V1 escrow were drained in a single transaction. The loss was 1,658,525 USDC and 69,257 DAI, about $1.73 million at the time. Current V2 / V3 / Exponent products were not in scope. The team published a post-mortem on 8 September. No funds have been recovered.
That last sentence is why this case is on ChainBounty.
V1 was publicly deprecated in January 2022. Withdrawals were left live so remaining users could exit. Four years later the escrow at `0x9abd0b8868546105F6F48298eaDC1D9c82f7f683` still held real USDC and DAI. That is the inventory an attacker actually needs: a forgotten contract, a live withdraw path, and a balance large enough to bother with.
What broke
This was not a flash loan, not an oracle, and not a stolen key.
Two `mintfCashPair()` calls created payer liabilities of `1` and `2^256 − 1`. Combined, the payer’s liability evaluated to −2^128. Free-collateral valuation in `ExchangeRate._convertToETH()` then applied a raw `uint128()` cast instead of `SafeCast.toUint128()`. On Solidity 0.6.x that overflowed to 0. The collateral check passed.
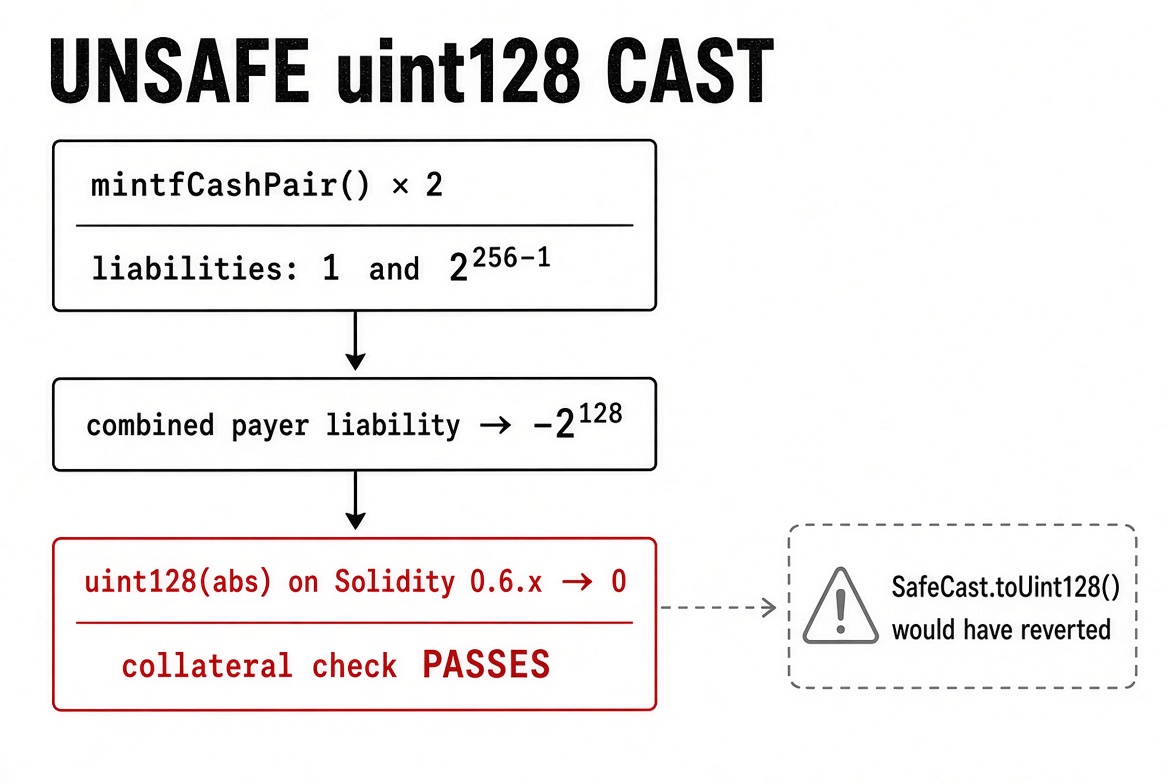
The attacker minted an unbacked fCash claim equal to the live escrow balances, settled it, and withdrew.
The whole sequence fit in two transactions, three minutes apart:
Hash | Time (UTC) | Block | |
|---|---|---|---|
Setup |
| 3 Sep 2026, 23:58:47 | 25,900,220 |
Drain |
| 4 Sep 2026, 00:01:35 | 25,900,234 |
Pause |
| shortly after | — |
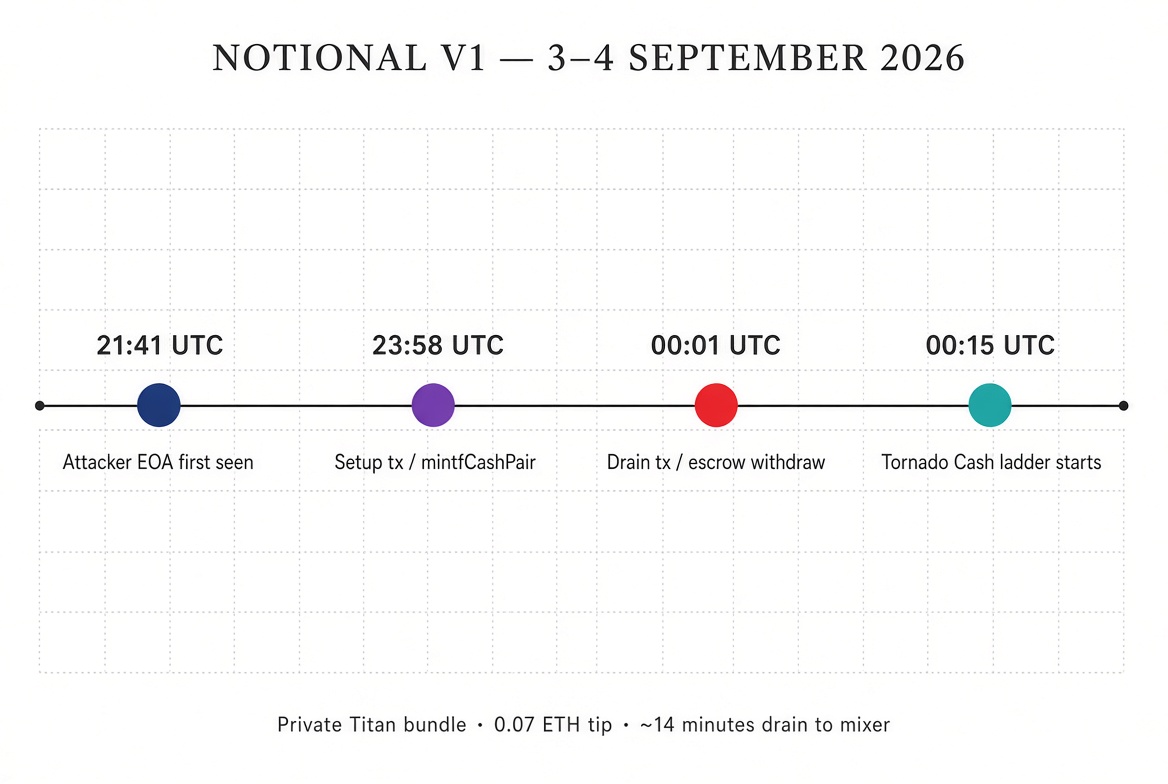
The drain was submitted as a private bundle through Titan, with a 0.07 ETH builder tip. Public mempool never got a look.
Where the money went
Attacker main: `0xDaCC235a494750193695A111D715c2ca12b5Ce38`. First on-chain activity for that wallet is 3 September 2026, 21:41:35 UTC — about two hours twenty minutes before setup. No prior history. No existing labels.
First-hop DAI receiver: `0x265ccfF3673bCAb03867988081cd51bFd919C03C`.
Same day, the stables were swapped to roughly 689.2 ETH. From `00:15:59 UTC` on 4 September, that ETH was dropped into Tornado Cash in a 100 / 10 / 1 / 0.1 ladder — 25 deposits, total 689.2 ETH, all from `0xc95496c917a41a394efdac3e0882f5903d24de69` into the sanctioned Tornado router `0xd90e2f925da726b50c4ed8d0fb90ad053324f31b`.
Fourteen minutes from drain to mixer.
One tracing detail worth flagging before anyone copies an abbreviated address into a freeze letter: two wallets share the same four-character prefix and suffix.
- `0xc95496c917a41a394efdac3e0882f5903d24de69` — Tornado deposit source (25 txs)
- `0xc9541b387b55c88aa6962480432b185373b5de69` — received 689.21258215375 ETH; outbound from this wallet was not established in the first outbound pass
Write both in full. Do not collapse them to `0xC954…De69`.
The only non-mixer service endpoint that showed up in the traced residual dust is CCE.Cash treasury (`0x0361897d757d13a4afad64a2e1bc561b96a8c7cf`) for 0.011222 ETH. No CEX deposit address appeared in the outbound graph. That is a null result, not a gap to invent around: inside the current hop window there is nothing to freeze at an exchange.
The graph below is the outbound trace from the origin wallet through five hops. Seed is the attacker EOA. Terminal is Tornado plus the CCE.Cash dust.
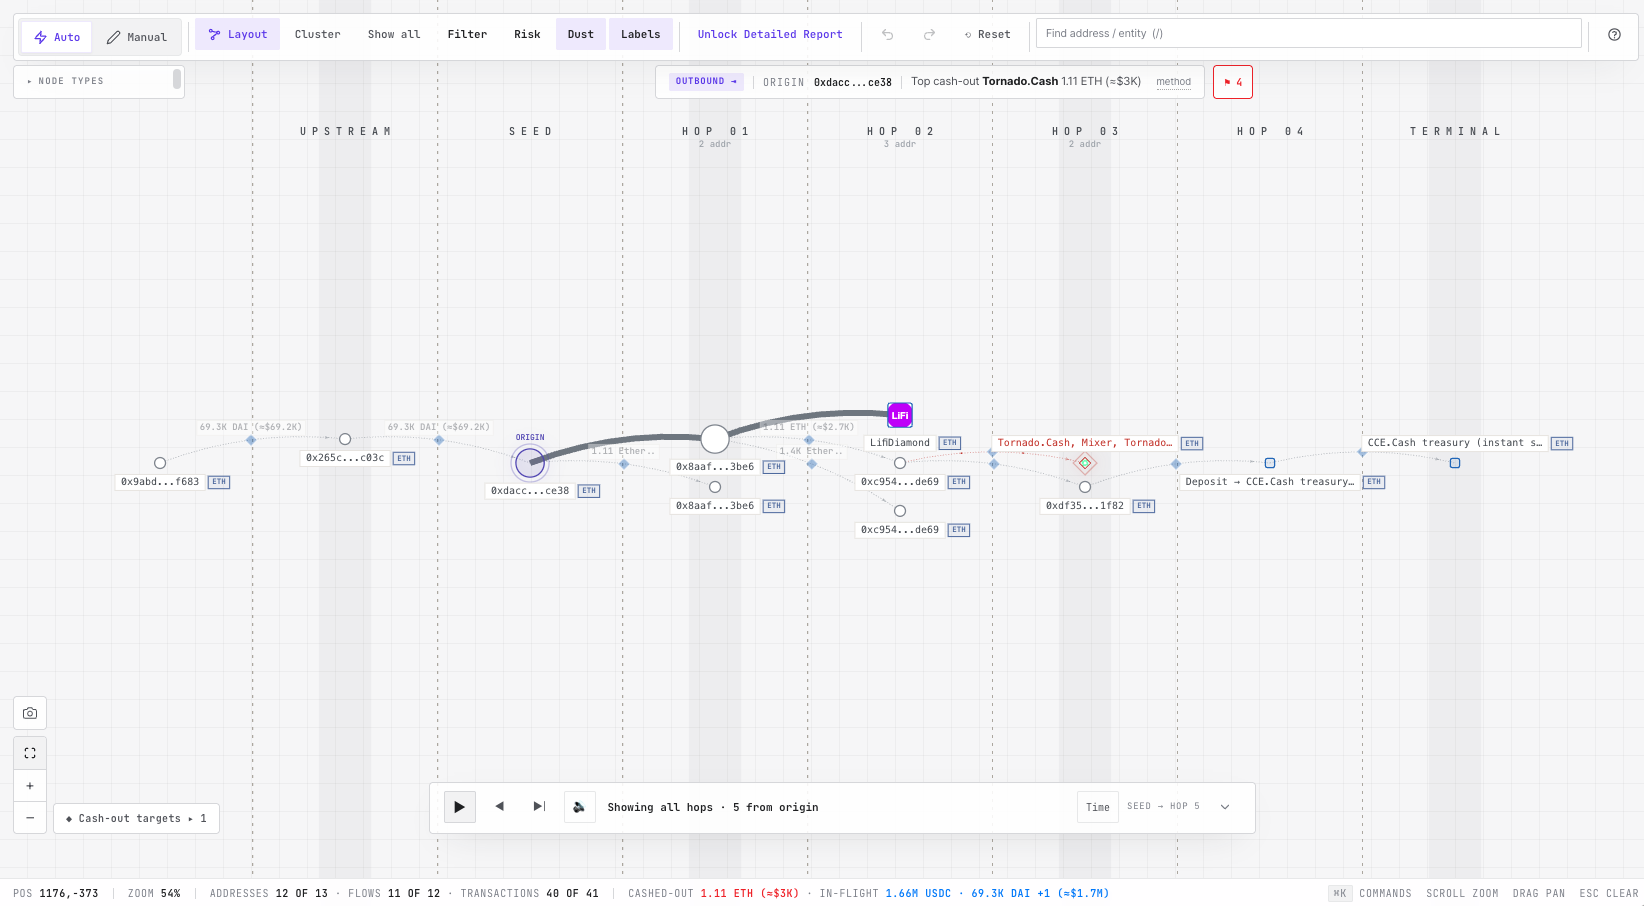
Status on that pass: 12 of 13 addresses, 11 of 12 flows, cashed-out 1.11 ETH (~$3K) visible on the highlighted path, in-flight 1.66M USDC + 69.3K DAI (~$1.7M) sitting behind the mixer wall.
Why this is still an open case
Notional’s post-mortem is public. The recovery surface is not closed.
Three facts keep it live:
1. Mixer withdrawals after 4 September have not been fully mapped. 689.2 ETH went in on a structured ladder. The only practical freeze window is the moment a withdrawal hits a KYC venue.
2. The attacker cluster is purpose-built. Main EOA, exploit contract (`0xec434a2f9b7b93aad1bed77d6bc512a75ae90d78`, 0.07 ETH tip receiver, first seen 3 Sep / last active 4 Sep), relay `0x8aaf01b6f9acc973274b8718be4d1c1be10e3be6`, and both `0xc954…de69` wallets are unlabeled and appear for this job only. That is operational hygiene, not amateur hour.
3. The primitive is being copied. SlowMist flagged two actors on BSC staging the same fCash overflow and waiting on position maturity. Cited contract: `0x0795E2cd771788572b61BeA45Abd6E9a8FC8D9F0`. Whether those positions matured, were paused, or paid out has not been confirmed on-chain in this file. That check is time-sensitive. After maturity it becomes another recovery problem. Before maturity it is still a stop.
What we want from investigators
P0
- Rebuild the exact call trace on setup + drain. Publish the overflow math as a one-pager.
- Map every ETH hop into Tornado and watch withdrawals after 4 September against the 100 / 10 / 1 / 0.1 pattern.
P1
- Cluster `0xDaCC…Ce38`, both `0xc954…de69` wallets, and the Titan private-order flow against prior exploits. Outbound-only work so far did not produce a prior-job link. That is also a result — inbound gas funding on the attacker EOA is the better identity lead.
- Full BSC replica file: transactions, maturity timestamps, pause status, whether any payout cleared.
P2
- Inventory other live 0.6.x forks of Notional V1 / similar fCash escrow that still hold balances.
- Deliverable: freeze memo on standby (no CEX dust in the current window), Tornado withdrawal watchlist, and a “deprecated-but-funded” contract list.
The part that should bother protocol teams
Deprecated does not mean empty. A contract that nobody monitors, compiled on 0.6.x, with a raw integer cast that the same file already replaced with `SafeCast` in other places, is not a historical footnote. It is an unattended vault.
The operator who hit this one already knew that. They picked the leftover escrow, submitted privately, converted freezable stables to ETH the same day, and structured the mixer deposits to the denomination set. If they built an inventory of V1-style fCash escrows, Notional was unlikely to be the only name on it.
If you are tracing withdrawals, sitting on a BSC confirmation, or holding a labeled counterpart we missed — file it.
Key references
- Notional post-mortem: https://blog.notional.finance/notional-v1-exploit-post-mortem/
- Drain tx: https://etherscan.io/tx/0xc3f3e318f7ab2d0daaba59e6ec901d25d1fe8a89aafe2b2b62e3b9aee1a24efa
- Escrow: `0x9abd0b8868546105F6F48298eaDC1D9c82f7f683`
- Attacker: `0xDaCC235a494750193695A111D715c2ca12b5Ce38`
 0
 0
44 reads
 Become an Investigator