NEM token exploit: tracing the BSC-to-Ethereum trail

October 24, 2026
Source: SentinelTX analysis.
SentinelTX’s analysis records 726,307.1011248019 BSC-USD paid to the exploit-signing address, followed by a bridge route and Ethereum settlement activity. The reported loss, mechanism, and final ETH balance require different levels of qualification.
This ChainBounty review draws on SentinelTX’s analysis of case CASE-20261024-NEM1. Recorded transfers, reported figures, and analytical assessments are distinguished throughout.
The recorded proceeds and reported loss
The investigation concerns a BNB Smart Chain token called NEM, identified in the analysis as token contract 0x9cf0e3ad4efa7ab602d7b5a38c55795cfa777777. The name NemTokenV2 comes from press reporting cited by SentinelTX. The analysis establishes no connection to the separate NEM/Symbol blockchain project.
Its central finding is a transaction dated October 21, 2026, at 03:28:50 UTC, in BSC block 128,866,147. The signing address, 0xfd929b0f270dfea6c4827262b4e2bf6ea50fe9b6, called an attack contract, 0x5e6d1f40be466dd2facc94a26818948ecd3b1ca2. SentinelTX classifies the resulting payment of 726,307.1011248019 BSC-USD to the signing address as confirmed. The full transaction hash and address register appear in the appendix.
The widely reported loss of approximately US$821,920 is a separate source claim. It is not interchangeable with the recorded payment of 726,307.1011248019 BSC-USD. SentinelTX does not establish a complete reconciliation between the reported loss and the recorded proceeds, so neither figure should be substituted for the other.
The analysis distinguishes the October 21 execution date from the October 22 alert and publication date. Its October 24 ETH balance observation is later still. These dates describe different events, not competing dates for one transaction.
From preparation to the Ethereum exit
All transaction times below are UTC on October 21, 2026, as stated in the source analysis.
- 01:00:17: The address described as the funder sent the signing address its first recorded gas funding, 0.007 BNB. The analysis flags this amount as unverified and requiring corroboration.
- 01:28:16–03:27:26: Sixteen NEM transfers from the funder supplied approximately 767,818.31 NEM, also an unverified amount. A second gas top-up is recorded as 0.01 BNB. Six helper-creation records span 01:32:22–03:14:31.
- 03:28:30: The signing address transferred 767,811.3061168424 NEM to the attack contract. The transfer is recorded, but its quantity is explicitly unverified.
- 03:28:50: The exploit transaction executed. The analysis reports 1,608 receipt logs and approximately 473 million BSC-USD in transaction-level movement across several counterparties. That gross movement is not presented as the loss or the attacker's proceeds.
- 03:38:38: The recorded 726,307.1011248019 BSC-USD payment was forwarded through a router labeled Socket OpenRouter. SentinelTX correlates a Relay bridge record to this source transaction.
- 03:39:11: A sender labeled Relay.link delivered 725,384.763364 USDT to the same address on Ethereum. The analysis classifies the route as confirmed through the correlated bridge record and destination transfer, while marking the destination amount unverified.
- 03:46:11–03:47:47: Three USDT legs went to a contract labeled CoW Protocol settlement. Their quantities are unverified.
The analysis’s later balance read is dated October 24. It records approximately 296.19 ETH remaining at the signing address on Ethereum, with no outbound ETH in the retrieved ledger. This is an unverified historical balance observation, not a claim about the address's live balance when this article is read.
The assessed mechanism: a skim-and-burn loop
SentinelTX assesses the incident as a token-accounting and liquidity-pool reserve manipulation exploit. Its proposed sequence depends on reporting that transfers into the pair count as sell volume, while a function named flushLpSellRecycle() burns NEM held by the pair. Repeated skim() calls are reported to return the operator's tokens as the pool's NEM holdings shrink, before the retained inventory is sold against the altered pool state.
That sequence is an assessment in the analysis. The token's source code and the individual burn, reserve, and skim-related events were not decoded there. The proposed sequence is therefore not an event-by-event proof of the vulnerability.
The reported count of 42 cycles has a limited technical anchor: the transaction's calldata ends with 0x2a, or decimal 42. Without ABI decoding, that word does not by itself prove what the parameter controls or how many cycles executed. Likewise, 1,608 logs show extensive transaction activity in the analysis, but an unclassified log count cannot independently establish 42 repetitions of a particular mechanism.
Flash-borrowed liquidity is another inference. SentinelTX describes large, same-transaction BSC-USD round trips involving Venus vUSDT, PancakeSwap, and two unlabeled contracts. It did not decode loan origination and repayment events. The analysis assigns the direct loss to the affected pair's liquidity providers, but does not provide a reconciled reserve-loss calculation matching the reported US$821,920.
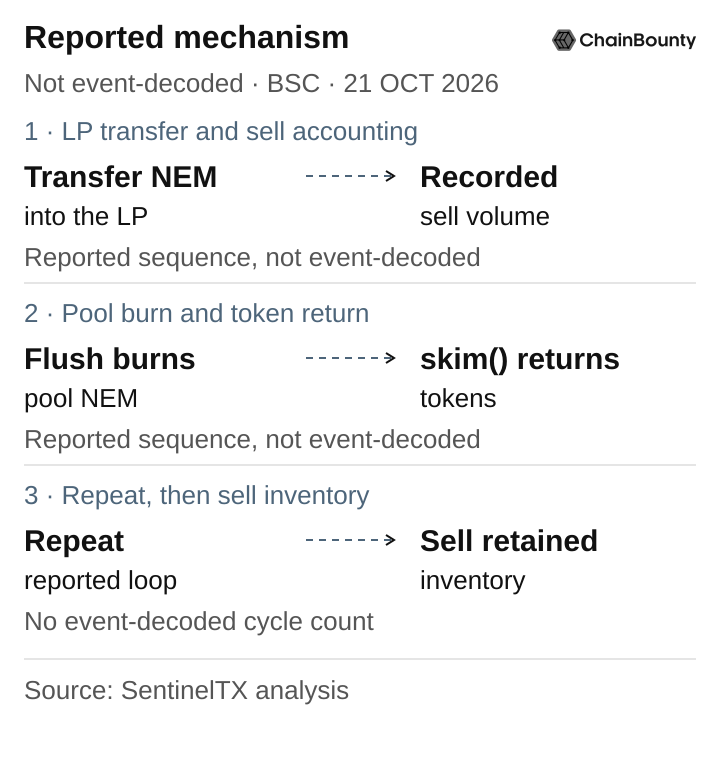
Diagram 1. Read the numbered rows from top to bottom, and each row from left to right. The analysis assesses a skim-and-burn reserve-desynchronization loop: transfers into the LP register pending sell volume, flushLpSellRecycle() burns NEM held by the pair, skim() returns the operator’s tokens, and repeated rounds precede a final inventory sale. This is a reported mechanism, not an event-by-event decoded proof. The reported 42-cycle count is only partially corroborated by the raw calldata word 0x2a, not ABI-decoded; no exact loop count is encoded in this schematic. Equal-width dashed arrows summarize the reported sequence, not token quantities.
Slate labels identify the stated actions; arrows indicate the relationships written in each row, not quantities.
NEM token: 0x9cf0e3ad4efa7ab602d7b5a38c55795cfa777777. LP/pair: 0x840e19dcca541ee0b55a3c67e900a39d523b12b8; its victim-pool role is a source claim consistent with the analysis’s records. Attack contract: 0x5e6d1f40be466dd2facc94a26818948ecd3b1ca2. Signer/proceeds recipient: 0xfd929b0f270dfea6c4827262b4e2bf6ea50fe9b6; operator identity is not established.
Source: SentinelTX analysis. Source location: Transaction Typology → Mechanism: observed, inferred and claimed; Scheme description (assessment).
Funding supports a relationship, not an identity
The funder, 0x96cb6bec56e43b2f16c05e1af4776fbc7b9713b5, supplied the initial gas and the NEM inventory later committed to the attack contract. Its first-seen date is October 20 in the analysis. The repeated funding, inventory transfers, and timing support SentinelTX's assessment that the two addresses were operated by the same actor or closely coordinated actors. Common ownership is not proven, and no person or organization is identified as the operator.
Six helper contracts reportedly returned their NEM balances short by exactly 1 NEM each. SentinelTX interprets the similar interactions as rehearsal against mainnet conditions, an operational assessment rather than a separate finding of intent. Six listed WBNB recipients are classified as probable helpers; their mapping to the six creation records is not established.
The inventory has another upstream lead. An unlabeled contract, 0xaee6b842f94281653dde98da97debd93007de2a1, reportedly sent the funder 780,757.29 NEM across 45 transfers. In itemized examples, NEM arrived with BSC-USD and the same BSC-USD quantity was returned shortly afterward. SentinelTX suggests a reward, staking, or distribution mechanism as a possible explanation, but the contract's function was not decoded.
The contract’s ownership and any additional loss remain unproven. Shared first-seen dates with the token and pair do not establish ownership. The analysis also records a post-exploit sale by the funder through a TransitSwapRouterV5-labeled route, but its relationship to any additional loss remains unresolved.
Following the exit without overstating the endpoint
The analysis traces a BSC stablecoin payment into the router, a correlated Relay delivery on Ethereum, and three transfers to CoW Protocol settlement: 250,000.0 USDT, 250,000.0 USDT, and 225,384.763364 USDT. Each Ethereum quantity carries the source's unverified-amount qualification.
SentinelTX attributes the difference between the routed and delivered quantities to bridge fees and spread. That remains an assessment: the amounts are in different token denominations, the destination quantity is unverified, and no itemized fee accounting is provided.
The Ethereum native ledger is reported as four inbound transfers totaling 296.192678708450769578 ETH, no outbound ETH, and 0.000205413793461084 ETH used for gas. Its resulting balance is 296.192473294657308494 ETH. All of these ETH figures are unverified. The counterparties and hashes of the four incoming ETH transfers are not itemized in the analysis, so the article cannot supply a complete leg-by-leg conversion reconstruction.
The recorded endpoint is an address holding native ETH. It is not evidence of fiat cash-out. The WBNB contract's Binance-related label does not make it a Binance customer deposit address, and the CoW settlement contract is described as a non-custodial venue. No custodial exchange deposit is established by the analysis.
The BSC exit also contains an EIP-7702 authorization that delegates execution to another address. SentinelTX records that field but treats its batching interpretation as an assessment. Delegation on Ethereum is not established. These technical roles do not identify a beneficial owner.
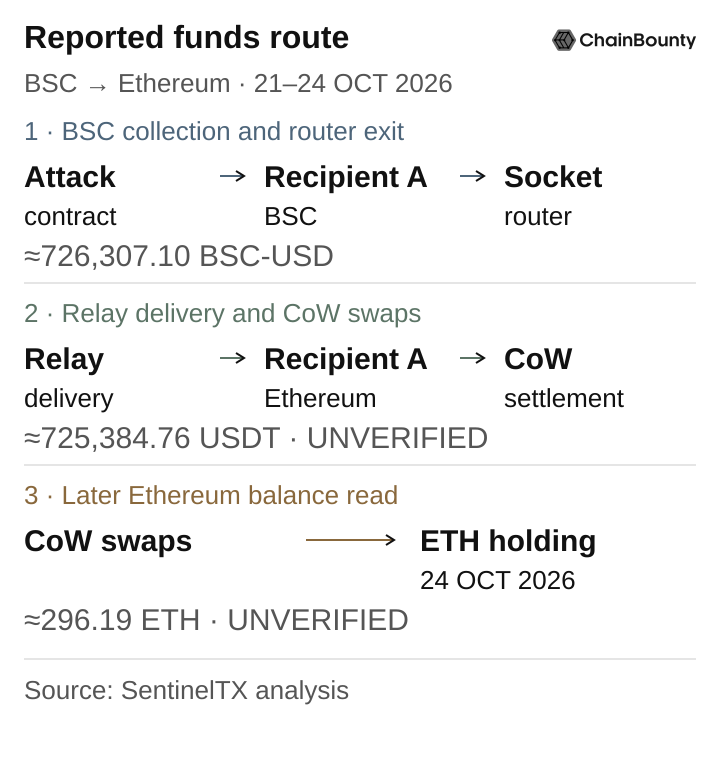
Diagram 2. Read the numbered rows as the reported route, not three independent totals. The analysis records 726,307.1011248019 BSC-USD from the attack contract to Recipient A and the same quantity forwarded through the Socket router on October 21. A correlated Relay record reports delivery of 725,384.763364 USDT to the same address on Ethereum; that destination quantity is unverified. Three CoW settlement legs follow. The October 24 balance read reports 296.192473 ETH, while the analysis’s ledger calculation gives 296.192473294657308494 ETH; both are unverified. Display values are approximate. The four inbound ETH counterparties are not itemized, so the final arrow summarizes the analysis’s conversion sequence and later balance, not a fully reconstructed transfer leg. Equal-width arrows are schematic; the BSC-USD, USDT and ETH values are not summed or treated as interchangeable loss amounts.
Slate: 1 · BSC collection and router exit; Sage: 2 · Relay delivery and CoW swaps; Amber: 3 · Later Ethereum balance read. Equal-width arrows show stated routes, not quantities.
Recipient A on both chains: 0xfd929b0f270dfea6c4827262b4e2bf6ea50fe9b6. BSC attack contract: 0x5e6d1f40be466dd2facc94a26818948ecd3b1ca2. Socket router: 0x50cfe7c1938db66a1a6d2e86d36f39fbef3d5c4a; the analysis’s literal attribution includes “Socket OpenRouter (Ethereum)” despite the BSC transaction. Relay-labeled Ethereum sender: 0xb92fe925dc43a0ecde6c8b1a2709c170ec4fff4f. CoW settlement recipient: 0x9008d19f58aabd9ed0d60971565aa8510560ab41. No operator identity or custodial exchange deposit is established.
Source: SentinelTX analysis. Source location: Executive Summary → Exit; Transaction Chronology → Fund-flow sequence and Gross versus forwarded amounts; Exchange-deposit and venue legs.
Why the look-alike transfers were excluded
The original source distinguishes real funding from records it classifies as suspected address poisoning. At 01:07:18, a look-alike of the funder sent 0.007 units of a token whose symbol imitated BNB using non-Latin characters. Its amount mirrored the real gas funding, but the analysis found no value-bearing onward movement and excluded it.
A mirror-image record named a look-alike of the signing address. The two full addresses are distinct, and the mirror-image record’s transaction hash is not provided. Neither poisoning record is used as evidence of common control or an economic connection.
The analysis also excludes unsolicited airdrops as spam, including two tokens recorded with a burn-address emitter and other tokens with miscellaneous names. An appearance in a transaction history is not enough, within the source's own methodology, to include a transfer in the traced proceeds.
Recovery implications and analytical limits
SentinelTX's practical priority is the last recorded Ethereum holding and any later onward transfer. The analysis describes potential investigative leads in the funder's upstream financing and in request metadata that infrastructure operators might hold. The availability of that metadata and any resulting recovery action are not established.
The source rates near-term recovery prospects as moderate, but that is its expert assessment, conditional on an unverified balance observation. It is not a recovery probability, an assurance that funds remain available, or a promise that a service provider can freeze native ETH. The analysis’s legal-process and negotiated-return suggestions require case-specific decisions by the affected parties and their qualified advisers; they are not legal instructions from ChainBounty.
Important analytical limits remain: the mechanism has not been decoded cycle by cycle, flash liquidity is inferred, the funder's earlier history is not itemized, two in-transaction counterparties lack an onward trace, and the four ETH receipts lack individual detail. The reported loss remains unreconciled with the recorded proceeds. The analysis does not specify its complete query windows; its conclusions are limited to the records discussed. No personal identity, custodial deposit, or connection to NEM/Symbol is established.
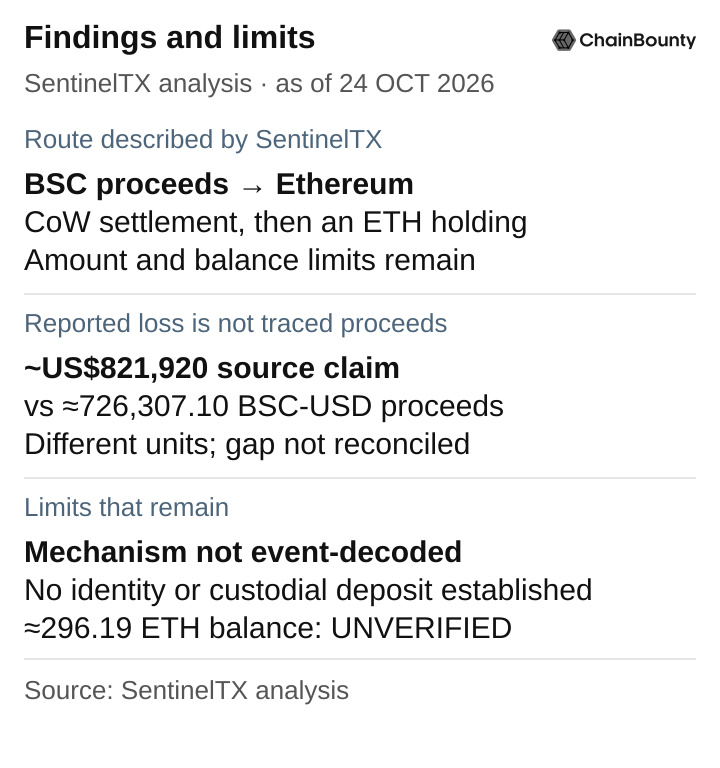
Figure 3. The analysis supports a reported route from BSC proceeds through Relay to Ethereum and CoW settlement, subject to its quantity and balance qualifications. Approximately US$821,920 is a publicly reported loss claim; 726,307.1011248019 BSC-USD is the analysis’s recorded proceeds payment. These differently denominated figures are not directly interchangeable, and the source does not reconcile the loss gap. The mechanism is not decoded cycle by cycle; no personal or organizational identity, custodial exchange deposit, fiat cash-out, or connection to the unrelated NEM/Symbol project is established. The October 24 balance observation of 296.192473 ETH remains unverified and is not a statement of a live current balance. Rounded display values are approximate.
Slate identifies section headings, not certainty or risk.
The balance observation and Recipient A role refer to 0xfd929b0f270dfea6c4827262b4e2bf6ea50fe9b6 on Ethereum, not the separate poisoning look-alike identified in the analysis.
Source: SentinelTX analysis. Source location: Key findings and certainty; Transaction Chronology → Coverage against the claim and Cash-out endpoint; Transaction Typology; source limitations.
Sources and scope
The transaction findings, address roles, and analytical assessments in this review are attributed to SentinelTX’s analysis of case CASE-20261024-NEM1. The appendix preserves its full address and transaction references. It should be read as a source register, not as independent verification of the underlying blockchain records.
The press context in SentinelTX’s analysis comes from search-result snippets attributed to TokenPost, DEV Community, KuCoin, PANews, TechFlow, and CryptoBriefing. These are attributed reporting references, not claims that the complete pages or underlying SlowMist posts were reviewed for this article.
Amounts described as unverified require corroboration. Service labels identify the roles assigned to addresses in the analysis; they do not establish ownership or custody. The mechanism and recovery assessments retain their stated qualifications, and the October 24 balance observation must not be treated as a live balance.
Appendix: full identifiers
The following register lists 31 full addresses and 21 full transaction hashes cited in SentinelTX’s analysis. It is not a complete transaction ledger. Address roles and service labels do not establish operator identity.
Full addresses
- 1. 0xfd929b0f270dfea6c4827262b4e2bf6ea50fe9b6 Exploit transaction signer and proceeds recipient on BSC; same address receives the reported Ethereum delivery. The analysis records BSC delegated code. Operator identity is not established.
- 2. 0x5e6d1f40be466dd2facc94a26818948ecd3b1ca2 Attack contract on BSC and payer of the recorded 726,307.1011248019 BSC-USD proceeds.
- 3. 0x9cf0e3ad4efa7ab602d7b5a38c55795cfa777777 NEM token contract on BSC. NemTokenV2 is a press-source name, not independently verified here.
- 4. 0x840e19dcca541ee0b55a3c67e900a39d523b12b8 Contract identified by press as the USDT/NEM pair on PancakeSwap. The analysis considers its victim-pool role consistent with the recorded transfers.
- 5. 0x96cb6bec56e43b2f16c05e1af4776fbc7b9713b5 Funder on BSC: recorded source of the signing address’s first gas and NEM inventory. No operator identity established.
- 6. 0xaee6b842f94281653dde98da97debd93007de2a1 Unlabeled BSC contract recorded as the funder’s NEM source. Its function is not decoded; a project-side mechanism is only an assessment.
- 7. 0x63c0c19a282a1b52b07dd5a65b58948a07dae32b EIP-7702 delegate named in the authorization list of the BSC exit transaction. No label; type not classified in the analysis.
- 8. 0x50cfe7c1938db66a1a6d2e86d36f39fbef3d5c4a BSC bridge-exit router identified as Socket OpenRouter in SentinelTX’s analysis. This entry concerns the recorded BSC transaction.
- 9. 0xb92fe925dc43a0ecde6c8b1a2709c170ec4fff4f Sender of the reported Ethereum USDT delivery. Exact source label: “Relay.link.”
- 10. 0x9008d19f58aabd9ed0d60971565aa8510560ab41 Recipient of the three Ethereum USDT legs. Exact label: “CowProtocol, Exchange.” Described by the analysis as a non-custodial settlement contract.
- 11. 0x07964f135f276412b3182a3b2407b8dd45000000 Route used for the funder’s post-exploit NEM sale on BSC. Exact label: “TransitSwapRouterV5.”
- 12. 0xfd5840cd36d94d7229439859c0112a4185bc0255 BSC in-transaction BSC-USD counterparty. Exact label: “Venus USDT, vUSDT, DEX.”
- 13. 0x238a358808379702088667322f80ac48bad5e6c4 BSC in-transaction BSC-USD counterparty. Exact label: “PancakeSwap.”
- 14. 0x92b7807bf19b7dddf89b706143896d05228f3121 Unlabeled in-transaction BSC-USD counterparty on BSC; onward movement not established.
- 15. 0x4f31fa980a675570939b737ebdde0471a4be40eb Unlabeled in-transaction BSC-USD counterparty on BSC; onward movement not established.
- 16. 0x370a7e2d300c14d79d4a7ee07aaca46c4b3012cf Listed with the following address under submitter and target of the Ethereum delivery transaction. The roles and attribution are unverified.
- 17. 0xccc88a9d1b4ed6b0eaba998850414b24f1c315be Listed with the preceding address under submitter and target of the Ethereum delivery transaction. The analysis does not separately verify the mapping or attribution.
- 18. 0xbb4cdb9cbd36b01bd1cbaebf2de08d9173bc095c WBNB contract on BSC. Exact label: “Binance, WBNB Token, Token Contract.” Not a Binance customer deposit address in the analysis’s account.
- 19. 0x2db7fca7a84a4ae69d41aec8d74b96b679c8ac5e First of six listed WBNB recipients on BSC, classified as probable helpers. Their mapping to helper-creation records #1–#6 is unresolved. The reported 0.0001 WBNB quantity is unverified.
- 20. 0xbae2628c3f926971d4fc66c16120b2c7e0dce42a Second listed WBNB recipient on BSC; probable helper, with creation-record mapping unresolved.
- 21. 0x0c3dac1d3b6f870b5bca16b7926631b525216865 Third listed WBNB recipient on BSC; probable helper, with creation-record mapping unresolved.
- 22. 0xe1a9d2ecfb453be4608c126ef95ee71faec7f9cc Fourth listed WBNB recipient on BSC; probable helper, with creation-record mapping unresolved.
- 23. 0x07d792806989300cd3b5d05329fea154a32ad96b Fifth listed WBNB recipient on BSC; probable helper, with creation-record mapping unresolved.
- 24. 0xa16f9a316a2b9ef97994cd47991b72ecbebfd7db Sixth listed WBNB recipient on BSC; probable helper, with creation-record mapping unresolved.
- 25. 0x50c4e75a512f2a14a7b304787adf79c4531a5909 Unlabeled code-bearing recipient of the residual BNB route at 03:40:52 UTC on BSC. The source does not provide that transaction’s hash.
- 26. 0x97caca78ac2a94c67643d07843f85afaa44a3ea5 Unlabeled BSC-USD source to the funder and address appearing in residual-route calldata. The source explicitly treats a swap-route executor role as an unverified lead, not established funding attribution.
- 27. 0x96cb0a81cd849f21e512f5d6eda78bdf1c0713b5 Look-alike of the funder, excluded as suspected address poisoning. Distinct from the real gas-funding address.
- 28. 0xfd92b74d57b02814ea2591bd963d1fae390fe9b6 Look-alike of the exploit signer/proceeds recipient, excluded as suspected poisoning. It is distinct from the address receiving the recorded proceeds.
- 29. 0x058941553ea64444077522d6b5edc2e09655ef66 Token contract used by the suspected poisoning record; symbol imitates BNB using non-Latin characters. Not native BNB.
- 30. 0x5c718fc9c1bc1ca6d55b3c9c564153d98faff2d0 Unsolicited token identified among excluded spam records with a burn-address emitter.
- 31. 0x1303753839659cd4ca526a9c2e7091cc68be26ab Second unsolicited token identified among excluded spam records with a burn-address emitter.
Full transaction hashes
Times below refer to October 21, 2026, UTC. Transaction references and classifications are attributed to SentinelTX.
- 1. 0x57b1847f6f2cf3d1676f6ba38064c0756d1fbec9b502c5dc662e35a2307fb0dd BSC. First gas funding, October 21 at 01:00:17 UTC; 0.007 BNB, unverified amount.
- 2. 0xe9827bcce1262daf9a6026afdce9a4d51bf7e28dcd7d3ba767c9684fc8523468 BSC. Second gas top-up, stated as 0.01 BNB. The analysis places it in the preparation interval but does not give an exact time.
- 3. 0xcbcdc77b393a30bf3212f80a8afdc334af642dc9615d47582cc5302f739da924 BSC. Anchor cited for NEM inventory funding. The analysis does not itemize all sixteen NEM transfer hashes.
- 4. 0x54842ae0334a6b4bd2b24fbbe0251ea2c302f2ab253f87f2340b7462a7d8a4cb BSC. NEM transfer into the attack contract at 03:28:30 UTC; 767,811.3061168424 NEM, unverified amount.
- 5. 0xfb093c96c0094cbcca10801f97ed2e5ed3d96550ce64b544df5a349545723f91 BSC. Exploit transaction, block 128,866,147, 03:28:50 UTC. SentinelTX classifies the payment of 726,307.1011248019 BSC-USD to the signer as confirmed.
- 6. 0x4da49613a58f3d872c5991c0b7fc1a3d4ebb6b2b3c55fab768c490e57b104a68 BSC. Router exit, block 128,867,454, 03:38:38 UTC; source hash used to correlate the Relay bridge record. SentinelTX records EIP-7702 type-4 execution.
- 7. 0xc4acd18a0e8f4b4f24b47ce6e57a7c936b148108327236125daac250d07bc8bb Ethereum. Reported bridge delivery, block 26,238,334, 03:39:11 UTC; 725,384.763364 USDT, unverified amount.
- 8. 0xfc7fc1af22358f55ea4f3847efb7a70514e81b4d0d8c5da392c7874609ab2533 Ethereum. First CoW settlement leg, 03:46:11 UTC; 250,000.0 USDT, unverified amount.
- 9. 0x0757d2285bd862798c3b52181e919e8853d6037e8096e4fdf7456a7e3269ab0d Ethereum. Second CoW settlement leg, 03:47:11 UTC; 250,000.0 USDT, unverified amount.
- 10. 0xbcef08a442ca7bba882c43ebf61fbc6fc285a70d7d207238bbea797b17817cfb Ethereum. Third CoW settlement leg, 03:47:47 UTC; 225,384.763364 USDT, unverified amount.
- 11. 0xf66fa8c86299c9de6798556d42966fb9fa8c6b47b0d1eb8080344685af3668fa BSC. Funder’s post-exploit NEM sale, 03:37:01 UTC, through the TransitSwapRouterV5-labeled route.
- 12. 0x38739784a8b13de37666e5770de7d2603a92ee50f233789b97ddd7c468300ed2 BSC. Example inbound cycle to the funder, 03:26:19 UTC, including 12,571.42 BSC-USD and NEM, as stated in the analysis.
- 13. 0x57a6519c13ad203c479d3166fea6ddefc46ad994d14e665c939778ab12f97d57 BSC. Example corresponding BSC-USD return, 03:26:45 UTC.
- 14. 0xce77892c0e98a893f0b109d0f905c9423337addec5142edaf75be07eb3a73f53 BSC. WBNB transfer to probable helper 0x2db7fca7a84a4ae69d41aec8d74b96b679c8ac5e.
- 15. 0x645edaec509f12f493ca15a42e793fc731dfc0610da85b7a1ee59dd7c609f0d7 BSC. WBNB transfer to probable helper 0xbae2628c3f926971d4fc66c16120b2c7e0dce42a.
- 16. 0x0e714d980478f9f636eae18d81ec5399e66eeee6926c113e886b243818e553df BSC. WBNB transfer to probable helper 0x0c3dac1d3b6f870b5bca16b7926631b525216865.
- 17. 0xec0de15f90e82015087eae522d2771de1ee8ac192cd91b8a851fa802079d34c6 BSC. WBNB transfer to probable helper 0xe1a9d2ecfb453be4608c126ef95ee71faec7f9cc.
- 18. 0xa3b2e00ade40364427fbcc08803fe9fa3c7de8aac45dcd92986e140890150ea9 BSC. WBNB transfer to probable helper 0x07d792806989300cd3b5d05329fea154a32ad96b.
- 19. 0xfb5384ed31469f13842a77a05ca0511402b7bad0d8af5f858de5acb9155e7124 BSC. WBNB transfer to probable helper 0xa16f9a316a2b9ef97994cd47991b72ecbebfd7db.
- 20. 0xcf4469e6214a085023251542c924fc468be8856a144075ddaf47360fcc8792e3 BSC. WBNB transfer to attack contract 0x5e6d1f40be466dd2facc94a26818948ecd3b1ca2.
- 21. 0x2b407b29b19baf491bfbcdd2a2e9c67f939e17bae22ffff6bd8f6287646326f8 BSC. Suspected address-poisoning record at 01:07:18 UTC. Excluded from economic tracing and attribution.
Other explicit identifiers
- Case reference: CASE-20261024-NEM1.
- Chains: BNB Smart Chain, chain ID 56; Ethereum, chain ID 1.
- Exploit calldata selector: 0x05d546ef. Final raw word: 0x2a, decimal 42. No ABI-decoded meaning is established.
- BSC exit observed byte pattern: 0x095ea7b3, described in the source as an approve pattern; inner router call not ABI-decoded.
- Control-call selector: 0xe9ae5c53. Ethereum delegated-code status is not established.
- BSC authorization nonce: 0x32. BSC transaction nonce: 0x31.
- Reported route text: "Source":"BUNGEE_AUTO", "AmountInUSD":"6.781519". This describes the residual BNB route, not an added valuation of the main proceeds.
- Helper-creation record identifiers: #1–#6; source block range 128,850,621–128,864,238. Full creation hashes are absent from the original narrative.
- Ethereum first control-transaction block: 26,238,366; nonce 0. Its hash is not supplied.
- Residual BNB transaction block: 128,867,751, at 03:40:52 UTC. Its hash is not supplied.
Coverage of the identifier register
- The full set of sixteen inventory-funding transaction hashes is not enumerated.
- The full set of 45 inbound NEM transfer hashes for the upstream contract is not enumerated.
- The four inbound ETH receipt hashes and counterparties are not itemized.
- The helper creation transaction hashes are not itemized.
- The WBNB wrap transaction hash at 01:31:59 UTC is not provided.
- The mirror-image poisoning transaction hash, burn-emitter address, and remaining spam-token identifiers are not supplied in full.
- The full residual BNB route transaction hash and all control-transaction hashes are not provided.
- These omissions limit reconstruction of the individual movements and the helper-creation mapping. The register does not infer missing identifiers.
 0
 0
6 reads
 Become an Investigator