커뮤니티
커뮤니티를 강화하기 위해 인사이트와 팁을 공유하세요.

카테고리

Investigation FindingsExecutive SummaryOn 1 October 2026, a third-party FlashLoopAdapter enabled execution from two Safe accounts. The exploit transaction delivered 114.096151469674448809 ETH to the initiating EOA. The evidence points to delegated module authority, not an exploit of Aave V3 core. SlowMist primary analysis and clarification.The strongest downstream finding is an exact fee split: 114.030726169100264326 ETH was wrapped, 113.745649353677513666 WETH entered the RAILGUN privacy-system proxy, and 0.285076815422750660 WETH went to the protocol treasury. The visible route ends at that privacy boundary; it does not identify a hidden recipient or prove an exchange cash-out.Measure / scopeVerified resultExploit proceeds received114.096151469674448809 ETH; counted oncePrivate-pool transfer113.745649353677513666 WETHTreasury fee0.285076815422750660 WETHScopeEthereum; focused funding and outbound routeInvestigation cutoff4 October 2026, 23:32:47 UTC; block 26122303Evidence basisSentinelTX call traces and receipts, independently checked Etherscan anchors, SlowMist primary analysisCore findingWhat establishes itDelegated authorityVictim-emitted module success logs 1023 and 1030Exact extraction accountingReceipt logs separate collateral, repaid debt, returned loan and ETH proceedsPrivacy boundaryShield receipt separates private-pool transfer and protocol feeFinding 1 — How Did the Safe Accounts Execute Without Owner Signatures?The question is not whether a wallet signed the initiating transaction—it did—but whether the victims’ owners signed the Safe executions that removed assets. The traced exploit used module executions. No owner-signed Safe execution was observed in the inspected call tree.Observed call relationshipEvidence / interpretationAdapter → victim Safe 1Module execution targeting weETH transferAdapter → victim Safe 2Module execution targeting lending-pool withdrawalAdapter → execution helperAdditional module execution frames naming the helper as the SafeCoverage boundary259 frames reported; 134 returned by the trace tool—not a complete replaySlowMist reports that open()/close() checked ISafe(msg.sender).isModuleEnabled(address(this)), allowing a fake caller to answer its own authentication check. It then describes attacker-controlled router.call data targeting genuine victim Safes through execTransactionFromModule. This source-level explanation is attributed research; our call-trace evidence supports the module-execution route, but we did not independently compile or replay the adapter. SlowMist primary analysis and clarification. 0x75328f916b1a0878724d364da5eb12b255160b894cb36c63ed5d718efc616fc4.Receipt corroboration — two victim-emitted success eventsBoth victim Safe contracts emitted ExecutionFromModuleSuccess naming the same adapter. Log 1023 follows the first victim’s weETH Transfer; log 1030 follows the second victim’s Aave withdrawal. These events independently corroborate the module route beyond the partial call trace. They establish successful execution by the named module, but do not by themselves reconstruct the caller’s authorization check or the owners’ earlier decision to enable it. Exploit receipt: decoded event logs.The implication is a separate authorization boundary: enabling a module grants executable authority beyond the ordinary owner-signature path. SlowMist explicitly clarified that Aave V3 core was unaffected. The current enabled-module lists and the complete set of exposed Safes were not enumerated; two observed victims are not a total exposure count.Finding 2 — Which Amount Is the Loss, and Which Is Reused Liquidity?The exploit receipt and internal movements show WETH unwrapped into the execution helper and then paid to the attack EOA. Those two legs describe the same 114.096151469674448809 ETH and must be counted once. 0x75328f916b1a0878724d364da5eb12b255160b894cb36c63ed5d718efc616fc4.QuantityClassificationEvidence boundary114.096151469674448809 ETHExploit proceeds receivedExact internal transfer11,537.239738536922710940 WETHMorpho loan and matching returnExact logs 1014–1015 and 1059; returned liquidity1,335.255802777509633370 WETHDebt repaymentExact Repay event for victim Safe 2, log 10211,449.351954247184082179 WETHSwap outputExact WETH transfer to helper, log 1058The large flash loan provides temporary liquidity for repayment and collateral release. It was returned, so counting it as stolen funds would inflate the incident by two orders of magnitude. Proceeds received are also not necessarily each victim’s gross collateral loss: debt repayment changes the net economic calculation. The receipt now establishes each victim’s exact token movements. A single ETH-denominated loss for each victim still requires an explicit weETH valuation basis and account-state reconciliation.Subtracting only exploit-transaction gas gives 114.092231045147641069 ETH. That is an arithmetic subtotal, not an all-in profit claim: deployment costs, forwarding costs and other activity are not completely reconciled.Victim Safe 1 — direct token removalThe first victim transferred 6.426087021311600894 weETH directly to the execution helper in log 1022. Its own module-success event follows in log 1023. This is an exact token outflow; it must not be relabeled as 6.426087 ETH or added to a WETH figure without a conversion basis. Exploit receipt: decoded event logs.Receipt itemExact resultVictimSafe 1; full account address in evidence appendixweETH outflow6.426087021311600894 weETHTransfer evidenceLog 1022; victim → execution helperModule executionLog 1023; adapter named by victimVictim Safe 2 — collateral removal after debt repaymentThe helper paid 1,335.255802777509633370 WETH against Safe 2’s debt. The Pool Repay event identifies both that victim and the helper as repayer. The Pool then records withdrawal of 1,306.482324969756972729 weETH for Safe 2 to the same helper; the token Transfer corroborates it. Gross collateral removed and debt extinguished are economically different legs. Exploit receipt: decoded event logs.Receipt itemExact resultDebt repaid for Safe 21,335.255802777509633370 WETH; logs 1020–1021Collateral delivered to helper1,306.482324969756972729 weETH; logs 1027 and 1029aToken burn value1,306.482262583889567736; log 1026Accrued balance increase0.000062385867404993; log 1026Module executionLog 1030; adapter named by victimThe aToken burn value plus its logged balanceIncrease equals the underlying weETH withdrawal exactly. Counting the burn, Transfer and Withdraw as three losses would triple-count the same collateral leg. The debt-token Burn likewise separates 1,329.536830578102452349 from 5.718972199407181021 of balance increase; together they equal the 1,335.255802777509633370 WETH repayment. These are receipt reconciliations, not independent cash movements.Helper accounting — why the flash loan cancels outHelper WETH legExact amount / receiptMorpho loan in11,537.239738536922710940 WETH; logs 1014–1015WETH debt repayment out1,335.255802777509633370 WETH; logs 1020–1021WETH swap output in1,449.351954247184082179 WETH; log 1058Morpho loan returned11,537.239738536922710940 WETH; log 1059WETH unwrapped114.096151469674448809 WETH; log 1060The matching loan-in and loan-return cancel. Swap output minus debt repayment equals 114.096151469674448809 WETH exactly, matching the withdrawal event and subsequent ETH receipt. This explains the observed extraction without treating temporary liquidity as incident loss. The helper also retained approximately 0.008411991 weETH in the explorer’s rounded token overview; it is excluded from the exact ETH subtotal because that overview is not an exact balance proof. Exploit receipt: decoded event logs.Combined execution and settlement mapThis supplementary overview connects the module-execution boundary with both collateral outflows and helper settlement. The dashed paths represent authority calls; the dotted path is a repayment prerequisite, not a token transfer. Solid paths show selected asset movements. The flash-loan return is shown separately from extracted proceeds.The diagram rounds amounts to six decimals. The native receipt tables preserve exact quantities; it does not convert weETH into ETH one-for-one or claim a complete execution trace.Finding 3 — What Actually Entered the Private Pool?The forwarding transfer is larger than the exploit receipt because the EOA had pre-existing funding. It cannot be treated as an exclusively stolen-funds figure. The next transaction converts the gross ETH input to WETH and divides it between the privacy-system proxy and treasury. 0x3a5663d9a3d32bdea3c3012fd9dbaf490195ed413204c4db8f1097e1e7f753f9. 0xa20636bf3792f705ae51a48afdec336fb0518cd43365a8fc3e596dea23266dc9.Shield receipt legExact WETHLogWrapped input114.030726169100264326262Transfer to privacy-system proxy113.745649353677513666266Transfer to treasury0.285076815422750660267Shield eventSupports the amount / fee split268The allocation chart below uses a shared linear WETH scale. The fee bar is intentionally tiny: enlarging it without a separate scale would misrepresent the 0.25% allocation. Chart labels are rounded to six decimals; the native table above preserves the full values and receipt indices.The two transfers sum exactly to the wrapped input. The treasury fee is 0.25% rounded down at token precision; transaction gas of 0.001793902352363730 ETH is separate. The treasury leg is a protocol fee—not evidence of cash-out, common ownership, or a recovery target. We independently checked these visible Etherscan logs against the SentinelTX follow-up result.Timeline — Funding, Execution and DispositionAll times below are UTC on 1 October 2026. These are selected transaction anchors, not a claim that every intervening transaction has been accounted for.UTC / blockEventAmount14:15:23 / 26098000RAILGUN withdrawal funds attack EOA0.049875 ETH net received15:08:47 / 26098264Exploit helper pays attack EOA114.096151469674448809 ETH16:45:59 / 26098748Attack EOA forwards to intermediate EOA114.130726169100264326 ETH16:46:59 / 26098753Intermediate EOA sends Relay Adapt input114.030726169100264326 ETHFunding to exploitation took 53 minutes 24 seconds. The creation transaction preceded exploitation by six minutes; forwarding followed exploitation by 1 hour 37 minutes 12 seconds, and shielding followed forwarding by 60 seconds. These measured intervals are consistent with a prepared execution sequence, but do not identify a person or prove coordination with any service operator.Helper creation — a direct infrastructure anchorThe creation transaction at block 26098235, 1 October 2026 15:02:47 UTC, was signed by the same initiating EOA and sent to a separate contract; the explorer identifies the helper as created within that transaction. This establishes a transaction-level infrastructure link. It does not justify calling the EOA the direct CREATE caller without inspecting the creation call frame. 0x0c2bbaf2b5ebf1102e0df4acb1bcc2c7bc920896c45da6f85b4e9442506a3884.Creation anchorObserved resultTransaction signer0x42c2633438609881c8fBAb82414eb9A0c45F9353Transaction target0x4a418c7132d452705a2123e95B5b9bFdF3b1f84aCreated helper0xf09168963ac7b31917a02aa82fa9cd667f4b67ffUTC / block2026-10-01 15:02:47 / 26098235Creation transaction0x0c2bbaf2b5ebf1102e0df4acb1bcc2c7bc920896c45da6f85b4e9442506a3884Wallet network — how the public route connectsThe account-level overview below joins the victim collateral legs with the directly observed outbound route. V2 collateral is delivered by the Aave token contract, not by a direct Safe token transfer. The funding origin is a separate earlier privacy-service withdrawal; using the same public infrastructure does not prove a shared hidden owner. Exact transaction anchors remain in the evidence appendix.Diagram nodeFull Ethereum account / contractV1 · Victim Safe 10xe3b23e47df7cd85876ac6cb05bdb9d7cd5b28520V2 · Victim Safe 20xcfedf95a3653a128dfc2e4288758a1a1850d169fH · Execution helper0xf09168963ac7b31917a02aa82fa9cd667f4b67ffA · Attack EOA0x42c2633438609881c8fBAb82414eb9A0c45F9353R · Forwarding EOA0x951ad21b85c1ce165f15d548a7c7d42520a32f1aS · Relay Adapt0xac9f360ae85469b27aeddeafc579ef2d052ad405P · Privacy-system proxy0xfa7093cdd9ee6932b4eb2c9e1cde7ce00b1fa4b9T · Protocol treasury0xe8a8b458bcd1ececc6b6b58f80929b29ccecff40Aave Pool0x87870bca3f3fd6335c3f4ce8392d69350b4fa4e2Morpho flash lender0xbbbbbbbbbb9cc5e90e3b3af64bdaf62c37eeffcbThe role-labelled nodes are verified account or contract anchors, not a common-owner cluster. The 114.130726 ETH forwarding transfer exceeds the exploit receipt because it includes pre-existing balance. Relay Adapt wraps 114.030726 ETH, then the receipt splits WETH between the privacy-system proxy and treasury. The treasury payment is a protocol fee, not attacker cash-out. No verified edge continues from the private pool to a hidden withdrawal or exchange.Connection Evidence — Direct Transfers Are Not Identity EvidenceA same-transaction call chain directly connects the initiating EOA, helper, adapter and victim executions. Two later transaction hashes directly connect the initiating EOA to the forwarding EOA and Relay Adapt. These are transaction relationships, not human attribution.Proposed connectionEvidence levelConclusionAttack EOA → helper → adapter → victimsDirect inspected call traceExecution relationship establishedAttack EOA → forwarding EOA → RAILGUNDirect value transfersVisible disposition route establishedFunding withdrawal and shield use same public serviceShared service patternDoes not establish hidden owner continuitySimilar-looking addressesPotential poisoningDo not merge into attacker clusterPost-shield withdrawal of similar sizeHeuristic onlyAmount / timing alone cannot attribute fundsLimits and Alternative InterpretationsThe traced scope is Ethereum. Two reported Optimism activities were not inspected. The exact exploit receipt and helper creation transaction were checked in this revision. Adapter source code, a complete replay, incident-block module lists, the precise CREATE caller and each victim’s pre/post account valuation remain unestablished. Historical owner/setup claims from the first automated result were withdrawn in the follow-up and are not used here.The RAILGUN funding-transaction signer may be an independent relayer. Shared public infrastructure does not identify an operator. No exchange endpoint was identified in the inspected routes; that is narrower than proving no exchange cash-out occurred. The private-pool transfer cannot be followed to a particular hidden withdrawal using these public records alone.Visible noncustodial EOA balances are not automatically freezeable. We also do not describe the helper’s deployment as the only remaining lead: unexamined histories, module exposure and alternate infrastructure remain separate questions.Incident-Specific Response PointsQuestionPractical investigation actionWhich Safes retain this authority?Enumerate adapter-enabled Safes and incident-block module lists; validate current exposure before remediationHow much did each victim lose net of debt?Use the exact receipt legs established here; reconcile pre/post positions and a documented weETH valuation basisWas infrastructure reused?Inspect the creation call frame and transaction target history; the signing EOA is now directly linked to helper creationCan downstream funds be attributed?Treat pool exit matches as leads; require independent evidence before attribution or exchange requestsFor affected account operators, the relevant control is the specific module’s execution authority. A verified vulnerable-module exposure warrants targeted module revocation and preservation of account state and receipts. This is distinct from a blanket assertion that Safe or Aave core is compromised.Evidence Appendix — Ethereum Account AnchorsRoleFull addressAttack EOA0x42c2633438609881c8fBAb82414eb9A0c45F9353Execution helper0xf09168963ac7b31917a02aa82fa9cd667f4b67ffThird-party adapter0x16bb8b912da187870c23ec6756bb3fad061283d8Victim Safe 10xe3b23e47df7cd85876ac6cb05bdb9d7cd5b28520Victim Safe 20xcfedf95a3653a128dfc2e4288758a1a1850d169fForwarding EOA0x951ad21b85c1ce165f15d548a7c7d42520a32f1aRAILGUN Relay Adapt0xac9f360ae85469b27aeddeafc579ef2d052ad405RAILGUN privacy-system proxy0xfa7093cdd9ee6932b4eb2c9e1cde7ce00b1fa4b9RAILGUN Treasury0xe8a8b458bcd1ececc6b6b58f80929b29ccecff40Evidence Appendix — Contract and Asset AnchorsRoleEthereum addressweETH token0xcd5fe23c85820f7b72d0926fc9b05b43e359b7eeWETH token0xc02aaa39b223fe8d0a0e5c4f27ead9083c756cc2Aave Pool V30x87870bca3f3fd6335c3f4ce8392d69350b4fa4e2aEthweETH token0xbdfa7b7893081b35fb54027489e2bc7a38275129Variable debt WETH token0xea51d7853eefb32b6ee06b1c12e6dcca88be0ffeMorpho flash lender0xbbbbbbbbbb9cc5e90e3b3af64bdaf62c37eeffcbHelper creation transaction target0x4a418c7132d452705a2123e95B5b9bFdF3b1f84aEvidence Appendix — Transaction AnchorsRoleFull transaction hashHelper creation0x0c2bbaf2b5ebf1102e0df4acb1bcc2c7bc920896c45da6f85b4e9442506a3884Funding withdrawal0xc5dc2606e42ebfad29fce601056248b9b3f3571318c9a0de2910ac7c0363852bExploit0x75328f916b1a0878724d364da5eb12b255160b894cb36c63ed5d718efc616fc4Forwarding0x3a5663d9a3d32bdea3c3012fd9dbaf490195ed413204c4db8f1097e1e7f753f9Shield / fee split0xa20636bf3792f705ae51a48afdec336fb0518cd43365a8fc3e596dea23266dc9Source and Method NotesPrimary mechanism and scope clarification: SlowMist primary analysis and clarification. Incident index: SlowMist Hacked. Transaction references above are Etherscan records. SentinelTX was used for the original call-trace and downstream receipt analysis. This revision directly checked the exploit receipt’s decoded events and the helper creation transaction in Etherscan; the shield accounting and exploit anchor were cross-checked against visible explorer records. The report separates directly observed transfers, attributed source-code findings and analytical inference.The central result is a module-authority route yielding a precisely observed ETH receipt, followed by a fee-reconciled privacy-pool entry. A large flash loan is not the loss figure, a protocol fee is not cash-out, and a privacy endpoint is not an identified attacker.Revision note — 5 October 2026: added exact victim-level receipt accounting, helper creation evidence, a measured UTC timeline, a proportional shield-allocation chart and clearer directional diagrams. The original investigation window ends at block 26122303 (4 October 2026 23:32:47 UTC); this revision does not claim a complete scan of later activity.
Executive SummaryPublic research describes an Aquifer Solana venue exploit on 31 August 2026. This investigation separates the reported exploit mechanism from the later transaction-anchored proceeds trail. Ethereum records confirm a transfer of 1,000.795547188808275967 ETH on 1 September to a relay address. Eleven subsequent Arbitrum USDC transfers to a contract labeled Hyperliquid: Deposit Bridge 2 total 2,470,625.249359 USDC.The deposit total does not establish a current Hyperliquid balance, the identity of the operator, or an ability to freeze assets. The Solana provenance of the largest Ethereum arrival remains unresolved. Reported counts of 212 calls and 18 vaults were not independently re-enumerated.The Finding in One ScreenMeasureScope / evidence boundary1,000.795547188808275967 ETHOne Ethereum handoff, 1 September 2026, 20:37:23 UTC2,470,625.249359 USDCGross sum of 11 Arbitrum deposits, 4–6 September 2026; not current holdings1 supported CCTP pairTen other routes remain correlations, not fully established message matchesHistorical evidence windowDeposit ledger ends 6 September 2026, 02:40:26 UTC; not a live balance snapshotSource boundaryRetained investigation and explorer checks from the original report; editorial revision adds no new tracingThree Findings That Matter1. The EVM handoff is anchored to a transaction. The large ETH transfer is directly identified. It does not resolve its complete upstream Solana provenance.2. The destination is a deposit endpoint, not a final location. Eleven transfers establish gross USDC deposits. They do not establish current account holdings, identity or recoverability.3. Cross-chain confidence is uneven. One fee-adjusted burn/mint pair is supported in retained evidence. Matching amount and time alone are insufficient for the other ten routes.When Did the Verified Trail Move?UTC, 2026EventInterpretation31 AugustReported Solana exploitPublic research context, not independently re-executed1 September 20:37:231,000.795547188808275967 ETH handoffEthereum transaction anchor4 September 20:16:47First of 11 USDC depositsStart of the retained Arbitrum deposit window6 September 02:40:26Last deposit: 249,792.579308 USDCEnd of this ledger, not proof activity stoppedWhich Ethereum Transfer Anchors the Trail?A successful Ethereum transfer on 1 September at 20:37:23 UTC forwarded 1,000.795547188808275967 ETH from the explorer-labeled Aquifer Exploiter 1 address to the relay. This is a verified transaction anchor, not proof that every upstream Solana transfer has been matched.FieldVerified valueTransaction0x728294f756bf1f2f35fb32d9c5a18b5f65f9e78cdc2fae72544a64ffb8004800Block / status25,884,871 / SuccessETH transferred1,000.795547188808275967ETH transaction fee0.000022413007617The dashed Solana segment marks unresolved provenance; the deposit endpoint does not imply current holdings.What Do the Eleven Deposits Establish?The retained ledger records eleven successful transfers from the same Arbitrum depositor to the explorer-labeled deposit contract. Their gross sum is 2,470,625.249359 USDC. The full transaction ledger is preserved in Appendix B below.The destination is explorer-labeled Hyperliquid: Deposit Bridge 2. These transactions establish deposits to that contract. They do not establish the subsequent trading-account balance, withdrawals, beneficial ownership, or the availability of a freeze mechanism. Those conclusions require separate evidence.Which Cross-Chain Pair Is Supported?SentinelTX saved evidence supports one Ethereum burn and Arbitrum mint pair using decoded message fields and matching amounts. The other ten routes remain amount-and-time correlations. A message hash and attestation were not established in the retained evidence, so this report does not claim complete cryptographic proof for all routes.StageUSDCEvidenceEthereum burn249,820.128254Decoded source amountExecuted fee27.548946Decoded feeArbitrum mint249,792.579308Burn minus feeFinal deposit249,792.579308Independently checked Arbiscan transferRecordTransactionEthereum burn0xe169519295399ed8d548480c77b1c01d97538bf2de99d3371adfbd2646d67f5aArbitrum mint0xb02754f975a86c91f3ebdfab98723c9e8e431047293beab7dd304a0afdcb7497The fee-adjusted mint equals the last verified deposit. This figure illustrates one supported pair, not a universal proof of every route.Why Must the Privacy Branch Be Kept Separate?A separate relay-funded branch received 1 ETH and interacted with wrapping and shielding infrastructure. Its amounts must not be confused with the much larger Arbitrum deposit route or with total activity in a shared helper contract. The following values come from the saved SentinelTX investigation, not a fresh independent replay of every internal call.StageAsset / amountMeaningRelay funding1 ETHBranch seedWrap-helper input0.999709712414154961 ETHSaved internal-call evidenceShield amount0.9959140645635465 WETHCase-specific branchFee output0.002496025224470041 WETHSaved fee transferUnreconciled difference0.00129962262613842 WETHDo not assign a destination without evidenceThe lower branch is separate from the main Arbitrum deposit route. Its unreconciled remainder is explicitly retained rather than assigned by inference.RoleEthereum address / transactionBranch wallet0xbc8d344b12c728707eb005b123786f3cd22e905cFunding transaction0xd2b4fee82f7322128fe1ffebb9697f6af3ee829ab6d2951419c1c3d0bea73485Shield transaction0x699cb2d44ec16685e6a7ae4f17a08798300beb4378ca66c0a8957a643b931d20The shared helper’s aggregate volume is not Aquifer proceeds. The earlier 54.53 WETH preview is not attributed to this case. A later call from the branch wallet remains unverified; the privacy boundary prevents a supported claim about its final owner or destination.What Remains Unproven?QuestionCurrent evidenceRequired next checkLargest Solana-to-Ethereum arrivalProvenance unresolvedMatch source bridge recordAll CCTP routes paired?One supported; ten correlatedCompare message identifiers and attestationsFunds still on Hyperliquid?Deposits onlyEstablish account-level onward activityWho operated the wallet?No human attributionIndependent attribution evidenceGross deposits equal stolen funds?Not fully establishedReconcile every inbound source and dustWhere Further Investigation Can Change the Conclusion?The useful next steps are evidence-specific, not generic wallet advice. Each would resolve a different boundary in this case.Evidence gapNext actionWhat it could establishSolana provenanceMatch source bridge execution to the Ethereum arrivalWhether the large arrival is attributable to the reported exploitTen correlated CCTP routesCompare decoded message identifiers and attestationsWhich cross-chain pairs are directly supportedAfter the deposit endpointObtain attributable account-level onward activitySubsequent movement or holdings; not implied by depositsPrivacy branch remainderReconcile internal calls and feesWhether the unassigned difference has a supported destinationThese are proposed verification actions, not claims that a service can freeze funds or that recovery has occurred.ConclusionThe strongest result is a transaction-anchored EVM trail: one large ETH handoff and eleven independently verified Arbitrum USDC deposits. The key analytical distinction is between seeing a deposit endpoint and proving where the money is now. Upstream provenance, complete cross-chain message matching, and onward account activity remain separate questions. Neither a service label nor a matching amount establishes an operator’s identity.Appendix A — Full Incident AddressesRoleAddress / networkEvidence boundaryReported exploit wallet7fTe9pvrwXJRBHq9MaSyVPR4PgEuhqLiA93Dxf4gRk7JSolanaPublic incident anchor; selected transfers tracedEthereum arrival0x2Dfe9e969796e2797278b02761dd9Ad6aE922746Forwarded 1,000.795547188808275967 ETHRelay / depositor0x200e52350fbc579c96bad87b6ef782c1f962dffdArbitrum; same address also used on EthereumSender of all 11 verified depositsDeposit destination0x2df1c51e09aecf9cacb7bc98cb1742757f163df7ArbitrumExplorer label: Hyperliquid: Deposit Bridge 2; onward balances not establishedAppendix B — Full Arbitrum Deposit LedgerAll eleven transactions below were checked against visible Arbiscan records: successful status, the same sender and destination, and native Arbitrum USDC. Times are UTC in 2026. The total is gross deposited USDC, not a current account balance or independently proven total stolen proceeds.UTC / sequenceUSDCTransaction1 · 09-04 20:16:472,453.9642340x5ca132222846c1e54b7ff42cd57869cb9734b23e34c1309ba7920e88c4ccea002 · 09-04 20:24:12243,041.1311030x2841ebcd439b5a22d1874d16a34c35e1aabada620bc54e2e93c2b796b421f4323 · 09-05 00:28:49245,361.5044680xfebdb16f6dd1ece48e0321da5acf80adc6a110a62ae8bd070936de4808d136734 · 09-05 02:41:46244,958.4719630x2e87862888319a4c1adcdab04d80f45a06172bd2e150156c80f26d0013ca4b275 · 09-05 04:47:32244,776.9320260xd37f8c85728d2539dca14f5c4ec54084c0270fe871f891f76910137569130a446 · 09-05 17:15:46247,930.4844880x44b89b44235aa3990a8c6fe12ce948a5e301b6bf9ba3dc1c48d3e87d718290c47 · 09-05 20:11:06247,586.8793160x4fa683c1804963b151fbbf36cd33420f0b0b24900d8837db9472069cbf9a742d8 · 09-05 22:15:04248,624.1728560x1af9d9423bb06d4002616c928ffbbc6637a36a6f4e6f817873750366bc4e78339 · 09-05 23:18:24247,966.9649290xdd1b18847b4dc17419fc0af0b30df967773f852eb934d7d6b972da963938ea8610 · 09-06 00:16:16248,132.1646680x0832c6bd5077ee6230bbbe1f4882d37d8fe03676b6c48d050bc8b4e9681f8b4311 · 09-06 02:40:26249,792.5793080x3933bb6d2e80de8365e92ec226df853a19f408206ead21589e96fb4b7e43fcf8Total · 11 deposits2,470,625.249359Nonces 0–10Sources and Revision ScopeThe report combines the saved SentinelTX investigation with visible Etherscan and Arbiscan transaction checks. Public incident context: Bitquery Aquifer investigation. Reported exploit counts and mechanism are public research, not an independent re-execution performed for this report. The full transaction links above identify the directly checked transfer evidence.Editorial revision: 6 October 2026. The structure and explanations were revised; no new on-chain observations or current-balance claims were added.
Executive SummaryOn 24 September 2026, Payy Network’s Ethereum RollupV1 bridge paid 1,918,792.198148 USDC to the same recipient across two verifyRollup batches. Both calls were submitted by Payy’s usual batch-posting address. The first payment was rapidly moved to a second contract, converted through UniswapX into approximately 683.38 ETH, and split across four wallets.By 26 September, three relay paths had deposited a transaction-anchored total of 682.3 ETH into the Tornado Cash Router. A fourth branch retained 1 ETH. The later 90,202.820016 USDC payout remained at the primary recipient; its verified genuine-USDC balance was 90,202.821244 USDC at the 28 September cutoff.Payy’s initial root-cause update ruled out a compromised key, social engineering, and an exploit of its off-chain infrastructure. The company has not yet published the validated technical cause. The call path proves that verifyRollup processed the payouts; it does not by itself prove which verification or authorization invariant failed.Incident AnchorsItemValueEvidenceNetworkEthereumOn-chainBridge / rollup contract0x367C1eAF14AA06b78ce76bd0243297de79d85270Contract historyBatch poster0x5343B904Bf837Befb2f5A256B0CD5fbF30503D38tx.from in both batchesPrimary recipient0xAa4985dBDaBfACa344237D40F7E06C4a0BB57E70USDC Transfer logsSwap / distribution contract0xb483B1742aaD0a60a9FC91bb36C5a42dbE3F3D38USDC and ETH flowFirst drain block26,044,909On-chainFirst observed time2026-09-24 04:21:23 UTCOn-chainPrimary-recipient total1,918,792.198148 USDCTwo verified transfersTwo verifyRollup BatchesTime (UTC)BlockTransactionAmount to primary recipient2026-09-24 04:21:2326,044,9090xf43abdac5422087f645d77923eb1c825178bff3eb86d17d40fa18d89701e18141,828,589.378132 USDC2026-09-24 09:30:3526,046,4390xda88fb9273c703a4d2647c744362f58b6db4e104d7a203a75d4b67e3d54858c890,202.820016 USDCThe first batch included ordinary-looking withdrawals to other addresses as well as the dominant transfer to the primary recipient. The second batch used the same function, bridge, submitter, and recipient.Conversion and Initial ETH SplitAt 04:22:59 UTC, the primary recipient transferred 1,828,594.895417 USDC to 0xb483B1742aaD0a60a9FC91bb36C5a42dbE3F3D38 in transaction 0xb2fd99c115ad98162149fa1e0e8243050d3009719910e00bff16808a12ca10e7. Public reporting identifies the conversion venue as UniswapX. The subsequent ETH distributions sum to approximately 683.38205 ETH.DestinationAmount receivedFirst-hop transactionStatus0xa3dD31d9aD9A7eCAC68c2d2cF6063DfEa7bA3cAe1.000000 ETH0xd68af00a8693f154f1daf576e6a91a966c6b0909617a412d0471cb15678b6ca0Retained0xe8d566E2f914dbd8309625e1792ed21fD0431956282.382139990140 ETH0x7987458cae1d4424b5555c4a50cda01a31a5b08469cd6ab4c35d9b32acf09b95Forwarded0x888A21c48cF442e312bddd7c24B678f0C7132a2a200.000000 ETH0xd2ef52f0497a693bf3fe25b3584c5ec1b85d901c9ca8c4e0997f5e1a61074f1aForwarded0x3d092740936dA4C5693DaE3633c7207A37F40104199.999911680412 ETH0x0b41b66d5e4158a82b5ca8adacf87a1b96fe79bd9e8da5b38b8c9551f4289a9eForwardedTornado Cash Deposit PathsOn 26 September, three relay wallets deposited 682.3 ETH into the Tornado Cash Router at 0xd90e2f925DA726b50C4Ed8D0Fb90Ad053324F31b. The transactions used the router’s deposit method. The total is calculated from transaction values, not an estimated USD conversion.Source branchRelay walletDeposit window (UTC)CountTotal0xe8d566E2f914dbd8309625e1792ed21fD04319560xF46e1e8Ca9a032f1C84b1451890ad0aedb5E0BeD06:09:35–06:19:599180.0 ETH0x888A21c48cF442e312bddd7c24B678f0C7132a2a0x2072f325f0Bb7e06c1D7C933a10886f794D4CC9906:46:11–07:11:118302.3 ETH0x3d092740936dA4C5693DaE3633c7207A37F401040x21D4A32a357c77e72dCe79810d54C7FCf5A1996907:16:23–07:17:112200.0 ETHTotal3 relays06:09:35–07:17:1119682.3 ETHRelayFirst Tornado deposit transactionLast Tornado deposit transaction0xF46e1e8Ca9a032f1C84b1451890ad0aedb5E0BeD0x7de4955568c12e82d0cea9bc08d18715414c45b612ec270b5fa171ae74775db30x1cfb681a5bb2567ca6c68facbf65f9decc239eedd73248de27193103705a9cf60x2072f325f0Bb7e06c1D7C933a10886f794D4CC990xe5dfd95a2710f45d1749d99c941200f0b5831b25ec92239ff3e9800e60b6dbf20xb9958c2a8828865936c53cac3967434381584e6753d0a09da579972ead8a9de60x21D4A32a357c77e72dCe79810d54C7FCf5A199690x2097d151c2efe641673d3a6e772817c5baefcfbb550d5e0ade1cb49cbd91611a0x0415dc1ff16cc17c6862b9ee27c1ebfbb2e30705d8f5e6157989e7618ecf64f4No centralized-exchange deposit was identified before the mixer deposits. The router entry breaks deterministic forward tracing; it does not identify the controller of any eventual withdrawal.Verified Balances and StatusAddressAsset / balance at 28 Sep cutoffStatus0xAa4985dBDaBfACa344237D40F7E06C4a0BB57E7090,202.821244 genuine USDCLater payout remains visible0xa3dD31d9aD9A7eCAC68c2d2cF6063DfEa7bA3cAe1.000000 ETHRetained branch0xe8d566E2f914dbd8309625e1792ed21fD0431956~0 ETHForwarded to relay0x888A21c48cF442e312bddd7c24B678f0C7132a2a~0 ETHForwarded to relay0x3d092740936dA4C5693DaE3633c7207A37F40104~0 ETHForwarded to relay0x21D4A32a357c77e72dCe79810d54C7FCf5A199690.028009 ETHResidual after depositsThe primary recipient also displays a separate token using the symbol “USDC” at another contract. This report excludes that token and counts only Circle’s Ethereum USDC contract, 0xA0b86991c6218b36c1d19D4a2e9Eb0cE3606eB48.Evidence AssessmentStatementAssessmentBasisTwo bridge batches paid the same recipientConfirmedReceipts and USDC logsBoth calls used verifyRollup and the usual batch posterConfirmedCall data and tx.fromRoughly 683.38 ETH was produced and splitConfirmed at distribution layerETH transfers from 0xb483…3D38682.3 ETH entered Tornado Cash RouterConfirmed19 direct deposit transactionsCompromised key or social engineering caused the incidentNot supported; Payy says initial RCA ruled these outOfficial Payy updateA specific proof-validation or authorization bug caused the incidentUnresolvedNo validated post-mortemA named person or organization controls the walletsUnresolvedNo identity evidenceResponse PrioritiesPriorityActionReason1Preserve both verifyRollup transactions, calldata and validator/prover artifactsNeeded for root-cause reconstruction2Monitor 0xAa49…7E70 and genuine USDC balance90,202.821244 USDC remains visible3Monitor 0xa3dD…3cAe1 ETH remains outside the mixer path4Provide the 19 Tornado deposit hashes to investigatorsPreserves precise entry amounts and times5Publish the validated post-mortem and user-remediation planFailure mode and reimbursement status remain unresolvedConclusionThe strongest forensic conclusion is not merely that Payy’s bridge lost about $1.92 million. The value followed two distinct post-drain states: 90,202.821244 genuine USDC remained at the primary recipient, while nearly all ETH created from the first tranche was split, relayed, and deposited into Tornado Cash less than three days later.The transaction history supports a deliberate laundering sequence. It does not establish the technical root cause or the identity of the operator. Those questions require Payy’s validated post-mortem, preserved rollup artifacts, and any later mixer-withdrawal correlation.SourcesPayy incident noticePayy root-cause updateUnchainedThe Crypto TimesiTokenly incident registryEthereum records: Etherscan and BlockscoutSentinelTX case: b92968a7-ee47-4f17-a260-1e5ebfc16a09
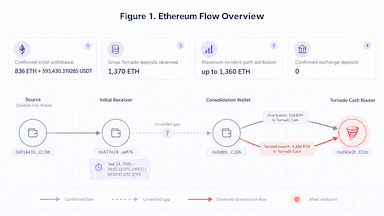
On September 24, 2026, crypto casino Duelbits reported a security incident affecting operational hot wallets across multiple blockchains.Public reporting cited in the investigation estimated the total loss at approximately $7 million, involving Ethereum, Solana, BNB Chain, Bitcoin, and Tron.ChainBounty analyzed the Ethereum leg of the incident, beginning with a confirmed withdrawal from a Duelbits-labeled hot wallet and tracing subsequent ETH movements through newly created intermediary wallets.The investigation identified 20 deposits totaling 1,370 ETH into the Tornado Cash Router between September 26 and September 28.However, the full 1,370 ETH cannot be attributed to the Duelbits incident with equal confidence. Based on transaction-level value paths currently anchored on-chain, up to 1,360 ETH of the Tornado Cash deposits can be explained by the tracked incident flow.No outbound exchange deposit was identified within the investigated path.Executive SummaryFinding Result Incident dateSeptember 24, 2026Blockchain analyzedEthereumConfirmed initial withdrawal836 ETH + 593,430.319285 USDTFirst receiving wallet0xA77e24Fe29d16E051e487ef4Ea7b056cb05aef76Reported consolidation wallet0x8dB9D7f0a03d212c566Ca80c66e294CeCC20C306Observed outbound movement from consolidation wallet1,914.1 ETHReturned to consolidation wallet540.0 ETHTornado Cash deposits observed1,370 ETH across 20 transactionsMaximum explained by tracked incident path1,360 ETHConfirmed exchange deposits in traced outbound flow0Consolidation-wallet balance at investigation snapshot973.536981 ETHInitial receiving-wallet balance at snapshot25.566884 ETHEvidence ClassificationClassification Meaning ConfirmedDirectly supported by transaction-level or address-attribution evidenceObservedTransaction path is directly anchored, but its attribution to the incident may depend on additional contextAnalytical assessmentInterpretation of observed behavior rather than independently proven intentUnverified leadPotentially relevant connection requiring additional evidenceThis distinction is critical throughout the investigation.An address interaction can establish that two entities touched the same infrastructure. It does not, by itself, establish that the investigated funds moved between them.1. Initial Withdrawal From the Duelbits Hot WalletThe Ethereum investigation begins with:0x014435B1E39945CF4f5F0c3cbb5833195A95CC9BThe address was attributed to Duelbits in the attribution data used during the investigation.Its first recorded activity occurred on February 14, 2024.At approximately 09:02 UTC on September 24, two major transfers left the wallet only 36 seconds apart.Time (UTC) Block Asset Amount Destination Transaction 09:02:1126046298USDT593,430.3192850xA77e24...aef760x4f2bc2a8...9bb73909:02:4726046301ETH836 ETH0xA77e24...aef760xcdc0b6dfac...3182dFull transaction hashesAsset Transaction hash USDT0x4f2bc2a8bc5040788c71e712546deec6d0f61529518b8114b0334ffd3e9bb739ETH0xcdc0b6dfacbefe4aef640be1538c9081bbf401ca9ad9784e1b0cfc044523182dThe receiving wallet,0xA77e24Fe29d16E051e487ef4Ea7b056cb05aef76was a previously unseen EOA whose first activity occurred on September 24.At the investigation snapshot, it retained 25.566884 ETH.What the blockchain proves — and what it does notBoth transactions were signed by the Duelbits hot wallet itself.That matters.From Ethereum transaction data alone, an investigator cannot distinguish an authorized withdrawal from a withdrawal executed by someone who obtained legitimate signing authority.The classification of these transactions as part of the reported compromise therefore relies on the incident disclosure and associated public reporting.The Ethereum transactions themselves show ordinary signed transfers rather than direct exploitation of a smart contract.2. The Missing Link to the Consolidation WalletPublic reporting identified the following address as the primary ETH consolidation wallet:0x8dB9D7f0a03d212c566Ca80c66e294CeCC20C306The wallet first became active on September 24.However, the investigation did not identify a direct value transfer from the initial receiver 0xA77e24... to the consolidation wallet 0x8dB9....Instead, two common counterparties were found.Address Activity Sent transactions Snapshot balance Label 0x181a638038a4bd75c207d080de83e217f8e8a1d7September 24 only60.000031 ETHNone0x4293b5dc11b250078da7359d7d57c15eecfcf70aJan. 2018 – Sep. 20263800.000547 ETHNone0x4293... is particularly notable because it sent funds to both the initial receiving wallet and the consolidation wallet.That creates a meaningful investigative lead.It does not yet create a verified value path.The transaction amounts and transaction hashes required to demonstrate that the investigated value moved through these common counterparties were not anchored in the current evidence set.ChainBounty therefore classifies:Connection Status Duelbits hot wallet → 0xA77e...Confirmed0xA77e... → 0x8dB9...Unverified value path0x8dB9... → downstream intermediary walletsObserved and transaction-anchoredDownstream intermediaries → Tornado CashObserved and transaction-anchoredThis gap prevents the entire Ethereum path from being presented as one uninterrupted forensic chain.3. A 0.1 ETH Route TestOn September 24, the consolidation wallet performed a small round-trip transfer involving another address.Direction Amount Transaction Consolidation wallet → 0x922adc...8cd230.1 ETH0x0edf6e07...bfe52b0x922adc...8cd23 → consolidation wallet0.1 ETH0x5eaf7ef1...a3f1aFull hashes:0x0edf6e07817a6d2eafd3f42c3d40c7dcab4756d4375286d48f26654dc9bfe52b0x5eaf7ef13016fd76a822f046935ca7b78f76bc66095249f8a8d8fec2d79a3f1aA 0.1 ETH round trip alone does not prove intent.Placed alongside the substantially larger transactions that followed, however, it is consistent with route validation before larger fund movements.That interpretation remains an analytical assessment rather than a directly provable fact.4. First Laundering Branch: 110 ETHBetween September 26 and September 27, the consolidation wallet began distributing ETH through newly activated intermediary wallets.The first branch started with:0xa31bb1fdf3409ce863bf646b69e6013ca74c38e3Consolidation Wallet → First IntermediaryDate Amount Transaction Sep. 2611 ETH0x2fa0bf95...12fac6Sep. 261 ETH0x928dccb8...286260Sep. 26650 ETH0xd9186462...62d801Total662 ETHMost of that ETH did not continue toward the mixer.First Intermediary → Consolidation WalletDate Returned amount Transaction Sep. 261 ETH0x98d87960...c0d83Sep. 26480 ETH0x391989db...03c1Sep. 2758.9 ETH0x29436031...0c8Total539.9 ETHAnother 111.1 ETH was forwarded to:0xadb82eef7baa2feaebe64f88577c06f803a2c578Date Amount Transaction Sep. 2610.1 ETH0xe4e83e46...896a5Sep. 27101 ETH0xaa3ff3bc...75ff6Total111.1 ETHThat wallet then deposited 110 ETH into the Tornado Cash Router:0xd90e2f925da726b50c4ed8d0fb90ad053324f31bDeposit Amount Transaction 110 ETH0xf12cf53b...d86af2100 ETH0xccaf6baa...5349Total110 ETHThe remaining 1.094278 ETH was returned upstream.This 110 ETH branch is fully explainable using the tracked transaction path.5. Second Laundering Branch: 1,260 ETHThe second and significantly larger movement occurred on September 28.The consolidation wallet transferred 1,252 ETH into a newly active address:0x6495afaeb766e59f3b725e6ef6e5622b44b272c3Consolidation Wallet → 0x6495...Amount Transaction 1 ETH0x2fb2fc01...709e3650 ETH0x72c887a4...b265e601 ETH0x425b31b4...e8a61,252 ETHThat wallet subsequently transferred 1,250 ETH into:0x56644f6a348a142d38fb7dde2e942c9ef03d09fcAmount Transaction 1 ETH0x5b6d00a9...ba07c500 ETH0xe8384b80...cff6f500 ETH0xb9424aa...bdc58249 ETH0x8471f89d...e6b5a1,250 ETHThe final intermediary then executed 18 Tornado Cash deposits.Tornado Cash Deposit StructureDenomination Transactions Total 100 ETH121,200 ETH10 ETH660 ETHTotal181,260 ETHIt also returned 1.905145 ETH upstream.This creates an important accounting issue.Observed activity at 0x56644f... ETH Tracked incident-path inflow1,250Tornado Cash deposits1,260Returned upstream1.905145Total observed outflow1,261.905145Outflow exceeding tracked inflow11.905145The intermediary therefore spent approximately 11.905145 ETH more than it received from the tracked upstream address.The origin of that additional ETH falls outside the investigated outbound path.As a result, ChainBounty does not attribute the full 1,260 ETH from this wallet to the incident.The maximum amount supported by the tracked inflow is 1,250 ETH.6. Why 1,370 ETH Does Not Equal 1,370 ETH of Attributed Incident FundsThe distinction can be summarized as follows.Branch Gross Tornado deposits Maximum explained by tracked incident path First branch110 ETH110 ETHSecond branch1,260 ETH1,250 ETHTotal1,370 ETHUp to 1,360 ETHThis is one of the most important findings in the investigation.The observed wallets deposited 1,370 ETH into Tornado Cash.But evidence-backed attribution should stop at 1,360 ETH unless the additional funding source at 0x56644f... can also be tied to the incident.A clean transaction graph is not the same thing as a proven provenance graph.7. Consolidation-Wallet Flow SummaryThe observed movements from the consolidation wallet can be summarized without double-counting as follows.Flow Amount 0.1 ETH test transfer0.1 ETHFirst intermediary branch662 ETHSecond intermediary branch1,252 ETHGross value sent from consolidation wallet1,914.1 ETHReturned to consolidation wallet540.0 ETHGross Tornado deposits from downstream wallets1,370 ETHConsolidation-wallet balance at snapshot973.536981 ETHThe wallet's complete inbound history was not reconstructed as part of this outbound tracing exercise.The 973.536981 ETH balance should therefore not automatically be treated as entirely stolen Duelbits funds.It is a monitored balance associated with the reported consolidation wallet, not a fully attributed recovery amount.8. The Laundering TypologyThe downstream activity shows several notable behavioral characteristics.Pattern Observation Assessment Small route test0.1 ETH sent and returnedConsistent with route validationDisposable EOAsFour intermediaries became active on the day they were usedConsistent with single-purpose routing infrastructureProgressive scaling110 ETH mixed before a later 1,260 ETH batchConsistent with testing before larger deploymentFixed denominations12 × 100 ETH and 6 × 10 ETH depositsConsistent with denomination-based mixer structuringBalance cleanupResidual ETH returned upstreamSuggests temporary wallets were cleaned after routingShort wallet lifespanIntermediaries showed only a small number of outgoing transactionsConsistent with operational compartmentalizationThe pattern is more structured than simply forwarding stolen ETH directly into a mixer.The sequence suggests an operator using temporary addresses, validating routes, scaling transaction size, and cleaning residual balances after use.This is a behavioral assessment. It does not, by itself, identify the operator.9. Address Poisoning Was Removed From the GraphDuring transaction review, ChainBounty identified 32 transactions consistent with address-poisoning activity.These transactions involved addresses deliberately resembling wallets in the investigation, often sharing similar starting and ending characters.Some also transferred fake assets named similarly to ETH rather than native ETH.Poisoning SummaryImitation address Target address Events Economic relevance 0x922a86...6cd230x922adc...8cd231Fake ETH-, no native ETH0xa31bb2...138e30xa31bb1...c38e313Fake ETH-, no native ETH0x6495e2...972c30x6495af...272c32Fake ETH-0xadb80c...1c5780xadb82e...2c5787Fake ETH-0x8db9cb...ec3060x8dB9D7...0C3067Zero-value native transfers0x5664cf...c09fc0x56644f...d09fc2Fake ETH-Total32ExcludedThese transactions were excluded because they showed no meaningful economic value flow and matched common address-poisoning characteristics.Including them would create false graph edges and potentially corrupt attribution.This is an important reminder that transaction-history proximity is not equivalent to financial linkage.10. No Exchange Cash-Out Was IdentifiedWithin the investigated outbound Ethereum flow:Destination category Confirmed deposits Centralized exchanges0Tornado Cash Router20 transactions / 1,370 ETH grossPublic reporting referenced Kraken and ChangeHero in connection with activity involving the consolidation wallet.Those references concerned claimed inbound flows into the wallet, rather than confirmed cash-out destinations in the outbound path analyzed here.ChainBounty therefore does not identify Kraken or ChangeHero as laundering destinations based on the present evidence.11. What the Ethereum Transactions Suggest About the Initial CompromiseThe initial ETH and USDT withdrawals were ordinary signed transactions.Observation Implication ETH moved via a standard native transferNo obvious Ethereum contract exploit in the transaction itselfUSDT moved through a standard token transferConsistent with valid signing authority being usedETH and USDT transfers occurred 36 seconds apartIndicates coordinated executionPublic reporting describes multiple chains affected in a narrow time windowBroader signing or withdrawal infrastructure compromise is plausibleThe available evidence is therefore more consistent with compromise of withdrawal signing authority than with a vulnerability in an Ethereum smart contract.Possible mechanisms could include exposure of private keys or compromise of infrastructure authorized to sign withdrawals.The blockchain cannot determine which mechanism occurred.That question requires off-chain evidence such as key-management records, signing-service logs, server telemetry, access logs, or other internal forensic material.12. The Most Interesting Unresolved AddressOne address differs significantly from the disposable infrastructure surrounding the incident:0x4293b5dc11b250078da7359d7d57c15eecfcf70aCharacteristic Observation First activityJanuary 5, 2018Activity lifespanMore than eight yearsOutgoing transactions380Interaction with initial receiverYesInteraction with consolidation walletYesAttributionUnknownThere are two materially different explanations.Hypothesis Investigative significance Operator-controlled gas or funding infrastructureCould expose older transactions, KYC-linked services, or reused infrastructureBridge solver, relayer, or other shared serviceMay have little or no attribution valueCurrent evidence cannot distinguish between them.The wallet should therefore be treated as a high-priority lead rather than evidence of attacker ownership.13. Remaining Investigative OpportunitiesPriority Investigative target Why it matters 10x4293...Could connect short-lived incident wallets to long-lived infrastructure20x8dB9... balanceFuture transfers may reach a bridge, exchange, or additional mixer3593,430.319285 USDT pathUSDT may remain technically freezeable depending on downstream disposition40xA77e... → 0x8dB9... gapClosing this gap would strengthen end-to-end provenance5Tornado Cash exitsPotential exit candidates can be evaluated against later exchange deposits6Non-Ethereum chainsSolana, BNB Chain, Bitcoin, and Tron remain outside this Ethereum-focused investigationAt the investigation snapshot, the two monitored wallets held:Wallet Balance 0x8dB9D7...0C306973.536981 ETH0xA77e24...aef7625.566884 ETHThe original 593,430.319285 USDT transfer also remains a significant unresolved asset path.If USDT remains in token form at an identifiable downstream address, issuer-level intervention may still be relevant.14. Fund-Flow Timeline15. ChainBounty AssessDate Event Amount Sep. 24Duelbits-labeled wallet → 0xA77e...593,430.319285 USDTSep. 24Duelbits-labeled wallet → 0xA77e...836 ETHSep. 24Consolidation wallet route test0.1 ETHSep. 26Consolidation wallet → first intermediary12 ETHSep. 26Consolidation wallet → first intermediary650 ETHSep. 26–27First intermediary → consolidation wallet539.9 ETH returnedSep. 26–27First laundering branch → Tornado Cash110 ETHSep. 28Consolidation wallet → second intermediary1,252 ETHSep. 28Second intermediary → final intermediary1,250 ETHSep. 28Final intermediary → Tornado Cash1,260 ETH gross15. ChainBounty AssessmentThe Ethereum evidence supports a clear downstream laundering pattern:short-lived EOAs → staged routing → fixed-denomination mixer deposits → residual-balance cleanup.It also supports a confirmed initial withdrawal of 836 ETH and 593,430.319285 USDT from a Duelbits-attributed wallet.What the evidence does not yet support is equally important.The value path between the first receiving wallet 0xA77e... and the reported consolidation wallet 0x8dB9... remains unanchored.And while downstream wallets deposited 1,370 ETH into Tornado Cash, the transaction-level incident path explains up to 1,360 ETH, not necessarily the full amount.That is the line ChainBounty draws between observation and attribution.ConclusionThe Ethereum portion of the Duelbits incident shows a structured laundering operation built around temporary wallets and Tornado Cash.A Duelbits-labeled hot wallet transferred 836 ETH and 593,430.319285 USDT to a newly activated address on September 24.Separately, ETH leaving the publicly reported consolidation wallet can be followed through four short-lived intermediary EOAs into the Tornado Cash Router.Those wallets deposited:Metric Amount Gross Tornado Cash deposits1,370 ETHNumber of deposits20Maximum explained by tracked incident path1,360 ETHConfirmed exchange cash-out0The distinction between 1,370 ETH observed and 1,360 ETH attributable is not a technicality.It is the difference between describing what appeared in a wallet's transaction history and demonstrating where investigated value actually came from.The investigation also remains incomplete at a critical point: the first recipient and the reported consolidation wallet have shared counterparties, but the value path connecting them has not yet been transaction-anchored.For that reason, ChainBounty does not present the case as a fully closed end-to-end flow.The next breakthroughs are more likely to come from closing that missing link, tracing the USDT path, analyzing the long-lived 0x4293... address, and monitoring the remaining ETH for interaction with identifiable services.Because in on-chain investigations, the goal is not to draw the cleanest graph.It is to know exactly which edges can be proven.Investigation MetadataField Value Case IDCASE-7907CC26NetworkEthereum — Chain ID 1Incident dateSeptember 24, 2026Investigation windowAugust 23 – September 28, 2026Gross Tornado deposits observed1,370 ETHIncident-path attributionUp to 1,360 ETHExchange deposits identified0This report is based on observable on-chain transaction data and address-attribution information available during the investigation. Statements describing behavior, intent, compromise mechanism, or operator infrastructure are analytical assessments unless explicitly identified as transaction-level facts.
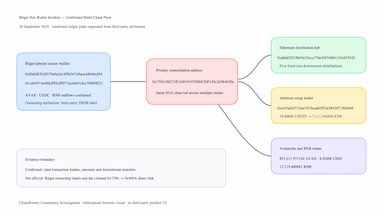
Executive SummaryBitget confirmed unauthorized transfers from hot wallets at 18:31 UTC on 24 September 2026. The exchange stated that cold wallets were not affected and that its protection fund exceeded $464 million. Public reporting placed the loss at approximately $351.6 million.SentinelTX expanded the investigation to 289 addresses and 41 evidence items across Ethereum, Arbitrum, Avalanche and BNB Chain. The pattern is consistent with a hot-wallet signing or key compromise: one consolidation EOA appeared across chains, stablecoins were rapidly swapped into ETH, funds crossed bridges, and Ethereum proceeds were split into fixed-size tranches.The clearest recovery lead is 20,763,612.55 USDC routed from Avalanche and Arbitrum through a common receiver into a Circle-labeled address. No centralized-exchange deposit or mixer exposure was confirmed in the reviewed scope.Incident AnchorsItemValueStatusEvidenceOfficial confirmation24 Sep 2026, 18:31 UTCConfirmedBitget statementPublic loss estimate$351.6MReportedCEO / mediaSentinelTX scope289 addresses; 41 evidence itemsConfirmedCase outputCEX or mixer exposureNone confirmedOpenReviewed scopeCore Wallet MatrixRoleAddressChainEvidencePrimary consolidation0x770b10b273fC44Fe9197D6bF20F145c2e98463EeMulti-chainHighUSDT0-to-ETH swap0xe410a2e5710ee787bcaa63f52a3943ff71f0d946ArbitrumHighStablecoin receiver0xb3fa262d0fb521cc93be83d87b322b8a23daf3f0Arbitrum / AvalancheHighCircle-labeled route0xfd78ee919681417d192449715b2594ab58f5d002Multi-chainHigh label; destination openEthereum source0x469Ac1406dE92f82C0563477240a3627057425DCEthereumHighEthereum hub0xa6dd3f218b65e32ccc37be30f74884133c655545EthereumHigh inbound; mixed outflowAvalanche downstream0x5085b3d52b5587c18ef456fcbcde9a11d48340f8AvalancheHighBNB downstream0x7c96279ec1e888aa56b9b836e0db26ca48573e1cBNB ChainHighWhat the Cross-Chain Flow ShowsThe primary consolidation address was active on Ethereum as early as 7 February 2026, contradicting descriptions of it as newly created. TRDB labels on two upstream addresses are useful leads, but do not independently prove Bitget ownership.Confirmed Chain-Level MovementsChainConfirmed movementActionConfidenceEthereum1,541.51 ETHSource to distribution hubHighArbitrum19,668,851.77 USDT0 → 7,111.344304 ETHSwap and splitHighAvalanche821,000 AVAX + 8,204,678.8 USDCTwo downstream routesHighBNB Chain12,719.45 BNBRouter-linked downstreamHigh; partial pathArbitrum: Swap, Split and Partial Stablecoin RecoveryOn Arbitrum, 19,668,851.77 USDT0 reached a dedicated swap wallet and was converted through UniswapX and 1inch intents into 7,111.344304 ETH. One branch converted 2,513 ETH into 6,561,140.178933 USDC; another 26,830.363654 USDC joined the same receiver before the route reached a Circle-labeled address.Key TransactionsChainTransactionMovementStatusEthereum0xbb7f4d68c339f44e048b45bcee466bc75a086fc02d89cda8242b5031639bf8b41,541.51 ETH → hubIncident-anchoredEthereum0x872dd53e25e071ae7ae6b653a44ff18cfc041e8fdea4ac0da72c6ef97ba4ede110,000 ETHGross hub outflow onlyEthereum0xd955a11839263c24e49ddb850b17663d0122904cee1fb9c436e04203a88ec28810,000 ETHGross hub outflow onlyEthereum: Anchored Inflow vs. Gross Hub ActivityA confirmed transaction moved 1,541.51 ETH from the Ethereum source to the hub. The hub later sent several much larger tranches. Those gross outflows cannot all be attributed to this incident because only the 1,541.51 ETH inbound is directly anchored to the investigated path.Bridges, Routers and Recovery LeadsInteraction with a router or bridge does not mean that service controlled the attacker.PriorityAddress / serviceObserved amountAction10xfd78ee919681417d192449715b2594ab58f5d002 / Circle20,763,612.55 USDCPreserve and freeze route20xe35e9842fceaca96570b734083f4a58e8f7c5f2a / Across1,600 ETHTrace destinations30xef4fb24ad0916217251f553c0596f8edc630eb66 / deBridge1.001213 ETHPreserve destination tx40x2bca667d37afe8d065ca46e3261e9442e77cbeae~1,997 ETH residualMonitor and trace50x5085b3d52b5587c18ef456fcbcde9a11d48340f8~620,999.99991 AVAXMonitor and traceWhat Remains UnprovenNo threat actor has been identified. No evidence confirms a CEX deposit or mixer. The direct link from the multi-chain consolidation address to 0x469Ac1406dE92f82C0563477240a3627057425DC was not independently confirmed; it remains a third-party Bubblemaps claim. Zero-value and tiny lookalike transfers were excluded as address-poisoning noise.Untraced RemainderChainUnresolved amount / pathNext stepEthereumMuch of 34.75M USDT/USDC; hub downstreamSeparate incident funds from prior activityArbitrum~1,997 ETH + ~990 ETH; Across destinationsTrace destination chainsAvalanche~620,999.99991 AVAX; router outputResolve router recipientsBNB Chain~9,719.45 BNBTrace beyond shared routersConclusionThe evidence confirms coordinated cross-chain dispersal and a high-priority Circle recovery route, while leaving substantial balances and several bridge destinations unresolved. The urgent action is preservation and freeze outreach for the Circle-labeled path, followed by destination tracing for Across and deBridge.Evidence note: wallet balances and labels reflect the SentinelTX investigation cutoff. Public statements, third-party labels and analytical inference are separated from transaction-confirmed facts.
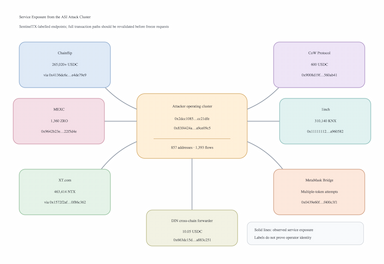
EXECUTIVE SUMMARYBetween 19 and 20 September 2026, a linked attacker cluster abused privileged signing and minting authority across the Artificial Superintelligence Alliance ecosystem. Public incident analysis attributes the initial loss to a compromised SingularityNET bridge-authorizer key and a separately compromised NuNet minting key—not to a flaw in Ethereum consensus or a normal user-wallet compromise.The most concrete liquid loss was 8,721,530.40162591 FET released from Fetch.ai's Ethereum conversion infrastructure. Unauthorized supplies of AGIX, NTX, WMTx and CGV were also created, but their face value must not be treated as realized proceeds: liquidity was too shallow to sell the entire counterfeit supply at quoted prices.SentinelTX expanded three seeds into 857 addresses and 1,393 flows. Its case summary connected the two main attacker addresses through a shared gas funder, identified several exchange and bridge exposures, and showed that the primary wallet still held 433.045913 ETH at the initial profiling cutoff. The result establishes a broad operational cluster, but it does not identify the human operator.HOW THE PRIVILEGED-ACCESS FAILURE WORKEDThe incident combined two different privileged actions. First, a valid-looking authorization was used against Fetch.ai's TokenConversionManagerV3 to release existing FET. Separately, compromised mint authority created unauthorized token supplies directly from the zero address. The contracts executed the permissions they were given; the security failure was control of the privileged signing and minting keys.The diagram below separates the liquid FET withdrawal from the later token mints. That distinction matters because drained reserve assets and newly created, illiquid supply have different economic effects.CONFIRMED SEEDS AND INCIDENT ANCHORSItemAddress / transactionType / valueTime / blockEvidence notePrimary attacker0x2dcc1085fdcf418b421e45e86e4e54637cc21dfe433.045913 ETH; 192 outbound txProfiling cutoffSentinelTX seed walletSecond attacker0x83f4424a401a9bb75f90314f21adaea6a9ce09c5Smart contractFirst active 20 SepShared-funder cluster linkFetch.ai converter0xab424a430cc09864fa1277a38193111705adf3a3Verified contractPublic incident anchorContract role verifiedFET withdrawal0xfe12c63b322d52727c615f3342222138d1563400a9880cebb516a9a162ac69e28,721,530.40162591 FETIncident withdrawalPublic transaction anchorEarliest preview tx0x17627865473286a01045f485b664274123e59c48bc3e65cbab6347264b49843bPreview transactionBlock 25,885,213Low-confidence “Poloniex Hack” endpoint leadPublic on-chain research reports 408.53 million NTX, 260 million AGIX and 53.838 million WMTx minted without authorization. Those quantities describe counterfeit supply, not cash successfully realized by the attacker.ONE OPERATING CLUSTER, NOT ISOLATED ADDRESSESSentinelTX found a common funding wallet, 0xa7a31d206042b8a3e81aa4cf8c68c1b76856ee48, that supplied ETH to both main attacker addresses. It sent 0.5776 ETH to the primary wallet. Two additional wallets—0x1572f2af7696b39c85e3221cde8efb640f86c362 and 0x3196fd46b8e44a48722d0e8d042dbf28ad2ea1f9—also supplied ETH or NTX to the primary wallet.This shared infrastructure is consistent with common control, but funding overlap is not proof of a real-world identity. The defensible conclusion is that the addresses operated as one coordinated on-chain cluster during the incident window.WHERE THE MONEY TOUCHED SERVICESSentinelTX's conversational case summary identified the following service exposures. They are useful intervention leads, but the free report preview does not disclose every full transaction hash or every hop. Each recipient and label should therefore be revalidated before a legal freeze request is sent.Secondary routing endpoints remain relevant but are not treated as final cash-out:Service / routeAddressObserved activityClassificationCoW Protocol0x9008d19f58aabd9ed0d60971565aa8510560ab41600 USDCRouting endpointMetaMask Bridge0x0439e60f02a8900a951603950d8d4527f400c3f1Multiple-token attemptsBridge endpointDIN cross-chain forwarder0x663dc15d3c1ac63ff12e45ab68fea3f0a883c25110.05 USDCForwarding endpointThe report preview also displayed a low-confidence endpoint labelled “Poloniex Hack” receiving 860.69 USDT, 1.20 million FakeAI and another token. Because the attribution confidence is low and the full path is locked behind the detailed report, it should be treated as an investigative lead—not a confirmed exchange cash-out.WHAT THE CHAIN PROVES—AND WHAT IT DOES NOTThe available evidence supports five conclusions:1. Existing FET left the converter through a transaction anchored to the primary attacker wallet.2. Large unauthorized token supplies were minted through privileged contract roles.3. The two principal attacker addresses shared funding infrastructure.4. The cluster interacted with labelled exchange, swap and bridge endpoints.5. The primary wallet retained a substantial ETH balance at the profiling cutoff.The evidence does not prove who stole the keys, whether every downstream wallet is controlled by the same person, or how much of the counterfeit supply was actually monetized. It also does not justify adding unsold token face values to liquid losses.One inconsistency remains open. SentinelTX's conversational summary described the Fetch.ai converter as receiving and holding the same 8.721 million FET, while independent call-level reporting describes the contract releasing that amount to the attacker. The transaction trace should control; the “holding wallet” wording should not be repeated without reconciling the contract call and token-transfer direction.INVESTIGATOR PRIORITIESThe first priority is preservation and freeze outreach to Chainflip, MEXC and XT.com using complete transaction paths—not abbreviated addresses. CoW, 1inch and bridge interactions should be preserved as routing evidence even when they are not final cash-out points.The second priority is key-control reconstruction: bridge authorizer rotation, NuNet minter-role changes, deployer access logs, CI/CD secrets, cloud audit logs and acknowledgement timestamps. The shared funder should be examined for earlier deposits from labelled exchanges or infrastructure providers.The third priority is live monitoring. The primary attacker wallet remained active through 21 September, and SentinelTX's report preview is based on Ethereum data through block 26,016,578 with the last transaction on 22 September. Any movement after that cutoff is a new evidentiary event.CONCLUSIONThis incident was not one token contract failing in isolation. A privileged-access compromise crossed multiple connected projects and turned trusted bridge and minting functions into attacker tools. The chain provides a strong operational cluster and several intervention points, while still leaving identity and final realized proceeds unresolved.The clearest public claim is therefore narrow: compromised privileged keys enabled one material FET withdrawal and several unauthorized token mints; the attacker cluster shared funding infrastructure; and part of the liquid proceeds reached labelled services where preservation and KYC requests may still matter.SOURCES AND METHODOLOGY• SentinelTX case CASE-C5F23B38, investigated 23 September 2026. Graph: 857 addresses, 1,393 flows. Preview evidence: 429 of 882 addresses shown; on-chain cutoff block 26,016,578.• Bitquery Research, “SingularityNET Hack Explained: AGIX, FET and NTX Minted,” 20 September 2026: https://bitquery.io/investigations/asi-bridge-counterfeit-supply• Smart Contracts Hacking, incident record: https://smartcontractshacking.com/hacks/asi-alliance-singularitynet-hack-2026• SingularityNET bridge documentation: https://dev.singularitynet.io/docs/products/Bridge/faq/Service labels come from SentinelTX's threat-reputation and exchange attribution data. Labels indicate an investigative lead; they do not by themselves establish ownership, intent or legal liability.SERVICE EXPOSURE APPENDIXThe four highest-priority intervention leads are organized below using the community editor’s native table. Labels are investigative leads and must be revalidated against complete transaction paths.EndpointObserved exposureRoute / contractConfidenceInvestigator actionChainflip265,020+ USDC0x4136dc6c18e2bcdb559145476f413318e4de79e9High-priority leadRevalidate tx path; freeze outreachMEXC1,360 ZRO0x9642b23ed1e01df1092b92641051881a322f5d4eMediumPreservation and KYC requestXT.com463,414 NTX0x1572f2af7696b39c85e3221cde8efb640f86c362High-priority leadRevalidate complete route1inch310,140 KNX0x1111111254eeb25477b68fb85ed929f73a960582Routing onlyPreserve swap evidenceINCIDENT ANCHOR TABLECore wallets and transaction anchors are separated from service exposure so investigators can copy complete identifiers without mixing them with attribution labels.ItemAddress / transactionAmount / activityEvidence statusInvestigator notePrimary attacker0x2dcc1085fdcf418b421e45e86e4e54637cc21dfe433.045913 ETHSentinelTX seed192 outbound txSecond attacker0x83f4424a401a9bb75f90314f21adaea6a9ce09c5First active 20 SepSmart contractShared funder linkFetch.ai converter0xab424a430cc09864fa1277a38193111705adf3a3Verified contractPublic anchorReconcile transfer directionFET withdrawal0xfe12c63b322d52727c615f3342222138d1563400a9880cebb516a9a162ac69e28,721,530.40162591 FETPublic tx anchorExisting FET releaseCLUSTER FUNDING AND ATTRIBUTION TABLEFunding overlap supports a coordinated on-chain cluster, but it does not identify the real-world operator.RoleAddress / transactionAsset / amountConnectionConfidenceShared gas funder0xa7a31d206042b8a3e81aa4cf8c68c1b76856ee480.5776 ETH to primaryFunded both main attackersStrong cluster leadAdditional funder A0x1572f2af7696b39c85e3221cde8efb640f86c362ETH / NTX fundingPrimary wallet and XT.com routeObserved linkAdditional funder B0x3196fd46b8e44a48722d0e8d042dbf28ad2ea1f9ETH / NTX fundingPrimary walletObserved linkEarliest preview tx0x17627865473286a01045f485b664274123e59c48bc3e65cbab6347264b49843b860.69 USDT + 1.20M FakeAILow-confidence endpoint labelInvestigate only
An unsafe `uint128` cast on Ethereum. Funds in Tornado Cash before most of the market was awake. Recovery is still open.On 3–4 September 2026, residual balances sitting in Notional Finance’s long-deprecated V1 escrow were drained in a single transaction. The loss was 1,658,525 USDC and 69,257 DAI, about $1.73 million at the time. Current V2 / V3 / Exponent products were not in scope. The team published a post-mortem on 8 September. No funds have been recovered.That last sentence is why this case is on ChainBounty.V1 was publicly deprecated in January 2022. Withdrawals were left live so remaining users could exit. Four years later the escrow at `0x9abd0b8868546105F6F48298eaDC1D9c82f7f683` still held real USDC and DAI. That is the inventory an attacker actually needs: a forgotten contract, a live withdraw path, and a balance large enough to bother with.What brokeThis was not a flash loan, not an oracle, and not a stolen key.Two `mintfCashPair()` calls created payer liabilities of `1` and `2^256 − 1`. Combined, the payer’s liability evaluated to −2^128. Free-collateral valuation in `ExchangeRate._convertToETH()` then applied a raw `uint128()` cast instead of `SafeCast.toUint128()`. On Solidity 0.6.x that overflowed to 0. The collateral check passed. The attacker minted an unbacked fCash claim equal to the live escrow balances, settled it, and withdrew.The whole sequence fit in two transactions, three minutes apart: Hash Time (UTC) Block Setup0xe1589a19…25d60a3 Sep 2026, 23:58:4725,900,220Drain0xc3f3e318f7ab2d0daaba59e6ec901d25d1fe8a89aafe2b2b62e3b9aee1a24efa4 Sep 2026, 00:01:3525,900,234Pause0x012fc554b165b3b3ccf3121018ae26503cab50031fa84adea29253b1cd5831d9shortly after—The drain was submitted as a private bundle through Titan, with a 0.07 ETH builder tip. Public mempool never got a look.Where the money wentAttacker main: `0xDaCC235a494750193695A111D715c2ca12b5Ce38`. First on-chain activity for that wallet is 3 September 2026, 21:41:35 UTC — about two hours twenty minutes before setup. No prior history. No existing labels.First-hop DAI receiver: `0x265ccfF3673bCAb03867988081cd51bFd919C03C`.Same day, the stables were swapped to roughly 689.2 ETH. From `00:15:59 UTC` on 4 September, that ETH was dropped into Tornado Cash in a 100 / 10 / 1 / 0.1 ladder — 25 deposits, total 689.2 ETH, all from `0xc95496c917a41a394efdac3e0882f5903d24de69` into the sanctioned Tornado router `0xd90e2f925da726b50c4ed8d0fb90ad053324f31b`.Fourteen minutes from drain to mixer.One tracing detail worth flagging before anyone copies an abbreviated address into a freeze letter: two wallets share the same four-character prefix and suffix.- `0xc95496c917a41a394efdac3e0882f5903d24de69` — Tornado deposit source (25 txs)- `0xc9541b387b55c88aa6962480432b185373b5de69` — received 689.21258215375 ETH; outbound from this wallet was not established in the first outbound passWrite both in full. Do not collapse them to `0xC954…De69`.The only non-mixer service endpoint that showed up in the traced residual dust is CCE.Cash treasury (`0x0361897d757d13a4afad64a2e1bc561b96a8c7cf`) for 0.011222 ETH. No CEX deposit address appeared in the outbound graph. That is a null result, not a gap to invent around: inside the current hop window there is nothing to freeze at an exchange.The graph below is the outbound trace from the origin wallet through five hops. Seed is the attacker EOA. Terminal is Tornado plus the CCE.Cash dust.Status on that pass: 12 of 13 addresses, 11 of 12 flows, cashed-out 1.11 ETH (~$3K) visible on the highlighted path, in-flight 1.66M USDC + 69.3K DAI (~$1.7M) sitting behind the mixer wall.Why this is still an open caseNotional’s post-mortem is public. The recovery surface is not closed.Three facts keep it live:1. Mixer withdrawals after 4 September have not been fully mapped. 689.2 ETH went in on a structured ladder. The only practical freeze window is the moment a withdrawal hits a KYC venue.2. The attacker cluster is purpose-built. Main EOA, exploit contract (`0xec434a2f9b7b93aad1bed77d6bc512a75ae90d78`, 0.07 ETH tip receiver, first seen 3 Sep / last active 4 Sep), relay `0x8aaf01b6f9acc973274b8718be4d1c1be10e3be6`, and both `0xc954…de69` wallets are unlabeled and appear for this job only. That is operational hygiene, not amateur hour.3. The primitive is being copied. SlowMist flagged two actors on BSC staging the same fCash overflow and waiting on position maturity. Cited contract: `0x0795E2cd771788572b61BeA45Abd6E9a8FC8D9F0`. Whether those positions matured, were paused, or paid out has not been confirmed on-chain in this file. That check is time-sensitive. After maturity it becomes another recovery problem. Before maturity it is still a stop.What we want from investigatorsP0- Rebuild the exact call trace on setup + drain. Publish the overflow math as a one-pager.- Map every ETH hop into Tornado and watch withdrawals after 4 September against the 100 / 10 / 1 / 0.1 pattern.P1- Cluster `0xDaCC…Ce38`, both `0xc954…de69` wallets, and the Titan private-order flow against prior exploits. Outbound-only work so far did not produce a prior-job link. That is also a result — inbound gas funding on the attacker EOA is the better identity lead.- Full BSC replica file: transactions, maturity timestamps, pause status, whether any payout cleared.P2- Inventory other live 0.6.x forks of Notional V1 / similar fCash escrow that still hold balances.- Deliverable: freeze memo on standby (no CEX dust in the current window), Tornado withdrawal watchlist, and a “deprecated-but-funded” contract list.The part that should bother protocol teamsDeprecated does not mean empty. A contract that nobody monitors, compiled on 0.6.x, with a raw integer cast that the same file already replaced with `SafeCast` in other places, is not a historical footnote. It is an unattended vault.The operator who hit this one already knew that. They picked the leftover escrow, submitted privately, converted freezable stables to ETH the same day, and structured the mixer deposits to the denomination set. If they built an inventory of V1-style fCash escrows, Notional was unlikely to be the only name on it.If you are tracing withdrawals, sitting on a BSC confirmation, or holding a labeled counterpart we missed — file it.Key references- Notional post-mortem: https://blog.notional.finance/notional-v1-exploit-post-mortem/- Drain tx: https://etherscan.io/tx/0xc3f3e318f7ab2d0daaba59e6ec901d25d1fe8a89aafe2b2b62e3b9aee1a24efa- Escrow: `0x9abd0b8868546105F6F48298eaDC1D9c82f7f683`- Attacker: `0xDaCC235a494750193695A111D715c2ca12b5Ce38`
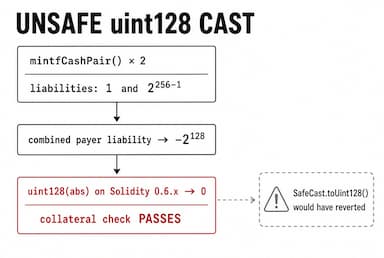
EXECUTIVE SUMMARYAt 04:38:47 UTC on 15 September 2026, an Ethereum transaction removed approximately 2,900 aEthrsETH from Safe wallet 0x40E93a52F6Af9fCD3b476aeDADD7FeABD9f7AbA8, withdrew the underlying rsETH from Aave, and split the proceeds. A generalized MEV searcher known as Yoink executed first, ahead of the party that prepared the exploit path.The largest portion, 2,882.37 rsETH, went to 0xC70f00CD7E461686b04B0E912E309becA8b80ea0. Another 17.63 rsETH was sold for approximately 18.95 ETH. Kelp publicly described a temporary 24-hour address-level pause and said rsETH remained fully backed and its core contracts were unaffected.The chain evidence supports a narrower technical conclusion than several early headlines. The failure was not a Safe core bug, a stolen owner key, or a bypass of signature verification inside Safe. The Safe had already delegated execution power to modules. A publicly callable batch executor treated a self-target as trusted, allowing an outsider to walk through an enabled gateway and liquidity module into Safe module execution without a fresh owner signature.ATTACK PATH AND EVIDENCE BOUNDARYThe main extraction transaction is 0x0e7680b06cb8a6f86c149d9ba90d98e3d334e7b072dde03909d43fcfd98a8705 in Ethereum block 25,980,525. Bitquery reports 175 successful calls, a maximum call depth of 24, and 39 logs.The caller path was public executor batch(self), gateway module, Safe module execution, delegate-call execution, and the enabled Uniswap v4 liquidity module. The Safe processed those module calls as designed. The authorization weakness sat in the public batch contract's target validation and in the amount of authority reachable behind that check.The extraction used a newly created junk token, PAT, as the other side of an aEthrsETH pool. Public discussions initially described a malicious Uniswap hook. Bitquery's call-level reconstruction says the pool's hook field was the zero address and the flow used a normal Pool Manager unlock and take sequence. Until contract-level evidence establishes otherwise, “malicious hook” should be treated as an early characterization rather than a confirmed mechanism.CONFIRMED TRANSACTION ANCHORSThe primary victim Safe is 0x40E93a52F6Af9fCD3b476aeDADD7FeABD9f7AbA8. The reported attacker EOA is 0x0dC2c5D6b05A317076CF501f7E7be36A5dfe9b66, the helper contract is 0x10605eE48Ff962952C966277A5D2dac0A0705Cb1, and the public keeper multicall is 0x4f0055926c839d1d960a82cbf84e2ee933958ebc.The Yoink EOA, 0xFDe0d1575Ed8E06FBf36256bcdfA1F359281455A, called the Yoink bot contract at 0x80BF7Db69556D9521c03461978B8fC731DBBD4e4. The extraction burned roughly 2,900 aEthrsETH and produced the underlying rsETH. The bot parked 2,882.37 rsETH at 0xC70f00CD7E461686b04B0E912E309becA8b80ea0 and sold the remaining 17.63 rsETH through a real ETH/rsETH market.THE 24-SECOND RACEAt 04:38:23 UTC, the helper deployed PAT and an unlocker and minted a large PAT supply. At 04:38:35, it seeded the Uniswap v4 pool. Twelve seconds later, the Yoink transaction landed at index zero in block 25,980,525. The original attacker's transaction does not appear in that block.Within the capture transaction, the module path moved aEthrsETH from the Safe into Pool Manager, the unlocker took the aToken, and the helper withdrew the underlying rsETH from Aave. Yoink then split the proceeds between the large receiving wallet and an in-block sale.The distinction between “front-running the attacker” and “recovering the victim's funds” matters. Yoink prevented the original exploiter from receiving the primary payout, but public chain data does not establish that the receiving wallet belongs to a white hat or that the funds were returned. Address behavior alone cannot identify the operator or its intent.FOLLOW-ON FLOWS AND CURRENT EXPOSUREBitquery reports no rsETH outflow from the 2,882.37 rsETH receiving wallet at its investigation cutoff. That supports a dormant-balance finding, not an independent proof of Kelp's off-chain restriction mechanism. Kelp's public statement described a temporary pause; Bitquery did not identify an on-chain admin pause transaction.The same morning produced several additional flows. At 05:24:47, a copycat extraction moved 50 aEthrsETH through the same PAT pattern; 40 rsETH entered CoW in four transfers and 10 rsETH moved to another address. At 05:47:59, the same reported attacker path hit a second Safe, 0x6a1fac6b3466e29421f70d6eaa91a0de0f627ea2, moving 86,632 DUSD and 38,248 USDC and producing approximately 23.69 ETH for the attacker EOA.At 05:53:59, Yoink used a Morpho Blue WETH flash loan and Aave's liquidation function against the first Safe. Aave events recorded about 168.83 WETH of debt covered and 157.71 rsETH seized. The seized rsETH was sold on Fluid before the flash loan was repaid.At 06:00, the owner disabled the gateway and liquidity modules used by the drain. At 06:37, the same sender repaid 248 WETH of Aave debt. At 07:20, an owner transaction disabled nine additional modules. The containment sequence therefore followed the exploit and several copycat attempts rather than preventing the first extraction.WHAT REMAINED ON THE SAFEThe wallet was not emptied. Bitquery's post-incident snapshot reported approximately 50,279 aEthrsETH, 51,344 variable-debt WETH tokens, 7.18 native rsETH, and 18 Uniswap v4 position NFTs, including the empty PAT position. These balances are a point-in-time public-chain observation and can change.WHAT THE CHAIN PROVES — AND WHAT IT DOES NOTConfirmed by transaction-level public-chain analysis:• The primary extraction occurred in block 25,980,525 through an enabled module path without a fresh Safe owner signature.• Roughly 2,900 aEthrsETH was converted to rsETH; 2,882.37 rsETH was parked at one receiver and 17.63 rsETH was sold.• The pool used for PAT had a zero hook address in Bitquery's reconstruction.• Later activity included copycat drains, a second Safe loss, an Aave liquidation funded through Morpho, and module disable transactions.• The largest rsETH balance had no observed rsETH outflow at the published cutoff.Not established by the available evidence:• The real-world identity or intent of the attacker, Yoink operator, or receiving wallet controller.• Whether the 2,882.37 rsETH will be returned, retained as a bounty, or released after the reported pause.• Whether an off-chain restriction can be mapped to a specific on-chain admin transaction.• A complete victim-loss figure that reconciles the initial drain, copycats, the second Safe, debt repayment, and later liquidations.CONCLUSIONThis incident is a warning about delegated authority rather than multisig cryptography. Safe's owner threshold was never asked to approve the transfer because the relevant modules already possessed a route to execute for the wallet. The control that failed was the caller boundary in front of those modules.The MEV outcome reduced the original attacker's take but did not automatically restore the victim. Investigators should keep the 2,882.37 rsETH receiver, the ETH skim wallets, the CoW route, the Fluid sale, and the second-Safe proceeds under observation. The next material update will be a return transaction, a release from the reported restriction, or a transfer into a labeled service.METHODOLOGY AND SOURCESThis report uses Bitquery's published call-level reconstruction and public Ethereum transaction references, cross-checked against Blockaid's initial alert, Kelp's incident statement, and contemporary reporting. A new SentinelTX investigation was not executed because the account had no remaining monthly investigation slot; this report therefore does not claim SentinelTX verification.Bitquery, “How a Safe module drained 2,900 rsETH in one block”: https://bitquery.io/investigations/rseth-safe-module-drainBlockaid incident alert: https://x.com/blockaid_/status/2099732957803999342Kelp incident response: https://x.com/KelpDAO/status/2099740756865159562Primary transaction: https://etherscan.io/tx/0x0e7680b06cb8a6f86c149d9ba90d98e3d334e7b072dde03909d43fcfd98a8705Unchained, “A Bot Robbed the Hacker Who Drained $7.8 Million in rsETH From a Safe Wallet”: https://unchainedcrypto.com/a-bot-robbed-the-hacker-who-drained-7-8-million-in-rseth-from-a-safe-wallet/
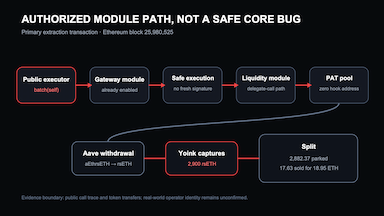
EXECUTIVE SUMMARYOn 6 September 2026, the Liquid Network suffered a validation failure that allowed unbacked L-BTC to be created and exchanged for Bitcoin held by the federation. Blockstream's incident status said approximately 4,000 BTC was withdrawn through SideSwap's Peg-out Authorization Key path while the key itself was not compromised. Public reporting later described a software validation and caching flaw rather than a signer compromise.SentinelTX reconstructed the Bitcoin mainnet leg. It confirmed 3,996.01834922 BTC leaving the federation peg wallet, passing through one relay address, and consolidating as 3,995.99999857 BTC in the attacker wallet. On 7 September, that wallet returned 3,400 BTC. At the investigation cutoff of 12 September 2026 at 23:36 UTC, 598.50136349 BTC remained in the same attacker address.The most important result is a null result: five-hop outbound tracing found no confirmed exchange deposit, mixer exposure, CoinJoin pattern, bridge route, or other cash-out leg for the remaining balance. The retained Bitcoin was visible and dormant rather than dispersed. This leaves a live recovery and enforcement window, but it does not identify the operator.INCIDENT MECHANICS AND EVIDENCE BOUNDARYLiquid's normal peg is intended to keep L-BTC backed one-for-one by Bitcoin held by the federation. The incident broke that backing invariant. The exploit did not require movement of federation signing keys; instead, an invalid asset state was accepted by the peg-out path and released real BTC.The diagram below shows only the Bitcoin mainnet path independently anchored by SentinelTX. Liquid-side issuance details, the precise vulnerable code path, and the disclosure timeline remain dependent on public technical reporting until a complete postmortem is published.CONFIRMED TRANSACTION ANCHORSThe first anchor is transaction 8db751a650ae2f12006b7e8c69a75e4df360e8afd6b9e05ae0b9fa6458a7b140. It moved 3,996.01834922 BTC from federation peg wallet bc1qdlld6antmv4xug242ed83q7k4rqw50cwfns38szx4qu2f4jwaxxsuhwxxr to relay address bc1qgslsydz56d0ed6827hdemfmk5w2f6ldyc6wt7p.Transaction 85d2ca15bea33a592e73ed40c6a5da887feecf1e77f58ec7f580e00841645043 then moved 3,995.99999857 BTC from that relay to attacker wallet bc1ql4mfu6aundtkksxklfajs2h3t9nzcd6gyqjlte. On 7 September, transaction a6d697a25266ce3c78774fd1d75f896b7af522ada209b0f6228ea497bc49a46d returned 3,400 BTC to the federation peg wallet.The evidence ledger below separates confirmed transfers from one unresolved accounting gap. The attacker wallet's observed balance exceeds the simple anchored inflow-minus-return calculation by approximately 1.96304 BTC. That difference may reflect additional inflows, but it must not be assigned to the exploit without transaction-level reconciliation.CURRENT STATUS OF THE REMAINING 598.5 BTCSentinelTX traced outbound activity from the attacker wallet across a 60-day window and up to five hops. The only material outbound transaction was the 3,400 BTC return. The remaining 598.50136349 BTC showed no confirmed split, peel chain, CoinJoin, mixer deposit, bridge transfer, or centralized-exchange deposit.The attacker address and federation peg address were both unlabeled in SentinelTX's internal entity database. Calling the latter the federation wallet relies on public incident materials and transaction context, not an independent database label. This distinction matters because address behavior can confirm a flow without proving real-world ownership.WHAT THE CHAIN PROVES — AND WHAT IT DOES NOTThe chain proves the withdrawal path, the relay hop, the final consolidation address, the 3,400 BTC return, and the retained balance at the stated cutoff. It also shows that the remaining balance had not entered a known off-ramp or obfuscation service during the observed window.The chain does not prove that the operator was a good-faith security researcher. Public messages reportedly used white-hat language, but retaining user backing as leverage after partial return fits a coercive, self-appointed bounty pattern. That is an analytical classification, not a legal finding or identity attribution.Likewise, public claims that a security warning was ignored remain disputed. Bitcoin Red Team co-lead Calle said the parties had agreed to an embargo and accused Blockstream of publishing an incomplete account early. Blockstream-linked voices denied that warnings were ignored. SentinelTX did not independently obtain a complete disclosure record, acknowledgement timestamps, severity triage, patch history, or embargo terms. Until those artifacts are published, the ignored-warning narrative should be treated as an allegation.INVESTIGATOR PRIORITIESThe clearest intervention opportunity is the first movement from bc1ql4mfu6aundtkksxklfajs2h3t9nzcd6gyqjlte. Exchanges and major service providers can prepare alerts against the confirmed address before a deposit appears. No freeze target exists yet because no exchange deposit leg was observed.The strongest attribution lead on the public chain is the relay address bc1qgslsydz56d0ed6827hdemfmk5w2f6ldyc6wt7p and its pre-incident history, co-spend relationships, and counterparties. Two shared outputs in the initial federation transaction—bc1qk3cvk5599nydy8zwavlxaduke54pgf4vl0ckru and bc1qkxwva32eh7mgezq5kladncd3n5wtcjmslh98my—also warrant service-attribution review.The unresolved 1.96304 BTC balance gap should be reconciled before the accounting chain is called complete. Off-chain evidence is equally important: SideSwap request records, account details, IP logs, authentication traces, and federation communications should be preserved.CONCLUSIONThe Liquid exploit is unusual not because the proceeds disappeared quickly, but because most were returned and the remainder stayed visible. At the cutoff, 598.50136349 BTC remained concentrated in one public address with no confirmed laundering or cash-out leg. That creates leverage for recovery negotiations, real-time monitoring, and coordinated exchange response.The restraint visible on-chain should not be mistaken for authorization or attribution. The defensible conclusion is narrower: a software validation failure released federation BTC; a single attacker cluster returned 3,400 BTC; the remaining balance was dormant; and the next transaction may be the first actionable off-ramp signal.SOURCESBlockstream Service Status, "Liquid Security Incident," 7 September 2026: https://status.blockstream.com/Chainalysis, "How The $320M Exploit of Liquid Network Went Down," 9 September 2026: https://www.chainalysis.com/blog/320m-exploit-liquid-network/SideSwap, "Statement on the Liquid Network incident of 6 September 2026": https://testnet.sideswap.io/news/statement-on-the-liquid-network-incident-of-6-september-2026/The Block, "Return the bitcoin: Blockstream refuses ransom demand for remaining 600 BTC from Liquid exploit," 11 September 2026: https://www.theblock.co/news/ecosystems/2026-09-11-return-the-bitcoin-blockstream-refuses-ransom-demand-for-remaining-600-btc-from-liquid-exploit-414247SentinelTX on-chain investigation completed 13 September 2026. All balances and endpoint observations are time-bound. Wallet association does not by itself identify a person or organization.
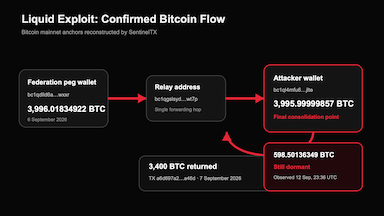
EXECUTIVE SUMMARYOn 28 August 2026, an outdated Solana collateral program used by Rain-powered stablecoin card products was reportedly exploited through a reused Ed25519 verification proof. Blockaid reports roughly $1.1 million drained across multiple programs, followed by swaps into SOL, a bridge to Ethereum, and approximately 455.9 ETH deposited into Tornado Cash.Our SentinelTX investigation reached a narrower, transaction-anchored conclusion. It independently confirmed two USDC inflows totaling 1,780.973441 USDC into the reported Solana collection wallet on the incident date and confirmed the published Ethereum router as a sanctioned Tornado Cash endpoint. It did not reproduce the reported $1.1 million total, the deBridge leg, or the 455.9 ETH deposit from the supplied seeds. Those gaps are central findings, not details to hide.INCIDENT MECHANICSAccording to Blockaid, the vulnerable contract accepted one attacker-controlled Ed25519 proof where two independent authorizations were expected. That enabled AddCollateralAdmin, followed by repeated WithdrawCollateralAsset calls across user collateral accounts. The failure was in shared card-balance infrastructure—not in users’ private keys.The diagram below separates the authorization failure from the later asset movement.VERIFICATION MATRIXClaimStatusEvidence~$1.1M lossReportedBlockaid / press2,945 admin + 5,288 withdrawalsReportedBlockaid1,780.973441 USDC on Aug 28Confirmed2 Solana txsdeBridge + 455.9 ETH to mixerUnanchoredNo matching path from seedsTornado router identityConfirmedSentinel labelClaim | Status | EvidenceReported loss of about $1.1M | Reported, not independently reproduced | Blockaid and press reporting2,945 AddCollateralAdmin and 5,288 WithdrawCollateralAsset calls | Reported, not independently reproduced | Blockaid1,780.973441 USDC received by the reported collection wallet on 28 August | Confirmed | Two Solana transaction anchorsdeBridge route and 455.9 ETH into Tornado Cash | Reported, not anchored in this session | No matching bridge or mixer transaction from supplied seedsTornado Cash router identity | Confirmed | Sentinel Protocol labelCONFIRMED SOLANA TRANSACTION ANCHORSThe reported collection wallet is FVNFzqAny8spWdPmYw6RQ9TkYa29ueFFiqCFD1gQnCEj. SentinelTX found two incident-date inflows:• 1,779.973441 USDC from HEgJutJjfCyG7RDtcS9xBc8sbty31TsqK3VCxyh4s7K1 in transaction 2oE6hQ7nFYpx9k1EUZuy93DsPqDUoo6MvSzMG8b8zGMZ7hUbzAzuYubicvRPK7Pcyvsxb1Hk35yB22dsC9jt3M5L.• 1.000000 USDC from 83v8iPyZihDEjDdY8RdZddyZNyUtXngz69Lgo9Kt5d6d in transaction JV6xqGB4Xppfre5rYvSauypAxZGG3quqtR19utqsQTmot4BPSr8KoqPRUZWfhZ6rDC9SkH45Lu4gcU34pyeKudv.No outbound movement from the collection wallet was observed in the 60-day window. Both counterparties were unlabeled. This means the supplied collection wallet explains only a small fraction of the reported loss and does not itself prove the subsequent swap, bridge, or mixer path.REPORTED FUND FLOW AND EVIDENCE BOUNDARYBlockaid describes a route from drained USDC and USDT through Solana DEX swaps into SOL, across deBridge to Ethereum, and finally into Tornado Cash. The diagram below shows that reported path while marking the mixer as the deterministic endpoint boundary.WHAT THE EVM SEEDS DO—AND DO NOT—PROVEThe supplied address 0xa1a15f1b0d4878873f2933573e4385ab1e4df25c had no relevant value-flow connection to the Solana incident in the observed window and retained only about $4.39. The second seed, 0x775028b2ce02844e8947905e4d655940a76cf559, had an active multi-exchange history, but SentinelTX found no taint-traceable path from the Rain exploit. Service contacts visible around that address—including Binance, Bybit, MEXC, FixedFloat, Cryptomus, Bitpanda and CoinEx—must not be presented as destinations of Rain proceeds without that missing link.The Tornado Cash router 0xd90e2f925DA726b50C4Ed8D0Fb90Ad053324F31b is independently labeled as a sanctioned mixer. The identity of the service is confirmed; the claimed 455.9 ETH incident deposit is not confirmed by this investigation.WAS THE ENTIRE WALLET TRAIL TRACED?No. Deterministic tracing stops at the supplied seeds because the collection wallet showed no outbound transaction in the observed window and neither EVM seed could be connected to the verified Solana inflows. The three strongest next steps are: obtain the full AddCollateralAdmin and WithdrawCollateralAsset transaction sets for all four matching deployments; trace upstream from HEgJutJjfCyG7RDtcS9xBc8sbty31TsqK3VCxyh4s7K1; and identify the reported 455.9 ETH Tornado Cash deposit cluster before tracing backward to a bridge arrival.CONCLUSIONThe most defensible conclusion is narrower than the headline. A shared, outdated authorization design reportedly widened one exploit across multiple card programs. SentinelTX confirmed two incident-date inflows and the mixer router’s identity, but it did not close the chain from those Solana inflows to the reported cross-chain laundering path. The gap between $1.1 million reported and 1,780.973441 USDC independently anchored points to missing wallet sets or incomplete public seeds.That distinction matters: a labeled exchange contact is not automatically incident proceeds, and a published mixer address is not proof of a specific deposit. The next investigation should begin from the deployment-level withdrawal transactions, not from assumptions about the supplied EVM wallets.SOURCESBlockaid, “$1.1M Rain Ecosystem Exploit: How Onchain Monitoring Gives Stablecoin Card Issuers Fleet-Level Coverage” (2 September 2026): https://blockaid.io/blog/11m-rain-ecosystem-exploit-how-onchain-monitoring-gives-stablecoin-card-issuers-fleet-level-coverageSentinelTX case CASE-ASYNCBE3, investigated 4 September 2026.APPENDIX — EVIDENCE STATUS TABLE
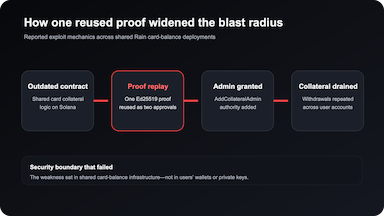
 조사관 신청하기