Defend Against Cybercrime with the Power of Community
Many victims have already taken action through ChainBounty. Report now and join the effort to stop online crime


Quick AI Scam Check
Help protect others by sharing your scam experience
이오영 면상까고 남들정보 팔아가며 찍은사진
[국제발신] 이오영 면#상#까고#남#들 정#보팔#아가며 #찍#은사진#궁#금한사#람 01079378010 #연#락하#면공#개
코인 주식 리딩방 초대
🏆 HANSUNG INVESTMENT GROUP 📈 국내 주식 & BTC 단기 전략 무료 공개 시장에는 언제나 기회가 있지만, 중요한 것은 언제 진입하고 어떻게 대응하느냐입니다. HANSUNG INVESTMENT GROUP은 국내 주식과 BTC 단기 전략 트레이딩을 기반으로 실시간 시장 분석과 단체 트레이딩을 운영하고 있습니다. 무료 공개를 통해 실제 운영 방식과 전문가의 전략을 직접 확인해 보시기 바랍니다. 🔗 무료 입장 링크 https://t.me/+YzI2zf5yamhmZDJk ━━━━━━━━━━━━━━ 📌 무료 공개 내용 ✅ 국내 주식 실시간 전략 ✅ BTC 단기 전략 ✅ 실시간 시장 브리핑 ✅ 전문가 대응 전략 ✅ 단체 트레이딩 운영 방식 ━━━━━━━━━━━━━━ 🎁 정회원 전용 혜택 ✅ 국내 주식 트레이딩 ✅ BTC 단기 전략 트레이딩 ✅ 실시간 시장 브리핑 ✅ 1:1 맞춤 투자 전략 컨설팅 ✅ 원금보장 프로그램 운영 (적용 대상 별도 안내) ━━━━━━━━━━━━━━ 📅 단체 트레이딩 운영 일정 🕘 09:00 ~ 11:30 │ 오전 국내 주식 트레이딩 ☕️ 11:30 ~ 13:00 │ 휴식 및 시장 모니터링 🕐 13:00 ~ 13:30 │ 오후 국내 주식 트레이딩 ₿ 14:00 ~ 14:30 │ BTC 단체 트레이딩 1부 ₿ 15:00 ~ 15:30 │ BTC 단체 트레이딩 2부 ₿ 16:00 ~ 16:30 │ BTC 단체 트레이딩 3부 ₿ 17:00 ~ 17:30 │ BTC 단체 트레이딩 4부 ₿ 18:00 ~ 18:30 │ BTC 단체 트레이딩 5부 ━━━━━━━━━━━━━━ 💬 운영 방식을 직접 확인하신 후 참여 여부를 결정하셔도 됩니다. 부담 없이 입장하셔서 실시간 리딩을 직접 경험해 보세요.
Contribute by sharing insights to strengthen the community

On 24 October 2026, X100’s Ethereum Freezer contract executed a sequence of governance proposals that moved treasury assets and withdrew liquidity. The crucial question is how addresses that acquired voting weight could use it immediately. The checked receipts show two supporting votes out of three Senate seats, followed by execution within the same transaction. The displayed source explains why that sequence was possible.This report follows three execution transactions, then a narrower onward route from the first USDT recipient through two conversions and one ETH distribution address. It separates the transaction sender, the contract doing the work and the address receiving the proceeds. Those roles are not proof of a person’s identity. E1, E2, E3.1. Before the numbers: what each participant didThe Freezer is the asset-holding governance contract. In the reviewed source, “frozen” tokens are tokens counted as stake for Senate membership; freezing here does not mean a stablecoin issuer or law-enforcement agency blocked an address. A helper contract is an address used during execution to hold stake and cast a vote. A bundler submits transactions for other operations; its presence does not identify the ultimate beneficiary.RoleEthereum addressFreezer: governance and treasury0x79F35A33FE2813414851c4Ae8daeacD14d822A46X token; 6 decimals0x100A2C7F45Fd48e217fdcE72e658dc78Fd43A100USDT token; 6 decimals0xdAC17F958D2ee523a2206206994597C13D831ec7First sender and final USDT recipient0x7ec2afdF3eC5964899894f8D58afa95cbB8FfD63Second transaction sender; explorer labels it ERC-4337 Bundler0xfc3fAcD67138966aB0c841E905B0C4BCA1AbE92FSecond final recipient0xEDac2D8905bF2Bf0033872D420C4ec6ef1dDd0c8Third transaction sender0xDAB137F390dF77caA97fd492540E973fd5e2F8c8Third final recipient0x0A67804462F04B0be1c433fB1C2F7fb76e5166F2Blockaid and Chainalysis supplied the public incident framing and transaction leads. The tables below use independently opened explorer records for movement and event facts. Their public estimates of roughly $4.7 million and roughly 4.85 million USDT are source snapshots, not interchangeable accounting totals. Public statement 1; Public statement 2; Public statement 3; Public statement 4; Public statement 5.2. Scope and the three findingsQuestionChecked scopeChain and event dateEthereum mainnet; 24 October 2026 UTCExecution window14:11:47–14:40:47 UTC; three selected receiptsOnward-route cutoffFour selected 400 ETH transfers through 14:43:59 UTCMethodPublic explorer receipt/log review and displayed exact-match verified source; not an independent node replayAccounting boundary4,848,017.339222 USDT paid to three selected recipients; not a whole-incident loss estimateReview date25 October 2026 KST; historical transactions, not a current-balance snapshotFirst, the governance boundary did not require the proposal to wait until its expiry: the first checked receipt creates, votes on and executes proposal 7 in one transaction. Second, the later executions use the same two newly observed helper addresses as senators, even though transaction senders and execution contracts differ. Third, the first recipient’s USDT payment is exactly matched by two subsequent USDT spends, while the ETH relay receives slightly more ETH than those two conversions produced. That difference prevents an all-funds provenance claim.3. How voting weight became an immediate treasury instructionWhat turned stake into execution permission? In the first receipt, each of two helper addresses receives 19,100.000001 X. Each sends 19,000.000001 X into the Freezer and a further 100 X as a candidacy fee. Frozen, Registered and Ranked events precede proposal creation. This ties the explanation to the actual receipt rather than assuming that any large holder could control the contract. E1.First execution evidenceObserved recordHelper holding stake and voting0xe08107E7Dc7c4540D139392e9D0FEA99ca019F37Second helper holding stake and voting0x176D1eA0ee9569783C6f6E455f7Be6171566619cProposal 7Selector 0xa4376352; v3Swap in the displayed permitted-method sourceVotes at execution2 votes for / 3 Senate seats; ProposalExecuted log 37Treasury leg400,000 X sent to the newly created pool; 35.675313 USDT received on the reverse legPool for that leg0x9A03c41c539880b51508bEbbc2Dde7B738f6f075Read Figure 1 from top to bottom. Arrows show the order of events within the first transaction, not an extra transfer of money. The observation to carry forward is that stake acquisition, voting and treasury execution happen together. The next question is which source checks permit that timing.Figure 1. Event sequence in E1. This is a governance sequence, not an asset-value chart. Full helper addresses and the transaction are in the adjacent table and evidence appendix.In Senate.sol, propose records the proposer’s supporting vote immediately. vote checks current Senate membership. execute tallies the current ranked list and accepts support when support × 2 is greater than senateSize. _state leaves a proposal open until it expires; expiry is a deadline, not a compulsory delay. execute then calls the permitted proposal data on the contract itself. DexTreasury.sol permits v3Swap and v3Decrease and forwards those operations to its module. Freezer.sol obtains voting stake from frozenOf. Displayed verified contract source.This source path and the receipt agree on the narrow failure mode: voting weight could be acquired and used immediately for treasury operations. The reviewed first proposal passes zero as its minimum output parameter; its observed 400,000 X leg receives only 35.675313 USDT. The later swap output elsewhere in the receipt is a different leg, not the treasury’s sale proceeds. We have not independently replayed historical storage, compiled the bytecode or audited every module path, so this is not a comprehensive code audit.4. Three executions do not establish three independent peopleAt 14:35:59 UTC, the second transaction executes proposals 8–13, including five liquidity-decrease instructions and one swap. The receipt creates a different execution contract and two helpers. It ultimately pays 96,381.883491 USDT and 9,894.892631 X to its final recipient. The sender is the bundler-labelled address, not that recipient. At 14:40:47 UTC, the third execution uses the same two helper senators seen in the second receipt, and pays a different recipient. This is a direct operational link, but does not resolve who controlled those addresses. E2; E3.ExecutionVerified final recipient paymentE1 · 14:11:47 UTC4,749,726.096973 USDTE2 · 14:35:59 UTC96,381.883491 USDT + 9,894.892631 XE3 · 14:40:47 UTC1,909.358758 USDT + 549,915.546932 XSelected USDT subtotal4,848,017.339222 USDT; no conversion of X to USDThe first USDT amount is the final transfer to the sender after the observed flash-loan repayment, not the larger gross swap output. An Aave FlashLoan event records a 1,942,457.637245 USDT principal and 971.228819 USDT premium in E1. The gross 6,693,089.638357 USDT swap output must therefore not be called net profit or added to the final payment. Likewise, repeated transfers between execution contracts and recipients are the same funds moving through a route. Native ETH gas is outside this USDT subtotal.Governance executionsReceipt evidenceE1 · proposal 72 / 3; execution log 37E2 · proposals 8–132 / 3 each; execution logs 484, 496, 508, 520, 532, 542E3 · proposals 14–172 / 3 each; execution logs 18, 28, 38, 59Raw final-payment checksE1 log 54: 4749726096973 USDT units; E2 log 554: 96381883491; E3 log 71: 1909358758Raw X check in E3Log 66: 549915546932 units; 6 decimal placesThese are selected recipient payments, not an independently reconciled loss across all treasury assets and all transactions. X-token residuals, changing pool prices and any other incident-linked activity remain outside that conclusion. The first explorer receipt is successful but also displays an internal reverted-call warning; “Success” does not mean every internal attempt succeeded.5. Following the first recipient into ETHWhere did the first USDT payment go? Two later transactions show the first recipient spending 2,000,000 USDT and 2,749,726.096973 USDT through a UniswapX settlement route. Their sum exactly matches the 4,749,726.096973 USDT received in E1. Internal native-asset transfers pay 851.542914929444388864 ETH and 1,170.472889392738131465 ETH back to that recipient. The transaction senders are settlement participants, not automatically the beneficial owner. S1; S2.RecordAmount and meaningS1 · 14:16:35 UTC2,000,000 USDT out; 851.542914929444388864 ETH inS2 · 14:17:47 UTC2,749,726.096973 USDT out; 1,170.472889392738131465 ETH inTwo conversion receipts2,022.015804322182520329 ETH received in totalR1 + R2 · 14:18:59 / 14:19:23 UTC2,022.856704743507502222 ETH sent onwardDifference0.840900421324981893 ETH more sent onward than these two conversions producedThe first recipient then sends 1,000 ETH and 1,022.856704743507502222 ETH to the same distribution address. Because that total exceeds the two conversion receipts, it cannot all be assigned exclusively to those conversions. Other ETH already present or received can mix with converted proceeds. This review proves the selected transfer sequence, not a unique per-wei attribution. R1; R2.Read Figure 2 from the first recipient to the central distribution address, then outward to four branches. Solid arrows are checked native ETH transfers. The top panel reports the separate conversion total and the mixing boundary. The four equal branch transfers are the key observation; their later disposition is the next unanswered question.Figure 2. Historical ETH transfers on 24 October 2026 UTC. Labels use evidence IDs and rounded ETH values for readability; exact quantities and full identifiers are preserved below. No current balances or common ownership are asserted.Distribution roleFull Ethereum addressCentral distribution address0x8296721489d0a7E934edd66ea27159B1C88A42e5D1 · 400 ETH · 14:39:47 UTC0xF637DCeE7Dd96E8FDaB926C5993D558B52D635eaD2 · 400 ETH · 14:40:35 UTC0x6790cF09ba33D05aDA2C13cBB4104F5b8B666391D3 · 400 ETH · 14:43:35 UTC0x64b135Af3d80733c9C290D58873e2CCcb34a81AeD4 · 400 ETH · 14:43:59 UTC0x4fDB9F9A44b356c8A9c2Ea060a40Fb7a9cAaBef3Each of D1–D4 is a successful 400 ETH transfer from the central address, for a selected distribution total of 1,600 ETH. The second and third execution transactions overlap this distribution window; the chronology is not three isolated phases. No outbound activity from the four recipients was exhaustively reviewed. Their historical receipts do not prove that they still hold 400 ETH each, that an exchange accepted them, or that anyone cashed out.6. What the evidence does not establishA shared helper pair links the second and third governance receipts, but shared infrastructure alone does not prove one operator, and different senders do not prove different people. No personal identity is established here. Explorer service labels are navigation clues, not legal findings. There is no verified recovery, asset freeze or exchange account attribution in this bounded review.The source displayed at the Freezer address is exact-match verified, and its creation receipt predates these transactions: 23 October 2026 at 14:25:59 UTC, block 26255911. That does not substitute for a complete historical-state or implementation-change analysis. The reviewed code and the selected emitted events support the immediate-governance path; unreviewed configuration changes and module branches remain limitations. Contract creation receipt.7. Incident-specific response pointsThe governance evidence points to a concrete control question: can newly acquired, currently ranked stake authorize treasury DEX operations before other holders have time to respond? A meaningful remediation review would need to test delayed execution, a prior-state voting snapshot and limits on treasury price execution against this exact same-transaction sequence. This report does not claim that any of those changes have been deployed.For tracing, preserve E1’s recipient payment, the two USDT settlement records and R1/R2 as one route rather than counting each hop as new loss. Preserve D1–D4 as separate historical outputs, with their exact hashes, before making a service-exposure claim. The outstanding recovery question is what happened beyond those four outputs; this review does not answer it.8. Evidence appendix8.1 Selected transaction inventoryAll times below are explorer-displayed UTC on 24 October 2026. Full hashes are deliberately retained. E1’s internal reverted-call warning is a qualified success; the other selected transaction detail pages display Success.Evidence E1RecordTransaction0x38c60844f1923d53fdce7d99e9bc2a2d8c73a08e793341dfbb479f8cc74d81d0UTC / block2026-10-24T14:11:47Z / 26263022Observed factFirst execution; final payment 4,749,726.096973 USDTStatusSuccess; explorer also shows an internal reverted-call warningEvidence S1RecordTransaction0xb861b3710531230449711b04b416cc65ccff87e6dab0457e373e5dbb637e5dd5UTC / block2026-10-24T14:16:35Z / 26263046Observed fact2,000,000 USDT out; 851.542914929444388864 ETH received by first recipientStatusSuccessEvidence S2RecordTransaction0xb25ae55fded129da667ba5375d23fc1c611167e5444b0d20751e86b51668accdUTC / block2026-10-24T14:17:47Z / 26263052Observed fact2,749,726.096973 USDT out; 1,170.472889392738131465 ETH received by first recipientStatusSuccessEvidence R1RecordTransaction0x9a3f04912e1e52ad04fc00ac72efb3169e4a4c73596d1a5d7c055375397cc0dcUTC / block2026-10-24T14:18:59Z / 26263058Observed factFirst recipient → distribution address; 1,000 ETHStatusSuccessEvidence R2RecordTransaction0x3a8908f55e86af180559aed1051f9acc6145dad5e3292ffa48582f5b8bb9e1f2UTC / block2026-10-24T14:19:23Z / 26263060Observed factFirst recipient → distribution address; 1,022.856704743507502222 ETHStatusSuccessEvidence E2RecordTransaction0x77c46e1aa9037ed4fbc9cc7e00d199dcd752acf576b4b5d3446e785dc45235c0UTC / block2026-10-24T14:35:59Z / 26263143Observed factSecond execution; final payments 96,381.883491 USDT and 9,894.892631 XStatusSuccessEvidence D1RecordTransaction0xa08147bbd6cd279678327faf43af3e7f96323aed376f5bdbe44ed9fbef2898e5UTC / block2026-10-24T14:39:47Z / 26263162Observed factDistribution address → branch 1; 400 ETHStatusSuccessEvidence D2RecordTransaction0x5954deb30f637cd2d789403dce8a03caa9a89f2c088f7963976927948804953eUTC / block2026-10-24T14:40:35Z / 26263166Observed factDistribution address → branch 2; 400 ETHStatusSuccessEvidence E3RecordTransaction0x7c49bf28865defd5c1345f6527210360d635e510fa49279d0b62e6e02cfad99aUTC / block2026-10-24T14:40:47Z / 26263167Observed factThird execution; final payments 1,909.358758 USDT and 549,915.546932 XStatusSuccessEvidence D3RecordTransaction0x09c7e5feac1a466c67f9b6816bf82f8f2f16297acfe282e7592b0dbd749366bfUTC / block2026-10-24T14:43:35Z / 26263181Observed factDistribution address → branch 3; 400 ETHStatusSuccessEvidence D4RecordTransaction0x8f2bfb1391244540283d009e05dcd49988452d0ea456a7edba4dd331394cbbd9UTC / block2026-10-24T14:43:59Z / 26263183Observed factDistribution address → branch 4; 400 ETHStatusSuccess8.2 Execution and voting address registerRoleFull Ethereum addressE1 outer contract0x89e903e4512F8a315ceBD99c29a1e40EeE6Fe2C9E1 execution contract0x37541Fc4A6F1eC86889bA506F51DC39f2BeDd10AE2 execution contract0x515Ca27BB80325cdc56f0ad3B9dE69829C869A51E3 execution contract0x554B49369E0e612bC56088E355D3a087006e0C64Helper senator in E2 and E30xC2f69b21BeA8F0C64cbd4597f262C80c993073BASecond helper senator in E2 and E30xb21F45868DCAAe3bE7c842971Ae61DD93D4C7CdEOther seat in checked event lists0xA13a935dce629FbbA304D3EbdA8d96459B05716E8.3 Source and evidence boundariesFreezer verified-source viewer: reviewed functions are listed in the code discussion above. X token metadata and USDT token metadata each display 6 decimals. Public analyst statements establish attribution and reported context; selected explorer receipts establish transfers and events. Arithmetic subtotals are calculations over that stated scope. Ownership, full loss, current holdings and recovery remain unverified.
Four token payouts, a sequence of conversions and one short relay define the Ethereum trail associated with the reported WAX Multi-Chain Bridge incident of 22 October 2026. SentinelTX’s case report follows that trail to an address labelled “HitBTC, Exchange”. The destination is an investigative lead, not proof of a completed cash-out or the identity of the person controlling the funds.This analysis focuses on the Ethereum transfers documented in SentinelTX report CASE-ASYNC3FA, compiled on 24 October 2026 UTC. It distinguishes recorded movements from venue labels and incident-level assessments. Amounts remain in their native asset units; no incident-wide dollar loss is calculated here.Four payouts in less than a minuteThe report records four transfers from the same Ethereum contract to the same recipient between 10:05:35 and 10:06:11 UTC on 22 October. The assets and quantities were:21,558.252354 USDT at 10:05:35 UTC.840.2750339 DAI at 10:05:47 UTC.2.54669928 WETH at 10:05:59 UTC.0.10993227 WBTC at 10:06:11 UTC.Address key: payout contract 0x24b22b031ae1b5a6b09f9a0fd33613a40e0d70e6; recipient 0x01664e199991b2f3fe412c2de5b9b7a0dcdc5070. Token symbols follow the report’s trace labels and are not a separate token-identity verification.Figure 1. Four Ethereum payout quantities, shown separately because the units differ. Source: SentinelTX CASE-ASYNC3FA, pp. 4–5 and 17. These are transfer amounts, not a total loss calculation.The contract’s role as the bridge’s release side is an assessment in the report, not a returned address label. Similarly, the recipient’s alleged attacker-side role depends on the broader incident interpretation. A transaction trail establishes movements between addresses; by itself it does not establish the identity or authority of the signer.From token balances to an ETH relayThe report’s chronology describes token-conversion activity after the payouts. It records two unsuccessful USDT swap attempts before a successful KyberSwap route at 10:16:11 UTC. The WBTC movement followed at 10:18:35, then WETH at 10:20:23 and DAI at 10:22:23. The WETH and DAI routes are attributed to Velora; the WBTC interaction is with an unlabelled contract.These swap venues should not be confused with the eventual exchange-labelled destination. They are intermediate interactions in the account’s conversion sequence, not evidence that the exchange received each original token.At 10:24:23 UTC, the recipient transferred 15.58 ETH to 0x62907e044ffe22a24aa8794ff2a6ea20598227bb. At 10:43:47 UTC, that relay sent 15.5799958 ETH to 0x80787af194c33b74a811f5e5c549316269d7ee1a, which the report labels “HitBTC, Exchange”. The report displays the second amount rounded to 15.579996 ETH in its chronology and summary.Figure 2. The Ethereum sequence described in the report: token payouts, conversion activity, an ETH relay and an exchange-labelled destination. The 15.579996 ETH endpoint figure is rounded. The report does not itemise each swap’s ETH output, so the full conversion-to-deposit attribution remains a partial path, rather than an exact per-token reconciliation.Flow address key: A = 0x01664e199991b2f3fe412c2de5b9b7a0dcdc5070; B = 0x62907e044ffe22a24aa8794ff2a6ea20598227bb; C = 0x80787af194c33b74a811f5e5c549316269d7ee1a (HitBTC label as returned).The distinction matters. The two ETH transfers are recorded movements. The interpretation that the 15.58 ETH combined the four swap proceeds with a small pre-existing gas balance is the report’s assessment. It does not support treating every wei of that transfer as independently reconciled proceeds of the incident.What the destination does, and does not, establishThe report describes the relay as a single-use pass-through within the inspected ETH record. Its onward transfer gives investigators a concrete transaction to present to the service associated with the destination label. It does not reveal a customer account, establish the wallet type, or demonstrate a fiat withdrawal.The destination label is therefore a route for further inquiry, not an allegation that HitBTC participated in the incident. The report’s recommended next step is preservation and lawful review of any relevant credited-account, access and onward-withdrawal records. Whether funds remain available, whether the label maps to a particular account and whether recovery is possible require information beyond this public transfer trail.The reported bridge mechanism remains a separate questionSentinelTX cites third-party reporting of a negative-fee input-validation issue in WAX’s eth.token withdrawal mechanism. In that reported model, a negative max_fee could offset the requested quantity while a full withdrawal was still recorded. The report does not include WAX-chain action records that independently establish the mechanism or map individual source-chain withdrawals to these Ethereum payouts.Its narrative also describes a Solana USDC branch. That is context for the reported multi-chain incident, not a basis for treating this Ethereum-focused analysis as a complete cross-chain reconstruction. No value transfer linking the Ethereum and Solana recipients is established in the report, and common control is presented as an inference rather than an on-chain connection.Accordingly, this article does not combine the branches into a loss total, identify an operator, claim that all affected funds have been located, or describe the underlying WAX mechanism as independently confirmed. The report itself leaves onward Solana movement unresolved.The evidence that would strengthen the caseSource-chain linkage: WAX withdrawal actions, quantities, fee arguments and transaction identifiers matched to destination-chain payouts.Conversion reconciliation: executed ETH outputs for each token swap, kept separate from gas funding and residual balances.Destination attribution: confirmation of the exchange-labelled address’s role and any relevant account records obtained through appropriate channels.Earlier infrastructure: the origin of the ETH used to fund the recipient’s initial gas, without assuming that funding alone proves common ownership.Figure 3. The report supports a specific Ethereum transfer trail. Operator identity, source-chain linkage, exact per-swap reconciliation and any completed cash-out remain separate evidentiary questions. Source: SentinelTX CASE-ASYNC3FA, pp. 8–16 and 17–18.Conclusion: a useful endpoint, not the end of the investigationThe clearest result is narrow and actionable: four recorded Ethereum token payouts were followed by conversion activity, a 15.58 ETH relay transfer and an onward transfer displayed as 15.579996 ETH to a HitBTC-labelled address. The amounts, timing and transaction anchors make that trail more useful than a headline loss estimate.The remaining work is to connect that trail to the source-chain actions and, where legally available, the account-level records behind the labelled destination. Keeping those questions separate preserves the difference between following funds and identifying who controlled them.Transaction anchorsUSDT payout: 0x7c6e4bf4efff995981b8b0f7fa1434cc85063e95c0f7460c71277e0a3f9c14d0DAI payout: 0x58960a7afccf78725e8bcfcf7c1f38cac9e08f2a556da81ec7ee1c5023fc79c6WETH payout: 0x9a55cd6c9e9067ac2bf8d33dff233a3e3dd3739c56206444b8a5e79daabb4ff5WBTC payout: 0x6e1553e7d932d8019f59ea6a3bd09c3071b41d538975686cf3f7e785f9e6716015.58 ETH to the relay: 0xd3f4c1c672eb8c3cdbc00216b0215fc72a16bc659a2e48b8a90241b4f165fe80Relay to the HitBTC-labelled address: 0x64c65d0296fbe983c365646eb5bbb788d6cdd21b2bc54c365e296aef26c885acSource note: Adapted from the SentinelTX platform-generated report “Investigation report CASE-ASYNC3FA”, compiled 24 October 2026 UTC. This article is an attributed analysis of that report, not an independently reproduced investigation. Explorer links use transaction hashes cited in the report; they are not proof of address ownership or the broader incident interpretation.
Source: SentinelTX analysis.SentinelTX’s analysis records 726,307.1011248019 BSC-USD paid to the exploit-signing address, followed by a bridge route and Ethereum settlement activity. The reported loss, mechanism, and final ETH balance require different levels of qualification.This ChainBounty review draws on SentinelTX’s analysis of case CASE-20261024-NEM1. Recorded transfers, reported figures, and analytical assessments are distinguished throughout.The recorded proceeds and reported lossThe investigation concerns a BNB Smart Chain token called NEM, identified in the analysis as token contract 0x9cf0e3ad4efa7ab602d7b5a38c55795cfa777777. The name NemTokenV2 comes from press reporting cited by SentinelTX. The analysis establishes no connection to the separate NEM/Symbol blockchain project.Its central finding is a transaction dated October 21, 2026, at 03:28:50 UTC, in BSC block 128,866,147. The signing address, 0xfd929b0f270dfea6c4827262b4e2bf6ea50fe9b6, called an attack contract, 0x5e6d1f40be466dd2facc94a26818948ecd3b1ca2. SentinelTX classifies the resulting payment of 726,307.1011248019 BSC-USD to the signing address as confirmed. The full transaction hash and address register appear in the appendix.The widely reported loss of approximately US$821,920 is a separate source claim. It is not interchangeable with the recorded payment of 726,307.1011248019 BSC-USD. SentinelTX does not establish a complete reconciliation between the reported loss and the recorded proceeds, so neither figure should be substituted for the other.The analysis distinguishes the October 21 execution date from the October 22 alert and publication date. Its October 24 ETH balance observation is later still. These dates describe different events, not competing dates for one transaction.From preparation to the Ethereum exitAll transaction times below are UTC on October 21, 2026, as stated in the source analysis.01:00:17: The address described as the funder sent the signing address its first recorded gas funding, 0.007 BNB. The analysis flags this amount as unverified and requiring corroboration.01:28:16–03:27:26: Sixteen NEM transfers from the funder supplied approximately 767,818.31 NEM, also an unverified amount. A second gas top-up is recorded as 0.01 BNB. Six helper-creation records span 01:32:22–03:14:31.03:28:30: The signing address transferred 767,811.3061168424 NEM to the attack contract. The transfer is recorded, but its quantity is explicitly unverified.03:28:50: The exploit transaction executed. The analysis reports 1,608 receipt logs and approximately 473 million BSC-USD in transaction-level movement across several counterparties. That gross movement is not presented as the loss or the attacker's proceeds.03:38:38: The recorded 726,307.1011248019 BSC-USD payment was forwarded through a router labeled Socket OpenRouter. SentinelTX correlates a Relay bridge record to this source transaction.03:39:11: A sender labeled Relay.link delivered 725,384.763364 USDT to the same address on Ethereum. The analysis classifies the route as confirmed through the correlated bridge record and destination transfer, while marking the destination amount unverified.03:46:11–03:47:47: Three USDT legs went to a contract labeled CoW Protocol settlement. Their quantities are unverified.The analysis’s later balance read is dated October 24. It records approximately 296.19 ETH remaining at the signing address on Ethereum, with no outbound ETH in the retrieved ledger. This is an unverified historical balance observation, not a claim about the address's live balance when this article is read.The assessed mechanism: a skim-and-burn loopSentinelTX assesses the incident as a token-accounting and liquidity-pool reserve manipulation exploit. Its proposed sequence depends on reporting that transfers into the pair count as sell volume, while a function named flushLpSellRecycle() burns NEM held by the pair. Repeated skim() calls are reported to return the operator's tokens as the pool's NEM holdings shrink, before the retained inventory is sold against the altered pool state.That sequence is an assessment in the analysis. The token's source code and the individual burn, reserve, and skim-related events were not decoded there. The proposed sequence is therefore not an event-by-event proof of the vulnerability.The reported count of 42 cycles has a limited technical anchor: the transaction's calldata ends with 0x2a, or decimal 42. Without ABI decoding, that word does not by itself prove what the parameter controls or how many cycles executed. Likewise, 1,608 logs show extensive transaction activity in the analysis, but an unclassified log count cannot independently establish 42 repetitions of a particular mechanism.Flash-borrowed liquidity is another inference. SentinelTX describes large, same-transaction BSC-USD round trips involving Venus vUSDT, PancakeSwap, and two unlabeled contracts. It did not decode loan origination and repayment events. The analysis assigns the direct loss to the affected pair's liquidity providers, but does not provide a reconciled reserve-loss calculation matching the reported US$821,920.Diagram 1. Read the numbered rows from top to bottom, and each row from left to right. The analysis assesses a skim-and-burn reserve-desynchronization loop: transfers into the LP register pending sell volume, flushLpSellRecycle() burns NEM held by the pair, skim() returns the operator’s tokens, and repeated rounds precede a final inventory sale. This is a reported mechanism, not an event-by-event decoded proof. The reported 42-cycle count is only partially corroborated by the raw calldata word 0x2a, not ABI-decoded; no exact loop count is encoded in this schematic. Equal-width dashed arrows summarize the reported sequence, not token quantities.Slate labels identify the stated actions; arrows indicate the relationships written in each row, not quantities.NEM token: 0x9cf0e3ad4efa7ab602d7b5a38c55795cfa777777. LP/pair: 0x840e19dcca541ee0b55a3c67e900a39d523b12b8; its victim-pool role is a source claim consistent with the analysis’s records. Attack contract: 0x5e6d1f40be466dd2facc94a26818948ecd3b1ca2. Signer/proceeds recipient: 0xfd929b0f270dfea6c4827262b4e2bf6ea50fe9b6; operator identity is not established.Source: SentinelTX analysis. Source location: Transaction Typology → Mechanism: observed, inferred and claimed; Scheme description (assessment).Funding supports a relationship, not an identityThe funder, 0x96cb6bec56e43b2f16c05e1af4776fbc7b9713b5, supplied the initial gas and the NEM inventory later committed to the attack contract. Its first-seen date is October 20 in the analysis. The repeated funding, inventory transfers, and timing support SentinelTX's assessment that the two addresses were operated by the same actor or closely coordinated actors. Common ownership is not proven, and no person or organization is identified as the operator.Six helper contracts reportedly returned their NEM balances short by exactly 1 NEM each. SentinelTX interprets the similar interactions as rehearsal against mainnet conditions, an operational assessment rather than a separate finding of intent. Six listed WBNB recipients are classified as probable helpers; their mapping to the six creation records is not established.The inventory has another upstream lead. An unlabeled contract, 0xaee6b842f94281653dde98da97debd93007de2a1, reportedly sent the funder 780,757.29 NEM across 45 transfers. In itemized examples, NEM arrived with BSC-USD and the same BSC-USD quantity was returned shortly afterward. SentinelTX suggests a reward, staking, or distribution mechanism as a possible explanation, but the contract's function was not decoded.The contract’s ownership and any additional loss remain unproven. Shared first-seen dates with the token and pair do not establish ownership. The analysis also records a post-exploit sale by the funder through a TransitSwapRouterV5-labeled route, but its relationship to any additional loss remains unresolved.Following the exit without overstating the endpointThe analysis traces a BSC stablecoin payment into the router, a correlated Relay delivery on Ethereum, and three transfers to CoW Protocol settlement: 250,000.0 USDT, 250,000.0 USDT, and 225,384.763364 USDT. Each Ethereum quantity carries the source's unverified-amount qualification.SentinelTX attributes the difference between the routed and delivered quantities to bridge fees and spread. That remains an assessment: the amounts are in different token denominations, the destination quantity is unverified, and no itemized fee accounting is provided.The Ethereum native ledger is reported as four inbound transfers totaling 296.192678708450769578 ETH, no outbound ETH, and 0.000205413793461084 ETH used for gas. Its resulting balance is 296.192473294657308494 ETH. All of these ETH figures are unverified. The counterparties and hashes of the four incoming ETH transfers are not itemized in the analysis, so the article cannot supply a complete leg-by-leg conversion reconstruction.The recorded endpoint is an address holding native ETH. It is not evidence of fiat cash-out. The WBNB contract's Binance-related label does not make it a Binance customer deposit address, and the CoW settlement contract is described as a non-custodial venue. No custodial exchange deposit is established by the analysis.The BSC exit also contains an EIP-7702 authorization that delegates execution to another address. SentinelTX records that field but treats its batching interpretation as an assessment. Delegation on Ethereum is not established. These technical roles do not identify a beneficial owner.Diagram 2. Read the numbered rows as the reported route, not three independent totals. The analysis records 726,307.1011248019 BSC-USD from the attack contract to Recipient A and the same quantity forwarded through the Socket router on October 21. A correlated Relay record reports delivery of 725,384.763364 USDT to the same address on Ethereum; that destination quantity is unverified. Three CoW settlement legs follow. The October 24 balance read reports 296.192473 ETH, while the analysis’s ledger calculation gives 296.192473294657308494 ETH; both are unverified. Display values are approximate. The four inbound ETH counterparties are not itemized, so the final arrow summarizes the analysis’s conversion sequence and later balance, not a fully reconstructed transfer leg. Equal-width arrows are schematic; the BSC-USD, USDT and ETH values are not summed or treated as interchangeable loss amounts.Slate: 1 · BSC collection and router exit; Sage: 2 · Relay delivery and CoW swaps; Amber: 3 · Later Ethereum balance read. Equal-width arrows show stated routes, not quantities.Recipient A on both chains: 0xfd929b0f270dfea6c4827262b4e2bf6ea50fe9b6. BSC attack contract: 0x5e6d1f40be466dd2facc94a26818948ecd3b1ca2. Socket router: 0x50cfe7c1938db66a1a6d2e86d36f39fbef3d5c4a; the analysis’s literal attribution includes “Socket OpenRouter (Ethereum)” despite the BSC transaction. Relay-labeled Ethereum sender: 0xb92fe925dc43a0ecde6c8b1a2709c170ec4fff4f. CoW settlement recipient: 0x9008d19f58aabd9ed0d60971565aa8510560ab41. No operator identity or custodial exchange deposit is established.Source: SentinelTX analysis. Source location: Executive Summary → Exit; Transaction Chronology → Fund-flow sequence and Gross versus forwarded amounts; Exchange-deposit and venue legs.Why the look-alike transfers were excludedThe original source distinguishes real funding from records it classifies as suspected address poisoning. At 01:07:18, a look-alike of the funder sent 0.007 units of a token whose symbol imitated BNB using non-Latin characters. Its amount mirrored the real gas funding, but the analysis found no value-bearing onward movement and excluded it.A mirror-image record named a look-alike of the signing address. The two full addresses are distinct, and the mirror-image record’s transaction hash is not provided. Neither poisoning record is used as evidence of common control or an economic connection.The analysis also excludes unsolicited airdrops as spam, including two tokens recorded with a burn-address emitter and other tokens with miscellaneous names. An appearance in a transaction history is not enough, within the source's own methodology, to include a transfer in the traced proceeds.Recovery implications and analytical limitsSentinelTX's practical priority is the last recorded Ethereum holding and any later onward transfer. The analysis describes potential investigative leads in the funder's upstream financing and in request metadata that infrastructure operators might hold. The availability of that metadata and any resulting recovery action are not established.The source rates near-term recovery prospects as moderate, but that is its expert assessment, conditional on an unverified balance observation. It is not a recovery probability, an assurance that funds remain available, or a promise that a service provider can freeze native ETH. The analysis’s legal-process and negotiated-return suggestions require case-specific decisions by the affected parties and their qualified advisers; they are not legal instructions from ChainBounty.Important analytical limits remain: the mechanism has not been decoded cycle by cycle, flash liquidity is inferred, the funder's earlier history is not itemized, two in-transaction counterparties lack an onward trace, and the four ETH receipts lack individual detail. The reported loss remains unreconciled with the recorded proceeds. The analysis does not specify its complete query windows; its conclusions are limited to the records discussed. No personal identity, custodial deposit, or connection to NEM/Symbol is established.Figure 3. The analysis supports a reported route from BSC proceeds through Relay to Ethereum and CoW settlement, subject to its quantity and balance qualifications. Approximately US$821,920 is a publicly reported loss claim; 726,307.1011248019 BSC-USD is the analysis’s recorded proceeds payment. These differently denominated figures are not directly interchangeable, and the source does not reconcile the loss gap. The mechanism is not decoded cycle by cycle; no personal or organizational identity, custodial exchange deposit, fiat cash-out, or connection to the unrelated NEM/Symbol project is established. The October 24 balance observation of 296.192473 ETH remains unverified and is not a statement of a live current balance. Rounded display values are approximate.Slate identifies section headings, not certainty or risk.The balance observation and Recipient A role refer to 0xfd929b0f270dfea6c4827262b4e2bf6ea50fe9b6 on Ethereum, not the separate poisoning look-alike identified in the analysis.Source: SentinelTX analysis. Source location: Key findings and certainty; Transaction Chronology → Coverage against the claim and Cash-out endpoint; Transaction Typology; source limitations.Sources and scopeThe transaction findings, address roles, and analytical assessments in this review are attributed to SentinelTX’s analysis of case CASE-20261024-NEM1. The appendix preserves its full address and transaction references. It should be read as a source register, not as independent verification of the underlying blockchain records.The press context in SentinelTX’s analysis comes from search-result snippets attributed to TokenPost, DEV Community, KuCoin, PANews, TechFlow, and CryptoBriefing. These are attributed reporting references, not claims that the complete pages or underlying SlowMist posts were reviewed for this article.Amounts described as unverified require corroboration. Service labels identify the roles assigned to addresses in the analysis; they do not establish ownership or custody. The mechanism and recovery assessments retain their stated qualifications, and the October 24 balance observation must not be treated as a live balance.Appendix: full identifiersThe following register lists 31 full addresses and 21 full transaction hashes cited in SentinelTX’s analysis. It is not a complete transaction ledger. Address roles and service labels do not establish operator identity.Full addresses1. 0xfd929b0f270dfea6c4827262b4e2bf6ea50fe9b6 Exploit transaction signer and proceeds recipient on BSC; same address receives the reported Ethereum delivery. The analysis records BSC delegated code. Operator identity is not established.2. 0x5e6d1f40be466dd2facc94a26818948ecd3b1ca2 Attack contract on BSC and payer of the recorded 726,307.1011248019 BSC-USD proceeds.3. 0x9cf0e3ad4efa7ab602d7b5a38c55795cfa777777 NEM token contract on BSC. NemTokenV2 is a press-source name, not independently verified here.4. 0x840e19dcca541ee0b55a3c67e900a39d523b12b8 Contract identified by press as the USDT/NEM pair on PancakeSwap. The analysis considers its victim-pool role consistent with the recorded transfers.5. 0x96cb6bec56e43b2f16c05e1af4776fbc7b9713b5 Funder on BSC: recorded source of the signing address’s first gas and NEM inventory. No operator identity established.6. 0xaee6b842f94281653dde98da97debd93007de2a1 Unlabeled BSC contract recorded as the funder’s NEM source. Its function is not decoded; a project-side mechanism is only an assessment.7. 0x63c0c19a282a1b52b07dd5a65b58948a07dae32b EIP-7702 delegate named in the authorization list of the BSC exit transaction. No label; type not classified in the analysis.8. 0x50cfe7c1938db66a1a6d2e86d36f39fbef3d5c4a BSC bridge-exit router identified as Socket OpenRouter in SentinelTX’s analysis. This entry concerns the recorded BSC transaction.9. 0xb92fe925dc43a0ecde6c8b1a2709c170ec4fff4f Sender of the reported Ethereum USDT delivery. Exact source label: “Relay.link.”10. 0x9008d19f58aabd9ed0d60971565aa8510560ab41 Recipient of the three Ethereum USDT legs. Exact label: “CowProtocol, Exchange.” Described by the analysis as a non-custodial settlement contract.11. 0x07964f135f276412b3182a3b2407b8dd45000000 Route used for the funder’s post-exploit NEM sale on BSC. Exact label: “TransitSwapRouterV5.”12. 0xfd5840cd36d94d7229439859c0112a4185bc0255 BSC in-transaction BSC-USD counterparty. Exact label: “Venus USDT, vUSDT, DEX.”13. 0x238a358808379702088667322f80ac48bad5e6c4 BSC in-transaction BSC-USD counterparty. Exact label: “PancakeSwap.”14. 0x92b7807bf19b7dddf89b706143896d05228f3121 Unlabeled in-transaction BSC-USD counterparty on BSC; onward movement not established.15. 0x4f31fa980a675570939b737ebdde0471a4be40eb Unlabeled in-transaction BSC-USD counterparty on BSC; onward movement not established.16. 0x370a7e2d300c14d79d4a7ee07aaca46c4b3012cf Listed with the following address under submitter and target of the Ethereum delivery transaction. The roles and attribution are unverified.17. 0xccc88a9d1b4ed6b0eaba998850414b24f1c315be Listed with the preceding address under submitter and target of the Ethereum delivery transaction. The analysis does not separately verify the mapping or attribution.18. 0xbb4cdb9cbd36b01bd1cbaebf2de08d9173bc095c WBNB contract on BSC. Exact label: “Binance, WBNB Token, Token Contract.” Not a Binance customer deposit address in the analysis’s account.19. 0x2db7fca7a84a4ae69d41aec8d74b96b679c8ac5e First of six listed WBNB recipients on BSC, classified as probable helpers. Their mapping to helper-creation records #1–#6 is unresolved. The reported 0.0001 WBNB quantity is unverified.20. 0xbae2628c3f926971d4fc66c16120b2c7e0dce42a Second listed WBNB recipient on BSC; probable helper, with creation-record mapping unresolved.21. 0x0c3dac1d3b6f870b5bca16b7926631b525216865 Third listed WBNB recipient on BSC; probable helper, with creation-record mapping unresolved.22. 0xe1a9d2ecfb453be4608c126ef95ee71faec7f9cc Fourth listed WBNB recipient on BSC; probable helper, with creation-record mapping unresolved.23. 0x07d792806989300cd3b5d05329fea154a32ad96b Fifth listed WBNB recipient on BSC; probable helper, with creation-record mapping unresolved.24. 0xa16f9a316a2b9ef97994cd47991b72ecbebfd7db Sixth listed WBNB recipient on BSC; probable helper, with creation-record mapping unresolved.25. 0x50c4e75a512f2a14a7b304787adf79c4531a5909 Unlabeled code-bearing recipient of the residual BNB route at 03:40:52 UTC on BSC. The source does not provide that transaction’s hash.26. 0x97caca78ac2a94c67643d07843f85afaa44a3ea5 Unlabeled BSC-USD source to the funder and address appearing in residual-route calldata. The source explicitly treats a swap-route executor role as an unverified lead, not established funding attribution.27. 0x96cb0a81cd849f21e512f5d6eda78bdf1c0713b5 Look-alike of the funder, excluded as suspected address poisoning. Distinct from the real gas-funding address.28. 0xfd92b74d57b02814ea2591bd963d1fae390fe9b6 Look-alike of the exploit signer/proceeds recipient, excluded as suspected poisoning. It is distinct from the address receiving the recorded proceeds.29. 0x058941553ea64444077522d6b5edc2e09655ef66 Token contract used by the suspected poisoning record; symbol imitates BNB using non-Latin characters. Not native BNB.30. 0x5c718fc9c1bc1ca6d55b3c9c564153d98faff2d0 Unsolicited token identified among excluded spam records with a burn-address emitter.31. 0x1303753839659cd4ca526a9c2e7091cc68be26ab Second unsolicited token identified among excluded spam records with a burn-address emitter.Full transaction hashesTimes below refer to October 21, 2026, UTC. Transaction references and classifications are attributed to SentinelTX.1. 0x57b1847f6f2cf3d1676f6ba38064c0756d1fbec9b502c5dc662e35a2307fb0dd BSC. First gas funding, October 21 at 01:00:17 UTC; 0.007 BNB, unverified amount.2. 0xe9827bcce1262daf9a6026afdce9a4d51bf7e28dcd7d3ba767c9684fc8523468 BSC. Second gas top-up, stated as 0.01 BNB. The analysis places it in the preparation interval but does not give an exact time.3. 0xcbcdc77b393a30bf3212f80a8afdc334af642dc9615d47582cc5302f739da924 BSC. Anchor cited for NEM inventory funding. The analysis does not itemize all sixteen NEM transfer hashes.4. 0x54842ae0334a6b4bd2b24fbbe0251ea2c302f2ab253f87f2340b7462a7d8a4cb BSC. NEM transfer into the attack contract at 03:28:30 UTC; 767,811.3061168424 NEM, unverified amount.5. 0xfb093c96c0094cbcca10801f97ed2e5ed3d96550ce64b544df5a349545723f91 BSC. Exploit transaction, block 128,866,147, 03:28:50 UTC. SentinelTX classifies the payment of 726,307.1011248019 BSC-USD to the signer as confirmed.6. 0x4da49613a58f3d872c5991c0b7fc1a3d4ebb6b2b3c55fab768c490e57b104a68 BSC. Router exit, block 128,867,454, 03:38:38 UTC; source hash used to correlate the Relay bridge record. SentinelTX records EIP-7702 type-4 execution.7. 0xc4acd18a0e8f4b4f24b47ce6e57a7c936b148108327236125daac250d07bc8bb Ethereum. Reported bridge delivery, block 26,238,334, 03:39:11 UTC; 725,384.763364 USDT, unverified amount.8. 0xfc7fc1af22358f55ea4f3847efb7a70514e81b4d0d8c5da392c7874609ab2533 Ethereum. First CoW settlement leg, 03:46:11 UTC; 250,000.0 USDT, unverified amount.9. 0x0757d2285bd862798c3b52181e919e8853d6037e8096e4fdf7456a7e3269ab0d Ethereum. Second CoW settlement leg, 03:47:11 UTC; 250,000.0 USDT, unverified amount.10. 0xbcef08a442ca7bba882c43ebf61fbc6fc285a70d7d207238bbea797b17817cfb Ethereum. Third CoW settlement leg, 03:47:47 UTC; 225,384.763364 USDT, unverified amount.11. 0xf66fa8c86299c9de6798556d42966fb9fa8c6b47b0d1eb8080344685af3668fa BSC. Funder’s post-exploit NEM sale, 03:37:01 UTC, through the TransitSwapRouterV5-labeled route.12. 0x38739784a8b13de37666e5770de7d2603a92ee50f233789b97ddd7c468300ed2 BSC. Example inbound cycle to the funder, 03:26:19 UTC, including 12,571.42 BSC-USD and NEM, as stated in the analysis.13. 0x57a6519c13ad203c479d3166fea6ddefc46ad994d14e665c939778ab12f97d57 BSC. Example corresponding BSC-USD return, 03:26:45 UTC.14. 0xce77892c0e98a893f0b109d0f905c9423337addec5142edaf75be07eb3a73f53 BSC. WBNB transfer to probable helper 0x2db7fca7a84a4ae69d41aec8d74b96b679c8ac5e.15. 0x645edaec509f12f493ca15a42e793fc731dfc0610da85b7a1ee59dd7c609f0d7 BSC. WBNB transfer to probable helper 0xbae2628c3f926971d4fc66c16120b2c7e0dce42a.16. 0x0e714d980478f9f636eae18d81ec5399e66eeee6926c113e886b243818e553df BSC. WBNB transfer to probable helper 0x0c3dac1d3b6f870b5bca16b7926631b525216865.17. 0xec0de15f90e82015087eae522d2771de1ee8ac192cd91b8a851fa802079d34c6 BSC. WBNB transfer to probable helper 0xe1a9d2ecfb453be4608c126ef95ee71faec7f9cc.18. 0xa3b2e00ade40364427fbcc08803fe9fa3c7de8aac45dcd92986e140890150ea9 BSC. WBNB transfer to probable helper 0x07d792806989300cd3b5d05329fea154a32ad96b.19. 0xfb5384ed31469f13842a77a05ca0511402b7bad0d8af5f858de5acb9155e7124 BSC. WBNB transfer to probable helper 0xa16f9a316a2b9ef97994cd47991b72ecbebfd7db.20. 0xcf4469e6214a085023251542c924fc468be8856a144075ddaf47360fcc8792e3 BSC. WBNB transfer to attack contract 0x5e6d1f40be466dd2facc94a26818948ecd3b1ca2.21. 0x2b407b29b19baf491bfbcdd2a2e9c67f939e17bae22ffff6bd8f6287646326f8 BSC. Suspected address-poisoning record at 01:07:18 UTC. Excluded from economic tracing and attribution.Other explicit identifiersCase reference: CASE-20261024-NEM1.Chains: BNB Smart Chain, chain ID 56; Ethereum, chain ID 1.Exploit calldata selector: 0x05d546ef. Final raw word: 0x2a, decimal 42. No ABI-decoded meaning is established.BSC exit observed byte pattern: 0x095ea7b3, described in the source as an approve pattern; inner router call not ABI-decoded.Control-call selector: 0xe9ae5c53. Ethereum delegated-code status is not established.BSC authorization nonce: 0x32. BSC transaction nonce: 0x31.Reported route text: "Source":"BUNGEE_AUTO", "AmountInUSD":"6.781519". This describes the residual BNB route, not an added valuation of the main proceeds.Helper-creation record identifiers: #1–#6; source block range 128,850,621–128,864,238. Full creation hashes are absent from the original narrative.Ethereum first control-transaction block: 26,238,366; nonce 0. Its hash is not supplied.Residual BNB transaction block: 128,867,751, at 03:40:52 UTC. Its hash is not supplied.Coverage of the identifier registerThe full set of sixteen inventory-funding transaction hashes is not enumerated.The full set of 45 inbound NEM transfer hashes for the upstream contract is not enumerated.The four inbound ETH receipt hashes and counterparties are not itemized.The helper creation transaction hashes are not itemized.The WBNB wrap transaction hash at 01:31:59 UTC is not provided.The mirror-image poisoning transaction hash, burn-emitter address, and remaining spam-token identifiers are not supplied in full.The full residual BNB route transaction hash and all control-transaction hashes are not provided.These omissions limit reconstruction of the individual movements and the helper-creation mapping. The register does not infer missing identifiers.
Blog
Gravity Bridge Exploit: Full Attacker Fund Flow Traced — 113 Transactions Reveal Sophisticated…
Gravity Bridge Exploit: Full Attacker Fund Flow Traced — 113 Transactions Reveal Sophisticated Laundering OperationThe laundering infrastructure behind the recent Gravity Bridge exploit has now been largely uncovered.After tracing 87 confirmed attacker transactions and an additional 26 downstream movements, the overall flow of stolen funds is becoming clear. What initially appeared to be a straightforward bridge exploit has evolved into a highly structured laundering operation involving decentralized exchanges, relay wallets, non-custodial swap services, and centralized exchanges.This report summarizes the complete fund flow observed so far and highlights the remaining recovery opportunities.Executive SummaryTotal tracked transactions: 113Initial stolen assets converted into ETH almost immediatelyApproximately $4.7M converted through KyberSwap and 1inch2,600 ETH consolidated into a secondary aggregation walletFunds dispersed through dozens of one-time relay walletsConfirmed deposits identified at ChangeNOW and KuCoinMultiple staging wallets still hold potentially recoverable fundsSeveral laundering paths remain active and require real-time monitoringPhase 1 — Asset ConversionThe attacker-controlled wallet:0x7B582033061b96cC3F9421e73a749ED7C62da1F9immediately began converting stolen stablecoins into ETH.The swaps were executed primarily through KyberSwap and 1inch, suggesting the attacker wanted to reduce exposure to token freezes while maximizing liquidity.Observed transactions include:$100K USDC → ETH$200K USDC → ETH$500K USDC → ETH$400K USDT → ETHMultiple additional swapsIn total:Approximately $4.3M USDCApproximately $434K USDTwere converted into ETH within a short time window.The rapid conversion indicates pre-planning and suggests the operator anticipated potential blacklisting or asset recovery attempts.Phase 2 — ETH ConsolidationAfter conversion, the attacker consolidated funds into a second wallet:0x4d3ca32e687e871a58b78AcAc73bE59AC37C7A47A total of 2,600 ETH was transferred through multiple transactions:600 ETH500 ETH500 ETH500 ETH500 ETHThis wallet appears to have functioned as the primary distribution hub for the laundering operation.Rather than cashing out directly, the operator implemented a layered relay strategy designed to fragment attribution and complicate tracing efforts.Phase 3 — Distributed Relay LaunderingThe most notable discovery is the laundering architecture itself.Instead of sending large transfers directly to exchanges, the attacker repeatedly split funds into dozens of temporary wallets.The observed pattern resembles:Primary Wallets → One-Time Relay Wallets → Swap Service / Exchange → Cross-Chain ExitIndividual transfers were commonly observed in the 6–10 ETH range.This methodology significantly reduces the visibility of exchange deposits and makes automated clustering more difficult.The pattern appears intentional and operationally mature.Confirmed ChangeNOW ActivityThe largest identified laundering route currently leads to ChangeNOW.Observed destination:0xeba88149813bec1cccccfdb0dacefaaa5de94cb1Estimated deposits:Approximately 114 ETHRoughly $230,000 equivalentBecause ChangeNOW is non-custodial, recovery options are more limited.However, transaction records still exist.The highest priority investigative question is determining what assets these ETH deposits were converted into.Particular attention should be given to:Monero (XMR)Privacy-focused assetsCross-chain bridge destinationsIf conversion into privacy-preserving assets occurred, tracing may become significantly more difficult.Confirmed KuCoin DepositsA second laundering path has been identified through KuCoin.Known deposit address:0x45300136662dd4e58fc0df61e6290dffd992b785Estimated deposits:Approximately 6 ETHAdditional suspected deposit address:0x58edf78281334335effa23101bbe3371b6a36a51Status:Further confirmation requiredUnlike ChangeNOW, KuCoin operates as a custodial exchange and maintains KYC records.This creates a potential recovery and attribution opportunity if law enforcement or affected parties act quickly.Remaining On-Chain FundsSeveral wallets remain active and continue to warrant monitoring.Primary Staging Wallet0xc8c71ae4261e55a66d9967f2ac252be4e669f562Current observations:Received 59 ETHOnly 15 ETH moved onwardApproximately 44 ETH potentially remains under attacker controlThis wallet may represent an operational staging point rather than a final cash-out destination.Additional Unresolved Destinations0xf1ed839d08309e2a52e58d69b06d286d35fc18bc — 15 ETH0xe1e471614305656114c39294637b65adccf665a3 — ~13 ETH0x58432e011aa493c404f80409d997b1eabdfd8e24 — 9 ETH0x79f376453537878eeb79fb7d2cdb2c10bc58f454 — 9 ETH0x98d9022fa2789c0d8e9cd49707599c6848619ed8 — 10 ETHThese wallets currently represent unresolved portions of the laundering network.Immediate Investigative Priorities1. KuCoin Cooperation RequestThis remains the strongest recovery opportunity.Required actions:Identify account owner(s)Preserve account recordsFreeze assets if still presentObtain associated KYC informationTiming is critical.2. ChangeNOW Exit TracingInvestigators should determine:Destination chainDestination assetConversion timingPotential privacy-coin exposureThis path likely contains the most important unanswered questions in the investigation.3. Real-Time Monitoring of Staging WalletsThe wallet:0xc8c71ae4261e55a66d9967f2ac252be4e669f562should be monitored continuously.A significant portion of attacker-controlled funds may still be sitting on-chain.Any future movement could reveal:Additional exchange depositsAdditional swap servicesNew laundering infrastructureFinal cash-out attemptsConclusionThe Gravity Bridge attacker did not rely on a simple exchange cash-out strategy.Instead, the operator employed a structured relay-wallet laundering network designed to fragment attribution, obscure exchange deposits, and delay investigation.While a meaningful portion of the funds has already entered laundering channels, several opportunities remain.The most actionable leads currently include:KuCoin deposit attributionChangeNOW conversion tracingMonitoring of the 59 ETH staging walletThe next movements from these wallets will likely determine whether investigators can continue following the money — or whether the trail disappears into privacy infrastructure permanently.
ChainBounty
5 months ago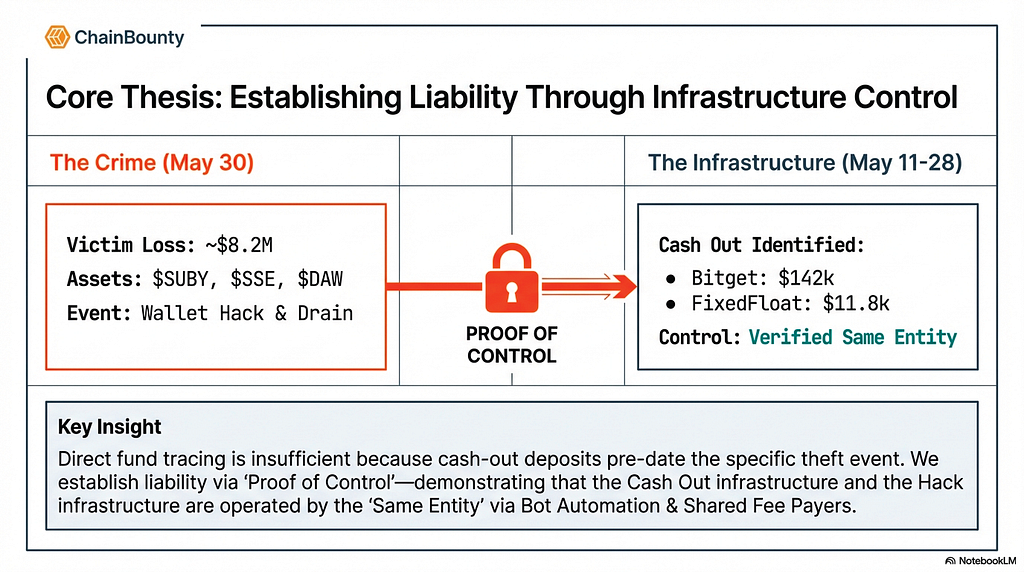
Unmasking a Sophisticated Solana Scam Network: A $SUBY Forensic Investigation
How automated bots and shared infrastructure revealed a 10-month-old organized crime syndicate.The blockchain never forgets, but it can be incredibly complex to navigate. Recently, ChainBounty conducted a deep-dive forensic investigation into a significant asset theft involving $SUBY and other Solana-based tokens. What began as a single incident report evolved into the discovery of a professional, long-standing scam infrastructure that has now led to an active criminal investigation by the Cyber Crime Investigation Division in Seoul, South Korea.1. The Incident: Precision and AutomationOn May 30, 2025, a victim’s wallet was drained of approximately 8.2 million $SUBY tokens, along with $SSE and $DAW. The speed of the transfer was alarming.Our forensic analysis revealed that this wasn’t a manual operation. The assets were moved to an intermediary wallet (46S5bgHq...) and immediately processed through automated scripts. These bots executed swaps into stablecoins and distributed funds across multiple "hop" wallets with 0-second latency, ensuring the trail became as fragmented as possible within minutes.2. Identifying the “Cash Out” InfrastructureBy tracing the flow of stolen assets, we identified two primary exit points: Bitget Exchange and FixedFloat (a mixing service). While some deposits to these platforms occurred shortly before or after the specific $SUBY theft, our “Infrastructure Analysis” proved a definitive link. We discovered a massive, interconnected network:27 Common Fee Payers: A cluster of wallets consistently funded the gas fees for the attack wallets.63 Shared Addresses: These wallets acted as a central hub for multiple thefts over a 10-month period.The Forensic Anomaly: Why tracking the criminal organization is more effective than tracking the tokens aloneThis confirms that the attackers are not “lone wolves” but an organized syndicate operating a “Scam-as-a-Service” model on the Solana network.3. The Evidence: The Smoking GunThe most compelling evidence of organized crime was the Machine-like Transfer Patterns. Our timeline analysis showed batch processing intervals of exactly 15 to 28 seconds. This level of synchronization is only possible through a dedicated command-and-control (C2) botnet designed for money laundering.Through our investigation, we identified over $142,430 USDT funneled through the Bitget deposit addresses associated with this specific group.Inhuman execution: Batch processing and mechanical intervals confirm the use of laundering bots.4. Active Investigation and Next StepsChainBounty has officially submitted this forensic package to the Seoul Metropolitan Police Agency. The investigation is currently focused on:KYC De-anonymization: Working with Bitget to identify the account holders behind the identified deposit addresses.Cross-Chain Tracking: Tracing funds that exited via FixedFloat into Ethereum and Bitcoin.Asset Freezing: Coordinating with exchanges to blacklist and freeze the identified criminal infrastructure.Conclusion: Vigilance in the Web3 EraThis case is a stark reminder that in the world of DeFi, your digital footprint — and that of the hackers — is permanent. At ChainBounty, we are committed to turning the tide against these scam networks.We urge the community to stay vigilant. Do not click on suspicious partnership links or authorize “blind signings” in your wallet. The scammers are professional, but so is our pursuit of justice.Join the Fight. Follow our investigation and report suspicious activities at our community: 🔗 https://community.chainbounty.io 📧 For inquiries: [email protected]#ChainBounty #Solana #Forensics #CyberCrime #Web3Security #OSINT #CryptoInvestigation
ChainBounty
9 months ago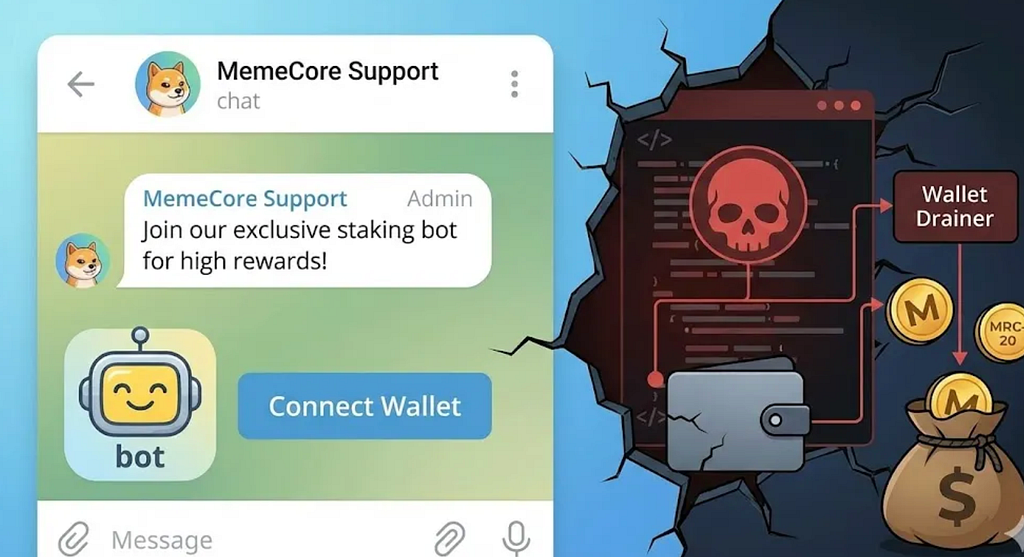
MemeCore (M) Digital Asset Theft Incident: On-Chain Forensics & OSINT Analysis Report
IntroductionThis report details a real-world case submitted by an applicant to ChainBounty’s Victim Relief Program. The victim approached us after suffering a significant loss due to a targeted social engineering attack. ChainBounty is actively assisting the victim by providing comprehensive on-chain forensics and intelligence analysis to trace the stolen assets and identify the perpetrators for law enforcement purposes.1. Executive SummaryThis report synthesizes the results of on-chain forensic analysis and Open Source Intelligence (OSINT) investigation regarding the digital asset theft incident that occurred between December 7 and 8, 2025.The incident appears to have originated from a social engineering attack targeting an active user of Memex, a major dApp in the MemeCore (M) ecosystem. The attacker impersonated community administrators and creators to lure the victim into a fake Telegram group, then induced them to connect their wallet to a fraudulent bot service using “high-yield staking rewards” as bait.The victim created a new wallet and transferred assets as instructed, but the flow was designed to funnel funds into the attacker’s scam network.On-chain analysis reveals that the stolen funds did not end with a simple transfer. A multi-stage laundering flow was observed, involving MRC-20 token swaps within the MemeCore network, repetitive transactions based on the WM contract, cross-chain bridging via Meson Finance, inflows into Centralized Exchanges (CEX), and dispersed withdrawals across multiple exchanges.Notably, a “direct-to-exchange” flow is clearly visible in the early stages. M tokens were directly transferred from the victim’s wallet to Suspect Bitget Deposit 1 (0x7a5d…), and this fund was collected into the exchange’s hot wallet (0x1ab4…) within a short period. This suggests the attacker operated a direct route to the exchange alongside other methods to accelerate cash-out early on.The damage is calculated based on two criteria:Total M Token Outflow (Direct): 2,151.11 M, approx. $2,881.39 (Combined sum of direct transfers to exchange + EOA/Gathering Wallet).Total M Token Outflow (Including Bridge): 8,280.11 M, approx. $11,150.17 (Direct outflow + Meson bridge outflow included).Furthermore, clues suggesting a connection to specific social accounts and developer community profiles were identified in Gathering Wallet 2 (0x1c00…5f), which was confirmed as a key hub for money laundering. Based on this, grounds to narrow down suspect candidates have been partially secured. However, this is a circumstantial judgment based on the correlation between public information (OSINT) and on-chain data, and is not a legally confirmed conclusion.1.1 Summary StatisticsThe key flows are summarized as follows:1.2 Summary of Key Flows (4 Core Paths)Path 1: Victim → Direct Outflow to Bitget (Attempt at Immediate Cash-out)A total of 2,140.72 M (approx. $2,867) was directly transferred from the Victim Wallet (0xdc54…) to Suspect Bitget Deposit 1 (0x7a5d…).The deposit was collected into the Bitget exchange hot wallet (Bitget 6, 0x1ab4…) within minutes (approx. 3–5 mins).This flow represents the attacker sending “M tokens that are easy to cash out immediately” straight to the exchange.Path 2: Victim → Gathering Wallet 1 → Meson Bridge → Gathering Wallet 2 (Mainstream of Indirect Laundering)After WM contract processing, 5 types of MRC-20 tokens were received by the Victim Wallet and then drained to Gathering Wallet 1 (0x8325…e6).In Gathering Wallet 1, MRC-20s were swapped back to M, and 6,129 M was bridged via Meson Finance (0x25ab…48d3).6,122.87 M arrived at Gathering Wallet 2 (0x1c00…5f) on the BNB Chain.Path 3: Gathering Wallets 1, 2 → Reconsolidation at Bitget Deposit 2 (Possible Mixing with Other Victims’ Funds)900.65 M from Gathering Wallet 1 and 5,007.02 M from Gathering Wallet 2 flowed into Suspect Bitget Deposit 2 (0xb408…).The combined total is 5,907.67 M. As there is a “possibility of other victims’ funds being mixed,” this needs to be interpreted separately from the victim’s sole damage amount.Subsequent collection into Bitget 6 (0x1ab4…) was confirmed.Path 4: Multi-chain Dispersed Withdrawal from Gathering Wallet 2 (Evasion/Smurfing)From Gathering Wallet 2, after swapping M → BNB, there is a record of 37.51 BNB being dispersed and withdrawn in 48 transactions to 5 exchanges: Bybit, Bitget, MEXC, Binance, and Remitano.Activity of the same address was confirmed on Arbitrum and Base as well as BNB, reinforcing the cross-chain laundering pattern.2. Incident Mechanism and Psychological AnalysisThis incident appears to have started from a social engineering scenario targeting human trust rather than technical flaws such as system vulnerabilities. It seems to be a variation of the typical “Pig Butchering (Sha Zhu Pan)” tactic adapted to the MemeCore ecosystem context. There are indications that the attacker analyzed the community atmosphere and the victim’s activity patterns beforehand to approach with a tailored script.2.1 Manipulating the Environment to Build Trust: “The Illusion of the Fake Room” The attack seems to have begun with an approach from an account mimicking an acquaintance active on Memex. In anonymous messenger environments like Telegram, profile pictures and Display Names can be configured similarly, and Usernames (Handles) are hard to distinguish with just a one-character difference. The attacker judged to have secured trust by exploiting these characteristics. The Telegram room the victim was invited to contained multiple accounts impersonating Admins and Creators. They staged the room to look like an “Official Community” by continuing conversations or sharing profit verification screenshots even before the victim joined. In such an environment, it was easy to mistake the room for an extension of the official Memex community, which became the basis for the fraud.2.2 Technical Deception: Fake Bot and Inducing Wallet Connection Once a certain level of trust was established, the attacker guided the victim saying, “You can receive staking rewards if you connect your wallet via the Telegram bot”. The method is close to a typical Phishing or Drainer type. The wallet (0xDC54…69b) the victim newly created and connected was a “clean wallet” with almost no transaction history. The moment the victim trusted the instructions and moved assets, it is likely the attacker secured control through one (or a combination) of the following methods:Possibility that the transaction signed via the bot was actually an Unlimited Token Approval, not staking.Possibility that it was designed to execute an asset Transfer transaction during the signing or connection process.Possibility that keys or permissions were exposed to the attacker during the wallet creation/connection process. The key point is that “Wallet Connection” may have turned into an act of handing over actual asset authority, rather than simple login or authentication.3. Technical Characteristics of MemeCore Ecosystem and Asset StructureTo interpret the fund flow, it is necessary to first understand the background of the MemeCore chain where the victim’s assets existed and the asset structure. This explains why the attacker performed repetitive swaps and why the laundering path developed into a specific pattern.3.1 MemeCore and Proof of Meme (PoM) MemeCore is a Layer 1 chain aimed at connecting the cultural value of Memes with an economic reward structure. It promotes Proof of Meme (PoM) as its consensus structure, which includes elements like community contribution and viral activities in the reward system alongside simple staking. The base asset of this chain is the M token. M is used for core functions such as gas fees, governance, and validator staking, and has relatively high liquidity, which is why the attacker ultimately pooled funds into M for laundering.3.2 MRC-20 Token Standard and Cash-out Constraints Tokens such as NinjaMEX, walxop, LIFT, Bubger, and Abudium identified in the swap path of this incident follow the MemeCore-specific token standard (MRC-20). These appear to be “transit tokens” temporarily passed through during the process of the attacker exchanging stolen assets on the internal DEX, rather than assets originally held by the victim. Technically similar to ERC-20, they are structured for the creation and circulation of meme tokens within MemeCore. The issue is external compatibility. Since it is rare for external chains, centralized exchanges, or bridges to directly support MRC-20, it is difficult for the attacker to move them out externally and cash them out in the MRC-20 state. Eventually, to proceed to the actual cash-out stage, they must go through the flow of: converting back to M on the internal DEX -> moving to an external chain (BNB Chain, etc.) via a bridge -> attempting cash-out via swap/dispersed withdrawal on the external chain. The massive internal swap transactions observed in the report are interpreted as reflecting the constraint of having to convert back to M for external export, along with the possibility of transit swaps intended to confuse tracking in some sections.4. Incident Timeline and Detailed Forensic ReconstructionThis incident is clearly divided into Reconnaissance & Testing on December 7 and the Main Exploit on December 8. The attacker checked the validity of the path the day before, and then stole all available assets and proceeded with rapid laundering the next day.4.1 Phase 1: Reconnaissance and Initial Infiltration (Dec 7) — Traces Left by Destination Choice Immediately after securing access rights, the attacker showed a pattern of verifying two things with small (or relatively small) transfers first, rather than moving the full amount immediately:Whether the wallet is actually usable by the attacker.Whether the exchange deposit is processed normally (no risk of detection/blocking). At 10:18 UTC, 388.717 M was transferred to Bitget Deposit 1 (0x7a5d…), and at 14:08 UTC, an additional 752 M was transferred via the same path. This flow aligns with the typical pattern of a small test followed by additional transfers. The notable point is that the receiving address 0x7a5d…337 is estimated to be a User-Assigned Deposit Address of a Centralized Exchange (Bitget), not a personal wallet. Funds flowing into this address were observed being collected into the Bitget hot wallet (0x1ab4…f23) within minutes. If cooperation with the exchange is established, there is a possibility that tracking can continue on an account basis (KYC-based).4.2 Phase 2: Full-Scale Asset Theft and Laundering (Dec 8) — Forced Conversion to M and Exfiltration The full-scale theft proceeded rapidly on December 8. In this phase, it is observed that repetitive processing of the WM contract and mass liquidation (swap) of MRC-20 tokens were carried out in parallel with simple transfers.4.2.1 WM Repetitive Processing Pattern: Between 06:45 and 06:49 UTC, 8 repetitive transactions occurred against the WM contract, confirming processing (Deposit/Withdraw) of approximately 8,000 M. This repetitive wrapping/unwrapping can be interpreted as (1) a staging to confuse tracking, or (2) a preparatory step to match the asset form required for subsequent swaps/bridging.4.2.2 Organized Outflow of 5 MRC-20 Tokens and Immediate Cash-out: Around 1:24 PM, continuous M→MRC-20 swap transactions via the internal DEX occurred in the victim’s wallet, which appear to have been performed by the attacker. Subsequently, these 5 MRC-20 tokens were transferred to Gathering Wallet 1 (0x8325…eae6), where a process of converting them back to M via the Swap Router was observed. This choice is pragmatic from the attacker’s perspective. The longer low-liquidity meme tokens are held, the greater the price fluctuation and tracking traces may become. It seems the attacker chose to quickly convert MRC-20 to M to increase mobility and cash-out potential.4.3 Phase 3: Cross-Chain Bridging and Final Concealment — Attempt to Evade Tracking via Chain Hopping The secured M tokens did not stay in the MemeCore chain for long and were observed moving to the BNB Chain via the Meson Finance (0x25ab…48d3) cross-chain bridge.Meson Bridge: 6,129 M Deposited.BNB Chain Arrival: 6,122.87 M received at Gathering Wallet 2 (0x1c00…5f) (Approx. 3 mins to arrive). Gathering Wallet 2 subsequently acts as a hub to send funds to exchanges or disperse them to other chains (Base, Arbitrum). It has a strong character of a “Operational Wallet” used repeatedly rather than a simple transit point.5. Fund Flow Structure AnalysisFunds drained from the victim’s wallet moved largely in two directions:Direct Outflow straight to the exchange (Priority: Speed).Indirect Laundering via gathering wallets and bridges (Priority: Evasion).5.1 Key Deposit (Receiving) AddressesSuspect Bitget Deposit 1: 0x7a5d...337 / Received: 2,140.72 M (~$2,867.47) / Note: Exchange Transfer.Gathering Wallet 1 (MemeCore): 0x8325...eae6 / Received: 5 MRC-20s + 10.39 M / Note: MRC-20 → M Swap.Gathering Wallet 2 (Multi-chain Same Address): 0x1c00...285f / Received: 6,122.87 M & Multi-chain activity (BNB/Arbitrum/Base).Suspect Bitget Deposit 2: 0xb408...dd5c / Received: 5,907.67 M (~$7,969) / Note: From Gathering Wallets 1, 2 → Exchange. Caution: Possibility of mixing with other victims' funds..5.2 Characteristics and Implications in Fund Flow First, the laundering strategy is split into two. Part of it prioritized speed by sending it quickly to the exchange (Path 1), while the rest tried to make tracking difficult through bridging and multi-chain dispersion (Paths 2, 4). Second, Bitget appears repeatedly. Both the direct outflow path (0x7a5d…) and the path from the gathering wallet (0xb408…) converge to Bitget deposit addresses. In particular, 0xb408… is a common point receiving funds from both Gathering Wallet 1 and Gathering Wallet 2, making it a candidate for a key cash-out window. However, as other victims’ funds may be mixed in this section, definitive conclusions should be avoided. Third, Gathering Wallet 2 (0x1c00…5f) functions as a central node that receives bridged funds and then performs exchange transfers or dispersion to other chains.5.3 Multi-Exchange Dispersed Withdrawal (Smurfing) Statistics (BNB Only) From Gathering Wallet 2 (BNB Chain) → Exchange Withdrawal Statistics:Bybit: 23.44 BNB / 16 txsBitget: 7.15 BNB / 2 txsMEXC Global: 5.06 BNB / 22 txsRemitano: 1.30 BNB / 4 txsBinance: 0.56 BNB / 4 txsTotal Exchange Withdrawals: 37.51 BNB / 48 txs / 5 Exchanges Note: After swapping M → BNB at Gathering Wallet 2, dispersed withdrawals were made to multiple exchanges. Activity of the same address was confirmed on Arbitrum and Base, reinforcing the cross-chain laundering pattern. Reference: Remitano is known as a platform widely used for P2P trading in Southeast Asia, which can serve as a reference clue for geographic profiling (Note: Do not conclude).6. Relevant Actor Intelligence AnalysisIn this investigation, by cross-examining on-chain flows and off-chain public activity traces, we secured clues to narrow down the relevant Actor (Actor A) and associated account/profile candidates. The central address of the analysis is Gathering Wallet 2 (0x1c00…5f), and OSINT information was organized around this address.6.1 Circumstances Connecting On-Chain Activity and Digital Identity In this case, some clues were observed where 0x1c00…5f, identified as a key gathering address, could be connected to external public activities. If the same address is repeatedly mentioned or exposed in specific social accounts or community profiles, it can serve as important evidence connecting on-chain addresses with off-chain activities. There are circumstances where a specific social account marked as (Redacted) posted the 0x1c00…5f address multiple times in posts related to past airdrops, whitelist registrations, faucet participation, etc. This raises the possibility that the address is associated with the account’s activity to a certain level.6.2 Detailed Identity Profile (Circumstantial) In the OSINT investigation, circumstances were confirmed where the social account/handle marked as (Redacted) is connected to a specific bounty/task platform (e.g., Superteam Earn) account/profile. The following additional information is derived from this:Real Name/Legal Identity: (Redacted)Country/Region of Residence: (Redacted; Partially consistent with Remitano usage patterns, etc.)Professional Identity: (Redacted; Based on self-introduction)Tech Stack Claims: (Redacted)Activity Character: (Redacted)Additional Explanation: Meaning of “Partially Consistent with Remitano Usage Patterns” Here, “Partially consistent with Remitano usage patterns” does not mean concluding residence in a specific country/region (e.g., Vietnam) solely because Remitano appeared. It is intended to be referred to as a supplementary clue that increases probability from the perspective of Geo-profiling. specifically:Regional Character of Remitano: Remitano is known to be relatively widely used for P2P On/Off-ramp (cash-out/settlement) purposes in Southeast Asia (especially Vietnam) rather than being used equally worldwide like global major exchanges. Therefore, if Remitano is naturally included and repeatedly observed in the multi-exchange withdrawal flow, the possibility that the actor’s living sphere/settlement environment touches the Southeast Asian region (including Vietnam) relatively increases.Hints form “Exchange Combination”: In this case, regional P2P channels like Remitano appear alongside general-purpose exchanges like Bybit, Binance, and MEXC. This combination can be interpreted as a form often observed in dispersed withdrawals considering the final cash-out route, rather than simple investor propensity.Therefore, Remitano traces are worth referencing as a “Geographic Clue Candidate”. However, it is a “Supplementary Clue,” not definitive evidence. Final confirmation must be made through cooperation/investigation data such as exchange KYC, login/access logs (IP/Device), and withdrawal methods (Bank/Payment info).7. Conclusion & Our CommitmentComprehensive Conclusion This incident, occurring on December 7–8, 2025, was a social engineering-based asset theft. Funds were laundered through two parallel paths:A direct path flowing straight into the Bitget exchange (Speed).An indirect path exfiltrated to external chains via the Meson bridge after internal swaps on MemeCore (Stealth).Additionally, circumstantial evidence links “Gathering Wallet 2” (0x1c00...5f) to specific social accounts and developer profiles, providing strong identification clues for law enforcement.Response Strategy ChainBounty has advised a phased response:Phase 1: Immediate reporting to law enforcement with key TxIDs and requesting asset freezing at Bitget.Phase 2: International cooperation review for cross-border tracking.Phase 3: Continuous monitoring of suspect addresses and community education on risk factors.Need help tracking stolen funds? Recovering stolen assets starts with professional tracking. If you have been targeted by a similar exploit, do not hesitate to reach out. ChainBounty’s Victim Relief Program provides the forensic evidence needed for law enforcement reporting and exchange cooperation.👉 Apply for Victim Relief Program: https://chainbounty.io/en/event/campaign-victim-support/(Disclaimer: This report is based on on-chain data and public OSINT. Identity-related content is circumstantial estimation. Final legal judgments must be confirmed through lawful procedures by law enforcement agencies.)
ChainBounty
9 months ago
 Become an Investigator