Community
Contribute by sharing insights and tips to strengthen the community.

Category

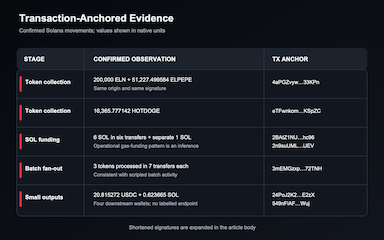
Malwarebytes reported a fake “GTA 6 leaked copy” site that placed a 1 SOL checkout in front of a download and loaded a remote multi-chain drainer script. The page exposed a Solana recipient address: 21iWU6FJWJ9FKKz4Jek2CyTh2x1fqs5jawjrNgE3nHjN.ChainBounty traced that address with SentinelTX. The result is useful precisely because it separates a public campaign indicator from proof of stolen funds. The address has real, transaction-anchored activity, but this investigation did not establish a victim-to-address transfer, an exchange cash-out, or an operator identity.WHAT THE SOURCE ESTABLISHESThe Malwarebytes analysis establishes the off-chain threat context: the fraudulent site presented a fake game purchase, calculated a near-total Solana balance transfer, and loaded code capable of targeting wallets on several EVM networks. It also published the Solana recipient and two infrastructure domains.Those findings do not automatically make every historical transaction involving the published address a theft transaction. That link must be proved separately on-chain.WHAT SENTINELTX OBSERVED ON-CHAINSentinelTX reconstructed a nine-address Solana cluster around the published seed. Four origin wallets supplied tokens or SOL to the seed, which then performed a batch token fan-out and several small USDC and SOL transfers.TRANSACTION ANCHORSToken collection:• 200,000 ELN and 51,227.499584 ELPEPE — 4aPGZvywmCZMeDqpKTfUiQjeHZYEDXJHRRLk4Vmq6YCBAwkWde7U3DimT6SamroZdwM4HKcgNWSceFgkoXY33KPn• 16,365.777142 HOTDOGE — eTFwnkombV3AvMmd9ucWeZ6LMbN9KuWnoSB8nQbJm9JsFAYAoUFAHxzy87R33JurAnAFFBrSWJF8awpyWcKSpZCSOL funding:• 6 SOL in six transfers — 2BAtZ1NUPqQnxM4vrvLDdN9fg5hy1Fh255nytZiUsG2Mhy61Y2YiVBc1UhiP2UrzydofBpCbzTHFpZkW62huhc96• A separate 1 SOL transfer — 2n9suUMLocSKpEvprh2g5EPecxKpZgEvCsiSFnn2DW5BJAAr6BJQcbm1EarFFZFyGq2Aj43efNTGiGYJZXCniJEVBatch fan-out:• Three tokens processed in seven transfers each — 3mEMGzxpcv3hvitz2N59TkiQesuYT4RVuNAbTrXteHdssZpCavaM8JN1z8fupRNwaiLTxmG52WK61fucduq72TNHSmall outputs:• 20.815272 USDC total and 0.623665 SOL total to four downstream wallets — 24PoJ2K27zjSrko4GkP49fP67XTC25xHYgX2aaSKcKcF3AwnNifrWXrqUGR12zEaMuqiP7BeVQ4JMCjkWME4E2zX; 549nFiAFvKU4sA9zUcTYKeZhS1SsJLpWeVfZ5X7XAa26RNm2DhYARTijor6sW9zqAupWfaCHEkDxK6SA3wz1mWuj; 4BXrF2MFbt7U6BshdLY12qQAK5kBV7VGEroaPLZZnVgBAZ2S1qX2qxMZq21fMapHsCAPZ4C41ZxLAKFCsJHQg9AJThe equal seven-way treatment of three tokens is consistent with scripted batch activity. The split SOL funding may be operational gas funding. Those are analytical interpretations, not proof that the cluster belongs to the drainer operator.THE KEY FORENSIC BOUNDARYNone of the nine addresses returned a reliable exchange, mixer, bridge, or named-service attribution. The four observed downstream wallets had no further movement within the traced scope. No confirmed cash-out leg was found.This means the investigation cannot defensibly claim:• that the observed tokens or SOL came from victims of the fake GTA 6 site;• that the batch fan-out was laundering rather than token distribution or spam;• that any specific person or organization controls the cluster;• a campaign-wide loss amount; or• a recovery target at a centralized exchange.The low-value outputs—about 20.8 USDC and 0.62 SOL—could represent settlement or account costs, but that remains inference. The on-chain evidence does not yet support calling them stolen proceeds.ADDRESSES WORTH MONITORING• 21iWU6FJWJ9FKKz4Jek2CyTh2x1fqs5jawjrNgE3nHjN — published seed; collection and redistribution; unattributed.• HMiD3578xUqodjNfLrFFTUwZww6aou6AKiX2NU33JXrM — six-part SOL supplier; unattributed.• 3TwWg4vVnVLBnwpJa8ZK3FrAbNucX8L3BtWtuwt7uVoC — ELN and ELPEPE supplier; unattributed.• 8ekCy2jHHUbW2yeNGFWYJT9Hm9FW7SvZcZK66dSZCDiF — largest USDC output and bidirectional counterparty; unattributed.The strongest next step is backward tracing of the four origin wallets and instruction-level decomposition of the seven fan-out recipients. Downstream monitoring should prioritize 8ekCy2jH…, because it is both the largest USDC recipient and a bidirectional counterparty.CONCLUSIONThe fake GTA 6 site is a credible wallet-drainer threat. The published Solana address is a valid indicator of compromise and has a structured on-chain history. But an indicator is not the same as an attribution.The defensible conclusion today is narrower: SentinelTX confirmed a nine-address collection-and-redistribution cluster, but did not prove that the observed funds were victim proceeds or identify a cash-out endpoint. That boundary should guide monitoring, exchange notices, and any future public claims.Source: Malwarebytes, “Fake GTA 6 ‘leaked copy’ drains your crypto wallet” (1 September 2026)https://www.malwarebytes.com/blog/scams/2026/09/fake-gta-6-leaked-copy-drains-your-crypto-wallet
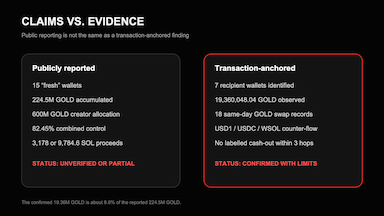
Executive summaryTrump Digital GOLD (GOLD) was promoted through an account styled as @realtrumpcoins1, briefly reached a reported market capitalization above $50 million, and then collapsed by roughly 98–99%. The branding implied political proximity, but no Trump family member publicly confirmed the token.SentinelTX did not validate the most dramatic public claims in full. It did confirm a narrower, transaction-anchored pattern: on 29 August 2026, a single Solana hub distributed 19,360,048.04 GOLD to seven wallets while USD1, USDC, and WSOL moved in the opposite direction in the same trading pattern. That is consistent with DEX swaps or pool interaction, but it does not by itself prove beneficial ownership, creator control, or the final cash-out amount.The evidence boundaryThe token mint is EMWtbpHaNqMbjUMZguuazhuZUVLWG3z4C5oZnGJPSqxS. The pair address examined was Hw5DkpbhbUd7QXj5syiShyPsYCpRCzbz2Vu433mdWEnU. SentinelTX case CASE-20260829-GOLD was explicitly marked partial because the unattended time cap prevented a complete trace. This report therefore separates verified on-chain observations from public reporting and inference.Confirmed fund flowThe central hub HLnpSz9h2S4hiLQ43rnSD9XkcUThA7B8hQMKmDaiTLcC sent GOLD to seven identified wallets on the incident date. The largest recipient received 16.73 million GOLD; the next two received approximately 1.09 million each. Four smaller recipients brought the observed total to 19,360,048.04 GOLD.At the same time, three counterparties sent USD1, USDC, or WSOL toward those recipients. This supports a DEX-swap or liquidity-interaction interpretation. It does not conclusively establish who controlled the wallets or whether every GOLD transfer was a sale.Public claims versus observed evidence15 newly created wallets: partial — seven recipients identified; “new” status not proved.224.5M GOLD accumulated: unverified — 19.36M GOLD observed.600M GOLD held by creator: unverified — creator wallet not identified.82.45% combined supply control: unverified — holder query incomplete.3,178 SOL (~$330K) or 9,784.6 SOL (~$1.01M) proceeds: both unverified; the figures conflict.$8.2M profit: not supported by transaction anchors in this investigation.The confirmed 19.36 million GOLD represents about 8.6% of the publicly claimed 224.5 million GOLD. The remaining 205.14 million GOLD was not traced in this session.Coordination indicators, not identity proofThe same date, the same sending hub, and the same swap pattern across seven wallets are indicators of coordination. They are not proof that a single person controlled every wallet. Several recipient wallets also had older activity, which weakens the blanket description of all participants as newly created wallets.The hub itself had activity before this incident and traded multiple meme tokens. It therefore should not be described as an incident-only attacker wallet without additional attribution evidence.Cash-out statusNo labelled centralized-exchange deposit, bridge, mixer, or exchange hot/cold wallet was identified within three hops of the seven recipients. The endpoint remains unresolved. This does not mean no cash-out occurred; it means the available investigation did not reach a labelled endpoint.What investigators should preserve nextThe highest-value next step is a deeper trace from the seven recipients, especially BNahnx13..., which received 16.73 million GOLD. Investigators should also resolve the token deployer from the mint creation transaction, reconstruct liquidity additions and removals for the pair, and seek exchange compliance matches for the identified wallets. Those steps are necessary before any defensible loss or profit number can be assigned.ConclusionThe chain supports a coordinated-looking GOLD distribution and swap pattern involving at least seven wallets and 19.36 million tokens. It does not yet support the full 15-wallet, 224.5-million-token, 82.45%-control, or $8.2-million-profit narrative. The strongest conclusion is therefore narrower: a concentrated, same-day market operation is visible on-chain, but identity, total proceeds, and final off-ramp remain unconfirmed.Sources: SentinelTX case CASE-20260829-GOLD; Cointelegraph; KuCoin News; CryptoRank. Public claims are attributed as reporting and are not presented as independently verified facts.
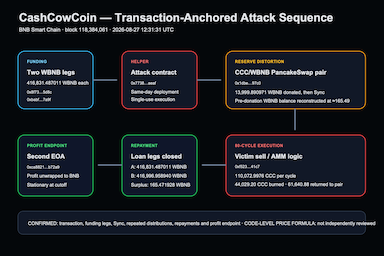
Executive SummaryOn 27 August 2026, a single BNB Smart Chain transaction used two large WBNB funding legs to manipulate the CCC/WBNB pool and extract 165.47192825151242 WBNB in profit. SentinelTX reconstructed the transaction flow and identified an important attribution distinction: the transaction signer paid the gas, but the profit was routed through a second contract to a different externally owned account.The evidence supports a reserve-manipulation exploit. It does not, by itself, identify the human operator.Evidence BoundaryThe primary evidence is the successful attack transaction 0x89d8050641019a5a75fa3dafb4f64fb153e4dd30c0f1f51d06a6cc206d3ead43, confirmed at block 118,384,061 on 27 August 2026 at 12:31:31 UTC. Public reporting describes a roughly $117,000 loss. Dollar values are therefore contextual; token amounts and transaction relationships below come from the on-chain reconstruction.Transaction-Level Attack SequenceThe attack signer 0x7977…13c4 invoked a helper deployed the same day. That helper aggregated 833,662.974022 WBNB across two funding legs. It then donated WBNB to the CCC/WBNB pair and triggered a reserve update before repeatedly trading against a system whose executable pricing depended on the manipulated pool state.Per confirmed cycle, 44,029.20 CCC moved to the burn address and 61,640.88 CCC returned to the pair. The loop was repeated 80 times. The mechanism matters more than the nominal flash-loan size: temporary liquidity only amplified a pricing dependency that trusted manipulable spot reserves inside one transaction.Repayment and Profit ExtractionThe first lender received exactly 416,831.487011 WBNB. The second contract received 416,996.958940 WBNB, including the surplus. One minute later, transaction 0x15be1604…acd97f moved the 165.471928 WBNB profit from that contract to 0xca8821…b72a9. Transaction 0xdaeada7c…8bf5 then unwrapped it into native BNB.At the investigation cutoff, the profit recipient held 165.53941989 BNB. SentinelTX found no confirmed direct deposit from this profit path to a centralized exchange, bridge, or mixer. That creates a live monitoring window, not proof that the funds will remain stationary.Address and Role MatrixAddressObserved roleAssessment 0x7977…13c4Attack transaction signerPaid gas; did not receive the profit0x7738…aeafSame-day helper contractAggregated funding and executed the sequence0x1dbe…97c0CCC/WBNB pairReserve state was distorted before Sync0xf523…41c7Victim sale/AMM contractExecutable pricing dependency requires code review0xbabf…7a9fSecond funding/repayment contractForwarded extracted profit0xca8821…b72a9Profit recipient EOAUnwrapped WBNB; funds stationary at cutoffWhat the Chain Proves — and What It Does NotThe chain proves the transaction ordering, token transfers, repayments, profit amount, and immediate post-exploit destination. It also shows that the signer and the profit recipient were different addresses.A shared gas source and a shared USDT source create a strong operational-cluster inference between relevant addresses, but they do not establish identity. The ultimate source of the second funding leg remains unresolved. The precise contract-level pricing formula and the relationship between two reported CCC contract identifiers also require separate code and deployment review.Investigator PrioritiesMonitor 0xca8821…b72a9 for first-hop movement, especially wrapping, bridging, or exchange deposits.Trace the upstream provenance of the second 416,831.487011 WBNB funding leg.Review the victim contract for direct or indirect reliance on pair reserves during executable pricing.Preserve the funding, attack, payout, and unwrap transactions as one evidence package.ConclusionThis was not simply a “large flash loan” event. The decisive control failure was allowing a manipulable pool state to influence executable pricing within the same transaction. The clearest recovery lead is the profit-recipient EOA, where the extracted value was still visible and had not entered a confirmed obfuscation or off-ramp service at the cutoff.Sources: SentinelTX on-chain investigation; Defimon Alerts; BitBase incident report.
TL;DRMoonwell’s Base lending markets reportedly lost approximately $8.7 million after an attacker manipulated the price of thinly traded MAMO collateral and borrowed liquid assets against the inflated valuation. Moonwell responded by setting Base Core Market borrow caps and MAMO/WELL supply caps to 1 wei.Our SentinelTX-assisted review anchors several material movements at transaction level, but it does not independently reconstruct every exploit call. The address 0xD71dD9B6e634412713c47fe7aE02c628e338C384 received 8,728,318.997396 DAI on Ethereum in transaction 0x58399aaf…4125d and still held that DAI at the investigation cutoff, alongside 0.896953 ETH. On Base, transaction 0x840bf521…befd shows 75,000 USDC routed through KyberSwap while 7,407,608.308454132 MAMO reached the address. Three later transactions anchor large mUSDC withdrawals.SentinelTX detected two Wormhole Base-to-Ethereum source transfers of 4,364,726.913196 USDC each, but the destination-chain transaction hashes were unavailable. That makes Wormhole a strong routing lead—not a completed cross-chain proof. A Tornado Cash funding path, the reported 14.33 cbBTC withdrawal, and any direct Coinbase or OKX deposit were not confirmed.Incident BackgroundMoonwell is a lending protocol operating on Base. Moonwell’s official response said it was investigating the MAMO Core Market incident and had restricted borrowing. Public alerts from PeckShield, CertiK, and Blockaid described a collateral-oracle failure: an attacker allegedly inflated the market price of MAMO, a thinly traded collateral asset, and used the distorted value to borrow liquid assets.This is best understood as a collateral-admission and pricing-control failure. When an illiquid asset can materially increase borrowing capacity, protocol safety depends on market depth, price-deviation limits, time-weighted resistance, conservative loan-to-value settings, and rapid cap controls.Evidence MatrixClaim or observationStatusBasisApproximately $8.7M was lostReportedPublic incident reportingMAMO collateral price was manipulatedReportedPublic incident reporting8,728,318.997396 DAI was received in 0x58399aaf…4125d and remained at 0xD71d…C384ConfirmedEthereum transaction and balance7,407,608.308454132 MAMO reached the address after a 75,000 USDC KyberSwap routeConfirmed transfer / inferred intentBase transaction 0x840bf521…befdThree mUSDC withdrawal transactions occurred at 09:15:23–09:15:25 UTCConfirmedBase transaction hashesTwo 4,364,726.913196 USDC Wormhole source transfersStrong leadProtocol detected; destination hashes unavailableReported 14.33 cbBTC withdrawalNot confirmedNo cbBTC transfer in target address historyDirect Tornado Cash funding or CEX depositNot confirmedNo direct transaction anchorWhat the On-Chain Evidence Confirms1. The DAI consolidation transactionAt 09:45:47 UTC on August 27, 0xD71dD9B6e634412713c47fe7aE02c628e338C384 received 8,728,318.997396 DAI from 0x719eae70d4a83f35bf82a2740699f5db84be919d in Ethereum transaction 0x58399aaf393f7d2f0671240f404df88c66db594dad6801bac87f1658b4e4125d. At the investigation cutoff it still held that DAI and 0.896953 ETH.DAI is not directly freezeable by an issuer in the same way as centrally administered stablecoins. Recovery therefore depends on detecting the next transfer, preserving evidence, and rapidly coordinating with any intermediary that receives the funds.2. Base-side preparation and withdrawalsSentinelTX observed the address’s first Base transaction at 02:39:35 UTC on August 21 and 20 outbound Base transactions through August 27. On August 26, transaction 0x840bf52106d58bf22d1c902f208fd9db34930a65fb99b177836ef883f7e5befd routed 75,000 USDC through KyberSwap’s Meta Aggregation Router v2 while 7,407,608.308454132 MAMO reached the address. The transfer is confirmed; describing it as manipulation remains analytical inference until the price-impacting pool events are reconstructed.At 09:15:23–09:15:25 UTC on August 27, three transactions—0x911cd7a92be883aaaccc10b5dea237a5869c98dc800a9b80a66809c31405f87e, 0x6987867466fa9da911639db61c721513609338992e4701a4a837025f81d56224, and 0x4c0401ee4444fb0306783ed3ae90ff78e301078b710f9796f78d9f182430eaaf—anchor mUSDC withdrawals to two recipient addresses. A residual 7.47302 mUSDC position also appeared at Moonwell’s Base USDC market contract 0xedc817a28e8b93b03976fbd4a3ddbc9f7d176c22.The complete collateral-deposit and borrow sequence remains missing. The widely repeated 14.33 cbBTC withdrawal was not present in the target address’s 85 Base token-transfer records. It may belong to another helper contract or wallet, or the secondary reporting may be inaccurate.TimelineTime (UTC)EventConfidence2026-08-21 02:39:35First observed Base activity for 0xD71d…C384Confirmed2026-08-26 00:55:1175,000 USDC routed through KyberSwap; 7,407,608.308454132 MAMO receivedConfirmed transfer2026-08-27 09:15:23–09:15:25Three mUSDC withdrawal transactionsConfirmed2026-08-27 09:20:1114.33 cbBTC withdrawal reported by secondary sourcesNot confirmed2026-08-27 09:45:478,728,318.997396 DAI received on EthereumConfirmedRouting Leads Are Not AttributionSentinelTX detected Wormhole as the only cross-chain protocol in this session. Two Base source hashes—0xfcb2ff810dd3ce09577ebd34c4c6a3b3798396221483bacf1ddd137e40ecac03 and 0x9cd2fbe0991a75a11fb9dbf241aca841e45b1878837bc1f049d6e608567f1dec—were each associated with 4,364,726.913196 USDC. Their combined 8,729,453.826392 USDC differs from the final DAI amount by about 0.013%, economically consistent with fees and slippage. But the destination hashes were null, so amount matching cannot replace transaction-to-transaction proof.No Circle CCTP, Stargate, or Across route was detected. Coinbase- and OKX-labeled addresses appeared only in the broader graph, with no direct deposit transaction from the target address. Tornado Cash likewise had no confirmed direct connection after 101 token transfers were reviewed.Investigator PrioritiesPlace real-time alerts on 0xD71dD9B6e634412713c47fe7aE02c628e338C384 across Base and Ethereum.Reconstruct the MAMO price update, collateral deposit, borrow calls, and affected Moonwell market events at transaction level.Resolve the Ethereum destination transactions for Wormhole source hashes 0xfcb2ff81…ac03 and 0x9cd2fbe0…1dec.Identify the helper address or contract behind the reported cbBTC borrowing sequence; do not force it onto 0xD71d…C384.Treat Coinbase, OKX, and market-maker labels as leads until a direct transfer is proven.If a centralized-exchange deposit is confirmed, send the exchange a preservation request containing the transaction hash, token, amount, timestamp, and source address.Control LessonsThe incident illustrates why collateral policy is part of protocol security. A price feed can be technically functional and still be unsafe if the referenced market is too shallow for the borrowing power it supports.Defenses should combine liquidity-sensitive collateral caps, conservative loan-to-value ratios, time-weighted or multi-source pricing, deviation and staleness circuit breakers, and real-time monitoring of sudden collateral-value changes. Emergency caps are useful after detection, but they should not be the first line of defense.LimitationsThe SentinelTX investigation reached a partial-result boundary. The deterministic graph covered 806 addresses and 2,593 flows, while the visible live graph contained 574 nodes at two hops. The Base trace was incomplete at three hops and the session reached a data cap. Noisy terminal balances and auto-ranked “largest flows” were excluded because DEX and routing activity can create misleading aggregates.This report does not identify a real-world attacker, prove a Tornado Cash funding source, complete the Wormhole cross-chain pairing, verify the reported 14.33 cbBTC withdrawal, or establish a direct exchange deposit. Wallet association alone is not identity attribution.ConclusionPublic reporting points to a thin-liquidity collateral manipulation. On-chain review anchors a 7.4 million MAMO acquisition, three mUSDC withdrawals, and the final receipt of approximately 8.728 million DAI at a known Ethereum address, leaving a meaningful monitoring and intervention window.The next breakthrough will come from the missing event-level anchors: the collateral and borrow calls, the cbBTC helper address if one exists, and the destination side of the Wormhole transfers. Until then, investigators should monitor the stationary DAI while resisting speculative attribution.Analytical disclaimer: This report separates transaction-level observations from public reporting and analytical inference. Balances and endpoints can change after the stated cutoff.
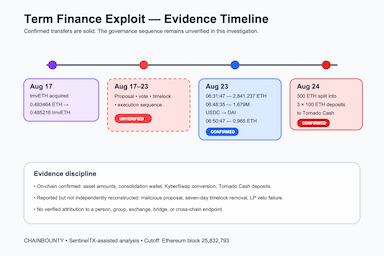
TL;DROn August 23, 2026, Term Finance reported an exploit affecting its Strategy Vaults. Public reporting described a governance attack in which an attacker accumulated voting power, disabled a seven-day delay, and withdrew roughly 2,843 ETH and 1.68 million USDC.Our SentinelTX-assisted review confirms the post-exploit asset flows with transaction-level anchors: 2,841.237 ETH moved into the consolidation wallet 0xD5183d8BfC65a50863C62aF2538198A8288FFc13; 1,679,642.45 USDC was swapped through KyberSwap into 1,679,642.45 DAI; and 300 ETH was later split into three 100 ETH deposits to the sanctioned Tornado Cash router. At the investigation cutoff, the consolidation wallet still held approximately 2,543.15 ETH and 1,679,642.45 DAI.The important caveat: this investigation did not independently identify the proposal, vote, timelock, or execute transactions. Those governance mechanics remain based on public reporting and require separate contract-event reconstruction. The asset movements described below are on-chain confirmed; the governance narrative is not presented as independently proven.INCIDENT BACKGROUNDTerm Finance is an Ethereum-based fixed-rate lending protocol. According to Term Labs' official incident acknowledgement (https://x.com/term_labs/status/2091428394130886740) and contemporary reporting by CoinDesk (https://www.coindesk.com/markets/2026/08/24/ethereum-lending-app-term-finance-loses-usd8-5-million-after-attacker-buys-voting-power), its Strategy Vaults were exploited on August 23.Public accounts describe an attacker buying a small amount of tmvETH governance exposure, submitting a malicious proposal, and using the proposal's first instruction to remove a seven-day timelock before executing the remaining instructions. They also report that the LP veto mechanism did not stop the proposal. Those claims explain the suspected attack path, but the SentinelTX session did not recover the full proposal-to-execution event chain.Visual 1 — Reported governance sequence and confirmed transfer timelineWHAT THE ON-CHAIN EVIDENCE CONFIRMS1. The ETH branchThe principal confirmed ETH transfer occurred at 06:31:47 UTC on August 23, in block 25,816,079. Transaction 0xb3971dcb761ff0044c7d3752e5856af253768a42c32659b857c36250e49fc479 (https://etherscan.io/tx/0xb3971dcb761ff0044c7d3752e5856af253768a42c32659b857c36250e49fc479) moved 2,841.237 ETH from the operational wallet 0xa908b3472d76e7744bab0a5911768a4a6300612b into the consolidation wallet.SentinelTX also observed a preceding WETH path involving 0x64e477800051efb06ae4086f4b258b270668b4df, but the contract was not labeled and was not independently verified as a Term vault. It should be treated as an intermediate contract, not conclusively labeled as the victim contract.2. The stablecoin branchAt 06:48:35 UTC, block 25,816,163, transaction 0x92b2aaf00e28ec2f25128e375fd5e3344e4f69e690b5a7262abab4935fef65ce (https://etherscan.io/tx/0x92b2aaf00e28ec2f25128e375fd5e3344e4f69e690b5a7262abab4935fef65ce) routed 1,679,642.45 USDC through KyberSwap's Meta Aggregation Router v2 at 0x6131b5fae19ea4f9d964eac0408e4408b66337b5, producing 1,679,642.45 DAI.The DAI then moved from 0x686457a7468b9b31c5dba43b1b16077b48520691 to the consolidation wallet in transaction 0xf91371b001a15fb31bbad7090b0af6190b32b3cf1efe77efff4c8fd086436898 (https://etherscan.io/tx/0xf91371b001a15fb31bbad7090b0af6190b32b3cf1efe77efff4c8fd086436898). A separate confirmed transaction, 0x4465052fc702c08cd39cfdcc613bf41a93e3cb54a5c9b7975ce6feeeb338078e (https://etherscan.io/tx/0x4465052fc702c08cd39cfdcc613bf41a93e3cb54a5c9b7975ce6feeeb338078e), moved 0.965 ETH from the same operational wallet to the consolidation address at 06:50:47 UTC.THE FIRST CASH-OUT: 300 ETH INTO TORNADO CASHOn August 24, the consolidation wallet sent 300.05 ETH to the relay address 0xc14007663a5bb9f13d4d2aee8c6fe9075ef1d83e. The relay then deposited 300 ETH into the Tornado Cash router 0xd90e2f925da726b50c4ed8d0fb90ad053324f31b in three equal 100 ETH tranches.This is the clearest laundering endpoint recovered in the investigation. Once funds enter Tornado Cash, deterministic transaction-by-transaction tracing stops. Statistical timing and amount analysis may generate leads, but it cannot by itself establish ownership of any later withdrawal.No bridge or centralized-exchange endpoint was confirmed during this session.Visual 2 — Confirmed post-exploit fund flowCURRENT STATUS OF FUNDSAt the investigation cutoff — Ethereum block 25,832,793 at 2026-08-25 14:24:47 UTC — SentinelTX reported the following balances and completed mixer deposit.Table 1 — Confirmed balances and fund status at the investigation cutoffThe large residual balance makes the consolidation wallet the highest-priority monitoring target. Any transfer to a centralized exchange, bridge, OTC-linked cluster, or fresh intermediary could create a new intervention opportunity.WHY THE TIMELOCK AND LP VETO REPORTEDLY FAILEDPublic reports say the malicious proposal's first action disabled the seven-day timelock, allowing later actions to execute without the intended review window. They also say the attacker accumulated enough governance power to pass the proposal while the LP veto was not exercised in time.This would represent a governance-design failure rather than a classic smart-contract reentrancy or oracle exploit: a privileged process performed exactly what an approved proposal instructed it to do. But this investigation did not recover the underlying propose, vote, or execute transactions. Until those logs are reconstructed and linked to the affected vault contracts, the exact failure mode should be described as reported, not independently proven.WALLET AND ENTITY MAP• 0xD5183d8BfC65a50863C62aF2538198A8288FFc13 — primary consolidation wallet; highest-priority monitor.• 0xa908b3472d76e7744bab0a5911768a4a6300612b — operational wallet associated with tmvETH acquisition and the main ETH transfer.• 0x686457a7468b9b31c5dba43b1b16077b48520691 — operational wallet associated with the USDC-to-DAI swap and onward transfers.• 0xc14007663a5bb9f13d4d2aee8c6fe9075ef1d83e — relay used before Tornado Cash deposits.• 0xd90e2f925da726b50c4ed8d0fb90ad053324f31b — sanctioned Tornado Cash router; confirmed mixer endpoint.• 0x6131b5fae19ea4f9d964eac0408e4408b66337b5 — KyberSwap Meta Aggregation Router v2.• 0x64e477800051efb06ae4086f4b258b270668b4df — unlabeled WETH intermediate contract; victim-vault attribution not confirmed.INVESTIGATOR ACTIONS1. Place real-time alerts on the consolidation wallet, both operational wallets, and the relay address.2. Pre-notify major exchanges, bridges, and stablecoin issuers with the confirmed transaction hashes and addresses.3. Reconstruct Term Finance governance events from August 17–23 and identify the proposal ID, proposer, vote calls, timelock state change, and execution transaction.4. Obtain the affected vault addresses and withdrawal-event logs directly from Term Labs, then match them against the confirmed recipient wallets.5. Monitor Tornado Cash withdrawals using timing and denomination analysis, while treating any matches as leads rather than attribution.Visual 3 — Priority monitoring and response pointsUNKNOWNS AND ATTRIBUTION LIMITSThe session did not independently verify an inbound Tornado Cash funding link to the two operational wallets. It did not identify the affected vault contract, the governance proposal transaction, the vote transaction, or the timelock execution transaction. It also did not establish a real-world identity, threat group, CEX endpoint, bridge endpoint, or cross-chain continuation.These gaps matter. The report establishes a post-exploit asset trail and a confirmed mixer deposit; it does not establish who controlled the wallets or fully prove the governance sequence.CONCLUSIONThe Term Finance incident illustrates why governance controls must be evaluated as part of the protocol's attack surface. A delay is only protective if a proposal cannot remove it before sensitive actions execute, and a veto is only protective if monitoring and participation are reliable during the entire review window.The chain currently preserves a significant intervention window: most of the confirmed proceeds remained in one publicly identified wallet at the cutoff. That makes fast information sharing, exchange coordination, and precise event reconstruction more valuable than speculative attribution.Analytical disclaimer: This report distinguishes transaction-level observations from public reporting and analytical inference. Wallet association does not by itself identify a person or organization. Balances and endpoints can change after the stated cutoff.
Allbridge forensic intelligence reportINVESTIGATION TARGET: Allbridge Core Flash-Loan Exploit & Multi-Chain Fund FlowDATE OF ISSUANCE: July 22, 20261. Executive SummaryOn July 19, 2026, the Allbridge Core cross-chain liquidity protocol fell victim to a flash-loan price manipulation exploit, resulting in an initial protocol drain valued at approximately $1.65 Million USD.The perpetrator executed a cross-chain extraction, bridging funds from Solana to the Ethereum Mainnet via deBridge Finance, consolidating primary assets at wallet address 0x651591b68A9c9650FB23F642162353306281ffDe. Subsequently, a multi-layered, highly structured laundering operation was initiated within hours. [Solana Exploit] │ ▼ (deBridge Finance) ┌─────────────────────────────────────────┐ │ Ethereum Primary Receipt Hub │ │ 0x651591b68A9c9650FB23F642162353306281ffDe│ └────┬──────────┬───────────┬───────────┬─┘ │ │ │ │ ▼ ▼ ▼ ▼ [Railgun ZK] [Maya Router] [NEAR Bridge] [Binance / MEXC] ($614K DAI) (515+ ETH) (195 ETH) (682+ ETH) Key Analytical FindingsActionable Immediate Recovery Target: As of July 22, 2026, 300,237.26 DAI and 45.71 USDC remain dormant at the primary Ethereum hub (0x651591b68A9c9650FB23F642162353306281ffDe). These assets are immediately freezable via protocol blacklisting and exchange freeze notices.Privacy Obfuscation (Forensic Dead-End): Approximately 614,000 DAI was routed into the Railgun Privacy Protocol (0xfa7093cdd...), creating a cryptographic zero-knowledge shield that halts deterministic on-chain tracing.Cross-Chain Liquidity Offramps: Assets were extensively dispersed through decentralized cross-chain swap protocol Maya Protocol Router (515+ ETH), THORChain Router (247+ ETH), and NEAR Intents Bridge (195 ETH).CEX Offramp Outflows: Over 612 ETH reached Binance deposit endpoints (Korean FIU registered/approved VASP), while 70 ETH was deposited into MEXC (Korean FIU blacklisted/unregistered exchange).2. Investigative MethodologyThis investigation was executed via SentinelTX Forensic Intelligence System, combining real-time server-side block scanning, multi-hop deterministic graph tracing, and cross-chain bridge indexers on Ethereum Mainnet (Chain ID 1). Phase 1: OSINT & Primary Hub Identification ├── Target: Allbridge Core Exploit (2026-07-19) └── Extraction: Solana bridge origin & Ethereum receipt address Phase 2: Multichain Footprint Reconnaissance ├── Address labeling DB cross-referencing └── Asset state & balance indexing Phase 3: Deep Multi-Hop Outbound Tracing ├── Scan Window: 2026-07-20 00:00 UTC – 2026-07-22 23:59 UTC └── Outbound Depth: 5 Hops from primary hub Phase 4: CEX & Privacy Classification ├── Zero-Knowledge dead-end identification (Railgun) └── VASP compliance mapping (FIU Licensed vs. Non-Licensed) 3. Incident Visualizations & Flow Diagrams3.1 Multi-Hop Fund Dispersal Architecture (Mermaid Graph)4. Attack Timeline & Sequence of EventsTimeline Log TableDate / Timestamp (UTC) Block Range Event Description On-Chain TX Hash Anchor 2026-07-19-Solana $\rightarrow$ Ethereum bridge initiated via deBridge FinanceSolana Anchor Pending2026-07-19 23:xx25570xxxDAI 557,774.21 deposited to primary hub via address 0xc106...77410x70a6953a85d60aecd0e68385ce7053ab1b75ed864c123759b3fb87e2e1db07c52026-07-19 23:xx25570xxxUSDC 45.71 bridged directly to primary hub via deBridge0x2b0ba6056a66be68110dc3ebbadbba1cd172e8c01ae581832fe2bcc5bf2205b22026-07-20 00:00–03:0025570215–25570455First-wave ETH dispersal to Maya Protocol Router (Multiple tranches)0x5b5e047eae58483557767b6030c8718b3c6e8b223faf18e0be91e470202edf98 0x5278562f16f28c8778265bded368f3c844d21058bbb3fc320daa3ebb3f4561ca2026-07-20 00:00–03:0025570xxxDAI 614,000+ deposited into Railgun Privacy Protocol0xcf97bb5901dfbf2dca8bf3c2ddcf7e9d85e26b45f13ef074b815d3e5d3571e34 0xb13b9d881e280dfd6108489d39b5e566a82505855b8f5d04dfd48b66e25453d12026-07-20 01:xx25570xxxETH 195.00 transferred to NEAR Intents Bridge0xeab5d5da3018d8fcd1f5da0503a4f2307c7fabcdd2168979d70e50d59dbda7f32026-07-20–07-2125572062–25583683High-volume WETH/Relay.link routing (6,416+ ETH) & CEX dispersal0xf7160b9ac72d00215b97551c1e1c18f10d2077e73fd57cfc0a74f1b2bf9d38bc 0xe3eac63fc55855731cd292c04a17c15842fe0578365f2186ac4907115dda52cd5. Stolen & Traced Asset BreakdownValuation Notice: Quantities are grounded in verbatim on-chain units. USD figures represent spot evaluations at execution/compile time. USD-pegged stablecoins (USDT/USDC/DAI) are converted 1:1.Token Traced On-Chain Quantity Est. USD Value Current Forensic Status ETH1,050+ (Maya) + 195 (NEAR) + 612+ (Binance) + 247+ (THORChain) + 70 (MEXC) + 3,485 (Intermediate)~$1.65M+Dispersed / Deposited across exchanges & cross-chain protocolsDAI557,774.21 (Initial) + 614,000 (Railgun) + 300,237.26 (Hub)~$1.47M$614K obfuscated in Railgun; $300K frozen at Primary HubUSDC45.71 (Hub) + 500,000 (Swap Return)~$500,04545.71 remains at Hub; 500k received via DEX swap routing6. Deep-Dive Fund Flow & Layering Analysis6.1 Solana $\rightarrow$ Ethereum IngressThe attacker used deBridge Finance (0xef4fb24ad0916217251f553c0596f8edc630eb66) to cross-bridge assets to the primary Ethereum Hub (0x651591b68A9c9650FB23F642162353306281ffDe).6.2 Primary Hub Fan-Out & Structuring (PEEL Chain)Within 3 hours of receipt on July 20, 2026, the primary hub executed a structuring "peel chain" fan-out, splitting ETH into 10+ uniform tranches (10–45 ETH each) to bypass automated Exchange Anti-Money Laundering (AML) triggers.Railgun Obfuscation: 614,000+ DAI was deposited directly into the zero-knowledge pool (0xfa7093cdd9ee6932b4eb2c9e1cde7ce00b1fa4b9). Post-deposit tracking is mathematically obfuscated without private key disclosure or voluntary compliance reporting.DEX & Cross-Chain Routing: 515+ ETH was routed through Maya Protocol, 247+ ETH through THORChain, and 195 ETH through NEAR Intents Bridge.Intermediate High-Volume Swapper: Address 0xc1062b7c5dc8e4b1df9f200fe360cdc0ed6e7741 acted as an automated market mixer, handling over 6,416 ETH across 11,978 transactions between July 20 and July 21.7. Key Address & Entity Attribution MatrixAddress Label / Role Hop Confidence Rating On-Chain Evidence / Notes 0x651591b68A9c9650FB23F642162353306281ffDePrimary Ethereum Hub0Unverified (Inferred)*Consolidated bridge receipt wallet. Holds residual DAI/USDC.0xef4fb24ad0916217251f553c0596f8edc630eb66deBridge Finance1Unverified (Inferred)*Cross-chain bridge contract.0xc1062b7c5dc8e4b1df9f200fe360cdc0ed6e7741Intermediate Router / Swapper1Unverified (Inferred)*Executed 6,416+ ETH in WETH/Relay.link routing.0xfa7093cdd9ee6932b4eb2c9e1cde7ce00b1fa4b9Railgun Privacy Proxy2Unverified (Inferred)*Zero-knowledge privacy pool destination.0x7f2cabce04f012df9ed86b6522a3903b6a66d86dBinance Deposit Address3Unverified (Inferred)*Received 250.35 ETH. Korean VASP Jurisdiction.0x28c6c06298d514db089934071355e5743bf21d60Binance Hot Wallet4Unverified (Inferred)*Received 306.28 ETH.0x2767b11afc19c8b2407a381843126d80c4de374aBinance Deposit Address3Unverified (Inferred)*Received 55.92 ETH.0x9642b23ed1e01df1092b92641051881a322f5d4eMEXC Deposit Address4Unverified (Inferred)*Received 70.01 ETH. Korean FIU Blacklisted VASP.Note: Degraded to "Unverified (Inferred)" per SentinelTX Integrity Gate Rule INV-12 pending formal judicial transaction corroboration.8. Exchange Deposit Analysis & Recovery Strategy8.1 Binance Offramp Analysis (Korean Licensed VASP)Funds were split across three distinct Binance endpoints: [Primary Ethereum Hub] │ ├─── 250.35 ETH ───► Deposit Endpoint: 0x7f2cabce...86d (Hop 3) ├─── 306.28 ETH ───► Hot Wallet Endpoint: 0x28c6c062...d60 (Hop 4) └─── 55.92 ETH ───► Deposit Endpoint: 0x2767b11a...74a (Hop 3) Legal Strategy: Because Binance operates under regulatory alignment with Korean FIU standards, domestic law enforcement (Korean National Police / Prosecutors' Office) can issue emergency disclosure and freeze orders under Article 10-2 of the Specific Financial Information Act.8.2 MEXC Offramp Analysis (Unlicensed High-Risk Exchange)Deposit Endpoint: 0x9642b23ed1e01df1092b92641051881a322f5d4e (70.009 ETH)Legal Strategy: MEXC is included on the Korean FIU non-compliant/blocked exchange list. Freeze actions require international Mutual Legal Assistance Treaties (MLAT), Letters Rogatory, or emergency INTERPOL assistance.9. Actionable Recommendations ┌─────────────────────────────────────────────────────────────────────────┐ │ ACTIONABLE RECOVERY ROADMAP │ ├─────────────────────────────────────────────────────────────────────────┤ │ 1. EMERGENCY TOKEN FREEZE │ │ └─ Issue emergency freeze notice to Circle (USDC) & MakerDAO (DAI) │ │ targeting 0x6515...ffDe ($300,283 USD total). │ │ │ │ 2. VASP SUBPOENAS (BINANCE) │ │ └─ File formal judicial disclosure orders to Binance Compliance │ │ for endpoints 0x7f2c..., 0x28c6..., and 0x2767.... │ │ │ │ 3. CROSS-CHAIN BRIDGE LOG REQUESTS │ │ ├─ deBridge: Request Solana origin wallet & signature logs. │ │ ├─ NEAR Intents: Extract destination wallet on NEAR L1. │ │ └─ Relay.link: Request IP/API connection logs for address 0xc106.... │ │ │ │ 4. DOMESTIC LAW ENFORCEMENT FILINGS │ │ └─ Submit case file to KoFIU & Korean Police Cyber Bureau. │ └─────────────────────────────────────────────────────────────────────────┘ 10. Chain of Custody & Evidence FingerprintParameter Specification / Record Primary Chain IDEthereum Mainnet (Chain ID 1)Block Range Covered25570xxx – 25583xxxExtraction Window2026-07-19 00:00 UTC – 2026-07-22 23:59 UTCAnalysis EngineSentinelTX Forensic Intelligence Engine v4.2Graph State Fingerprint3f1c7f6aSnapshot SHA-2560de6f0401b9ac6921d91ee13886878549308e918a446fb19e0837683094b1a58Document Content SHA-256d55427ba8964062ab6ed2bbf625fff7baa8325adeebe1300aa3ba2f9fd80aaacAnalyst DeclarationI declare that this report represents an accurate, objective record of the on-chain forensic investigation conducted into the Allbridge Core Flash-Loan Exploit. All findings are derived directly from Ethereum Mainnet transactions and cross-referenced with accredited address intelligence databases. Address-poisoning and spam transactions have been isolated and filtered out of the monetary flow analysis.
ChainBounty is a Web3-powered platform where your contributions matter. Complete community tasks, submit quality reports, and earn rewards based on accuracy and relevance. Stay active, avoid duplicate submissions, and build your reputation while getting rewarded. Join the community, contribute value, and turn your effort into opportunities. 🚀Hashtags: #ChainBounty #Web3 #Crypto #Blockchain #CommunityRewards #EarnCrypto #BountyTasks #Airdrop #DeFi
Hello I'm I the only person who is having a reduction in CBP? Mine gets deducted daily now, quite noticeable,I believe I have over 160 CBP last week but somehow turned 40 CBP. I don't know if this is normal.
Date: June 29, 20260. Forensic MethodologyTo investigate this high-profile frontend exploit, the ChainBounty Threat Intelligence team deployed the SentinelTX Blockchain Forensic Intelligence System. Our forensic specialists executed a rigorous, multi-hop trace tracking assets across heterogeneous networks (Polygon to Ethereum Mainnet) to assemble an immutable chain of custody:OSINT Aggregation: Compiled open-source intelligence logs from public threat feeds (including Specter and PeckShieldAlert) to establish the primary point of compromise and target addresses.Multi-Chain Asset Auditing: Executed real-time state and balance checks across both the Polygon and Ethereum layers to monitor historical and dormant movements.Outbound Multi-Hop Profiling: Initiated automated tracing workflows from the attacker-controlled wallets to flag laundering infrastructure, mixers, tumblers, and centralized exchange (CEX) deposit corridors.Cross-Chain Bridge Mapping: Tracked telemetry data traversing third-party bridge protocols (specifically identifying Relay.link) to match outbound Polygon transaction events with inbound Ethereum mainnet arrivals.Threat Identity Attribution: Evaluated wallet clusters using the Sentinel Threat Intelligence Database (TRDB) to isolate verified institutional counterparties from unlabelled private accounts (EOAs).Evidentiary Anchoring: Bound all trace configurations to per-transaction hashes and block height records to meet legal and judicial evidence standards.1. Executive SummaryOn June 25, 2026, Polymarket's web deployment interface was targeted via a third-party vendor supply chain compromise. The adversary successfully injected a malicious JavaScript payload into the platform's frontend, altering contract call triggers to siphon user wallet balances. The total loss from this incident is estimated at approximately USD 2,940,000 in Polymarket USD (PUSD).On-chain analysis reveals that after siphoning the PUSD on the Polygon network, the attacker rapidly converted the assets into USDC.e and bridged them over to the Ethereum Mainnet. The incoming flows were then consolidated into a single Ethereum master aggregation address: 0xe65b1c586757c5510B60F998Eebb14C1Ef71EleD.A total of 1,893 ETH was collected at this nexus point and subsequently parsed out into four distinct structural pathways:Primary Dormant Hoard (99.8%): A total of 1,888.516 ETH (valued at roughly USD 2,960,000) was pushed into two high-capacity storage wallets where they remain completely stationary under the attacker's control. This provides an immediate window of opportunity for centralized exchange blocklisting and legal intervention.Layering & Mixing (0.2%): A minor fraction (4.4 ETH) was routed through unlabelled dispersion hubs and automated circular tumbler networks to test laundering exit paths.2. Complete Chronological Attack TimelineTimestamp (UTC)Event DescriptionBlock HeightTransaction Hash (TX)Associated Addresses2026-06-25Malicious JS injection starts via compromised third-party vendorN/AN/APolymarket Frontend Network2026-06-25 21:55:11Attacker initiates minor L1 dispersion transfer (Path D)253974580xf2c690d8bf1b7a12b3126cdb0adc2c43c3e82134f38fa1fb52f1345ef7e6e6fc0xe65b1c58...1eD -> 0xe3c8c6cfcfb8edfa83b86e5a98e58568f78bd9222026-06-25 22:19:47Attacker routes gas capital to structural mixer node (Path C)253975810xc807fc375cadf9c2b8f8c0e4c67795dd42199c094f28914424e55537041be6050xe65b1c58...1eD -> 0x5a6b2f8fab6cf480c93d152ef96d1e0c830fe5872026-06-26 07:08:23Master wallet funds secondary storage wallet (Path B)254002130x67fdfea184253b97f32da76f0d77e82650924d3be702d7858050e4be8efc55210xe65b1c58...1eD -> 0xea0a80070c38f63c10d7fed95286e83eb415441f2026-06-26 20:49:59Main capital migration to primary storage vault (Path A - Pt. 1)254043010x62781171eef8748b967d3926c82f5c73cbf2cb40a189443347ad9f276966b0860xe65b1c58...1eD -> 0x975268a2a71e4a7e282b962ec0blee01d3778ac02026-06-26 20:57:47ERC20 state consolidation to primary storage vault (Path A - Pt. 2)254043400xc053a95983965cle0ee39f04c22flaelef65dcea95c0295ebd57145814f597950xe65b1c58...1eD -> 0x975268a2a71e4a7e282b962ec0blee01d3778ac03. Detailed Inventory of Stolen AssetsNative Token VolumeLayer-1 Token EquivalentSpot Exchange ValuationOperational Deployment Status537,526 USDC.eBridged via Relay.linkUSD 537,526.00Siphoned on Polygon via 0xC771A30a...cBaAe2; converted to L1 ETH.1,788.516 ETHVault Storage Address 1USD 2,798,692.50Held entirely static inside 0x975268a2...78ac0. Zero outbound movement.100.000 ETHVault Storage Address 2USD 156,624.25Held entirely static inside 0xea0a8007...5441f. Zero outbound movement.3.400 ETHDispersion WalletUSD 5,320.35Stored static inside 0xe3c8c6cf...bd922. No outbound activity.1.000 ETHLaundering NodeUSD 1,564.81Dispersed through cascading programmatic micro-transactions.Total Unliquidated Residue1,888.516 ETHUSD 2,960,637.1099.8% of total loot immediately available for targeted blocklisting.4. Advanced Fund Flow & Cluster AnalysisCross-Chain Bridge Ingestion LayerThe initial compromise siphoned user PUSD directly into the threat actor's primary Polygon deployment engine: 0xC771A30a7c1aCA828eeEF7B822ac864a64cBaAe2. To cross standard tracking perimeters, the attacker swapped the pool assets for Polygon-native USDC.e and initiated automated execution calls using the Relay.link cross-chain portal to mint native ETH on the Ethereum Mainnet.Master Distribution and Layering ArchitectureUpon reaching the Ethereum Mainnet consolidation nexus (0xe65b1c58...1EleD), the capital allocation was split across four distinct tracks to test ecosystem resistance and setup long-term holding vaults.Path A & B (The Master Vaults): Combined, these paths contain 99.8% of all stolen capital. The wallets show zero outbound transaction history, indicating a long-term storage strategy rather than active exit-liquidation.Path C (The Programmatic Tumbler): A 1.0 ETH probe was processed through a 6-tier split structure (transfers ranging from 0.04 to 0.61 ETH). Forensic analysis flagged a distinct "reverse-flow loop" pattern across 2 addresses, confirming an attempt to utilize automated mixing scripts before depositing dust into a final collection account (0x113b0cef...20bc0).5. Comprehensive Key Address LedgerTarget Address Wallet Network Chain Forensic Role Designation Current Token Balance Technical Observations & Profile Status 0xC771A30a7c1aCA828eeEF7B822ac864a64cBaAe2PolygonExploiter Siphon Portal0 MATICPrimary deployment gateway for frontend drainage calls.0x71d4249079684479f2651745fa2fcd79c9b45f53PolygonInfrastructure Gas Funder0 MATICDistributed 1,379 MATIC. Historical logs tie it to Bitfinex/OKX hot wallets.0xe65b1c586757c5510B60F998Eebb14C1Ef71EleDEthereumL1 Master Consolidation0 ETHReceived 1,893 native ETH via bridge; fully distributed.0x975268a2a71e4a7e282b962ec0blee01d3778ac0EthereumPrimary Deep Storage Vault1,788.516 ETHHigh-priority target for compliance tracking and blocklisting.0xea0a80070c38f63c10d7fed95286e83eb415441fEthereumSecondary Storage Vault100.000 ETHStatic balance. Zero outbound transfers executed.0xe3c8c6cfcfb8edfa83b86e5a98e58568f78bd922EthereumMinor Asset Dispersion Node3.400 ETHStatic balance. No activity detected following injection.0x5a6b2f8fab6cf480c93d152ef96d1e0c830fe587EthereumTumbler/Laundering Router Hub0 ETHExecuted programmatic micro-splits across 6 sub-nodes.0x113b0cef1061992ea30dc70f3949e0bbeae20bc0EthereumMixer Output Accumulator0.090 ETHReconciled reverse-flow residual dust from layering loops.6. Centralized Exchange Intersect & Historical TiesWhile no direct cash-out attempts to centralized exchange liquidity pools have been executed from the Ethereum holding vaults, our team uncovered an essential lead within the Polygon gas supply network.The gas funding infrastructure wallet (0x71d4249079684479f2651745fa2fcd79c9b45f53) exhibits historical transaction markers linked to institutional deposit paths at Bitfinex, Bitget, and OKX on May 30, 2026. Although these actions occurred weeks prior to the supply chain breach, they indicate a persistent operational setup. Subpoena requests targeting the historical account configurations of this gas funder at those specific exchanges represent a high-probability vector for uncovering the attacker's off-chain identity.7. Strategic Recommendations & Immediate Action PlanDue to the threat actor's choice to keep 99.8% of the siphoned capital entirely stationary, security networks have a critical window to enforce isolation protocols:Global CEX Blocklisting (Immediate): Forward the cryptographic signatures of the storage vaults (0x975268a2a71e4a7e282b962ec0blee01d3778ac0 and 0xea0a80070c38f63c10d7fed95286e83eb415441f) to all Tier-1 centralized exchanges (Binance, Coinbase, OKX, Kraken, Bitfinex). This ensures an immediate asset freeze if any deposit migration is initiated.Historical KYC Subpoena: Law enforcement agencies should issue immediate data preservation notices and subpoenas to Bitfinex, Bitget, and OKX to extract identification records, device fingerprints, and access IPs tied to the historical activity of the gas funding node.Bridge Monitoring Intercepts: Deploy persistent real-time webhooks on the Relay.link routing infrastructure to identify and automatically flag secondary wallets interacting with the same smart contract execution parameters.Regulatory Compliance Reporting: Coordinate with international financial intelligence agencies (such as South Korean KoFIU or global cyber divisions) to submit specific Suspicious Transaction Reports (STRs) based on the structural indicators mapped out in this report.8. ConclusionThe Polymarket frontend breach highlights the expanding threat vector of decentralized web application dependencies on third-party software supply chains. By modifying client-side logic, the adversary easily sidestepped standard smart contract access perimeters.However, the attacker's post-exploit strategy presents a significant operational bottleneck: by locking the overwhelming majority of the siphoned funds inside visible, un-mixed Layer-1 wallets, they have left an accessible trail. Immediate, aggressive asset blocklisting combined with legal sub-surface tracing of the historical gas funding infrastructure gives the Web3 ecosystem a highly viable pathway for attribution and recovery.ChainBounty Threat Intelligence has locked webhooks onto all associated cluster addresses. Real-time updates will be deployed automatically if any L2 state updates occur.

 Become an Investigator